Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

ECCouncil Updated 312-50v12 Exam Questions and Answers by khalid

Page: 32 / 42

ECCouncil 312-50v12 Exam Overview :

Exam Name: Certified Ethical Hacker Exam (CEHv12)
Exam Code: 312-50v12 Dumps
Vendor: ECCouncil Certification: CEH v12
Questions: 572 Q&A's Shared By: khalid
Question 128

The establishment of a TCP connection involves a negotiation called three-way handshake. What type of message does the client send to the server in order to begin this negotiation?

Options:

A.

ACK

B.

SYN

C.

RST

D.

SYN-ACK

Discussion
Question 129

Study the following log extract and identify the attack.
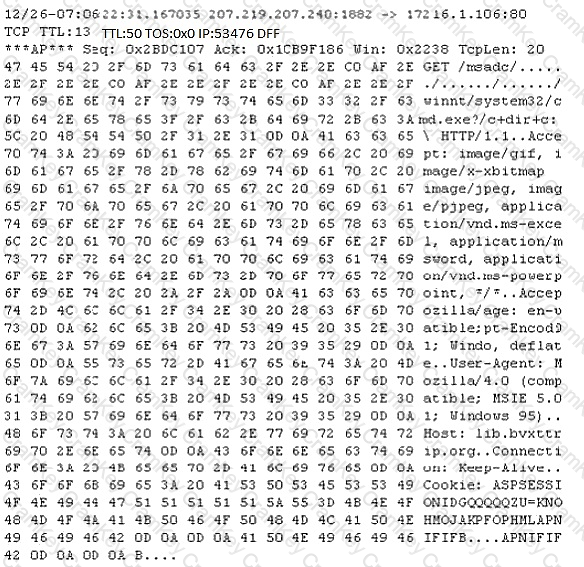
Questions 129

Options:

A.

Hexcode Attack

B.

Cross Site Scripting

C.

Multiple Domain Traversal Attack

D.

Unicode Directory Traversal Attack

Discussion
Miriam
Highly recommended Dumps. 100% authentic and reliable. Passed my exam with wonderful score.
Milan Aug 14, 2026
I see. Thanks for the information. I'll definitely keep Cramkey in mind for my next exam.
Norah
Cramkey is highly recommended.
Zayan Aug 17, 2026
Definitely. If you're looking for a reliable and effective study resource, look no further than Cramkey Dumps. They're simply wonderful!
Miley
Hey, I tried Cramkey Dumps for my IT certification exam. They are really awesome and helped me pass my exam with wonderful score.
Megan Aug 15, 2026
That’s great!!! I’ll definitely give it a try. Thanks!!!
Melody
My experience with Cramkey was great! I was surprised to see that many of the questions in my exam appeared in the Cramkey dumps.
Colby Aug 8, 2026
Yes, In fact, I got a score of above 85%. And I attribute a lot of my success to Cramkey's dumps.
Question 130

Which system consists of a publicly available set of databases that contain domain name registration contact information?

Options:

A.

WHOIS

B.

CAPTCHA

C.

IANA

D.

IETF

Discussion
Question 131

An attacker has installed a RAT on a host. The attacker wants to ensure that when a user attempts to go to "www.MyPersonalBank.com ", the user is directed to a phishing site.

Which file does the attacker need to modify?

Options:

A.

Boot.ini

B.

Sudoers

C.

Networks

D.

Hosts

Discussion
Page: 32 / 42
Title
Questions
Posted

312-50v12
PDF

$36.75  $104.99

312-50v12 Testing Engine

$43.75  $124.99

312-50v12 PDF + Testing Engine

$57.75  $164.99

