Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

ECCouncil Updated 312-50v12 Exam Questions and Answers by serenity

Page: 6 / 42

ECCouncil 312-50v12 Exam Overview :

Exam Name: Certified Ethical Hacker Exam (CEHv12)
Exam Code: 312-50v12 Dumps
Vendor: ECCouncil Certification: CEH v12
Questions: 572 Q&A's Shared By: serenity
Question 24

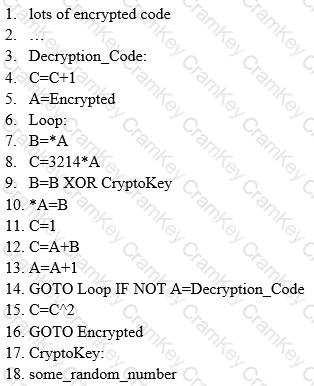
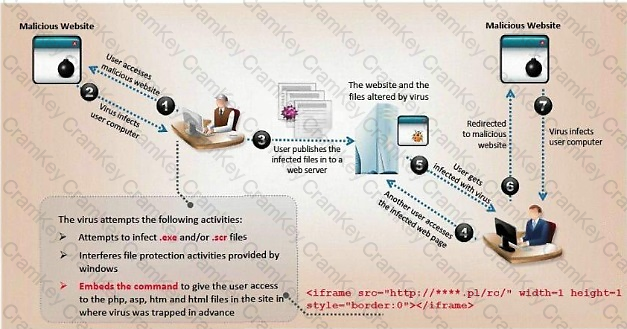
ViruXine.W32 virus hides their presence by changing the underlying executable code.

This Virus code mutates while keeping the original algorithm intact, the code changes itself each time it runs, but the function of the code (its semantics) will not change at all.
Questions 24

Here is a section of the Virus code:

Questions 24

What is this technique called?

Options:

A.

Polymorphic Virus

B.

Metamorphic Virus

C.

Dravidic Virus

D.

Stealth Virus

Discussion
Freddy
I passed my exam with flying colors and I'm confident who will try it surely ace the exam.
Aleksander Aug 3, 2026
Thanks for the recommendation! I'll check it out.
Sarah
Yeah, I was so relieved when I saw that the question appeared in the exam were similar to their exam dumps. It made the exam a lot easier and I felt confident going into it.
Aaliyah Aug 28, 2026
Same here. I've heard mixed reviews about using exam dumps, but for us, it definitely paid off.
Stefan
Thank you so much Cramkey I passed my exam today due to your highly up to date dumps.
Ocean Aug 6, 2026
Agree….Cramkey Dumps are constantly updated based on changes in the exams. They also have a team of experts who regularly review the materials to ensure their accuracy and relevance. This way, you can be sure you're studying the most up-to-date information available.
Peyton
Hey guys. Guess what? I passed my exam. Thanks a lot Cramkey, your provided information was relevant and reliable.
Coby Aug 10, 2026
Thanks for sharing your experience. I think I'll give Cramkey a try for my next exam.
Question 25

Ethical hacker jane Smith is attempting to perform an SQL injection attach. She wants to test the response time of a true or false response and wants to use a second command to determine whether the database will return true or false results for user IDs. which two SQL Injection types would give her the results she is looking for?

Options:

A.

Out of band and boolean-based

B.

Time-based and union-based

C.

union-based and error-based

D.

Time-based and boolean-based

Discussion
Question 26

A friend of yours tells you that he downloaded and executed a file that was sent to him by a coworker. Since the file did nothing when executed, he asks you for help because he suspects that he may have installed a trojan on his computer.

what tests would you perform to determine whether his computer Is Infected?

Options:

A.

Use ExifTool and check for malicious content.

B.

You do not check; rather, you immediately restore a previous snapshot of the operating system.

C.

Upload the file to VirusTotal.

D.

Use netstat and check for outgoing connections to strange IP addresses or domains.

Discussion
Question 27

Allen, a professional pen tester, was hired by xpertTech solutWns to perform an attack simul-ation on the organization's network resources. To perform the attack, he took advantage of the NetBIOS API and targeted the NetBIOS service. B/enumerating NetBIOS, he found that port 139 was open and could see the resources that could be accessed or viewed on a remote system. He came across many NetBIOS codes during enumeration.

identify the NetBIOS code used for obtaining the messenger service running for the logged-in user?

Options:

A.

<1B>

B.

<00>

C.

<03>

D.

<20>

Discussion
Page: 6 / 42
Title
Questions
Posted

312-50v12
PDF

$36.75  $104.99

312-50v12 Testing Engine

$43.75  $124.99

312-50v12 PDF + Testing Engine

$57.75  $164.99