Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

ECCouncil Updated 312-50v12 Exam Questions and Answers by yuvraj

Page: 39 / 42

ECCouncil 312-50v12 Exam Overview :

Exam Name: Certified Ethical Hacker Exam (CEHv12)
Exam Code: 312-50v12 Dumps
Vendor: ECCouncil Certification: CEH v12
Questions: 572 Q&A's Shared By: yuvraj
Question 156

Which of the following tools can be used for passive OS fingerprinting?

Options:

A.

nmap

B.

tcpdump

C.

tracert

D.

ping

Discussion
Question 157

Which mode of IPSec should you use to assure security and confidentiality of data within the same LAN?

Options:

A.

ESP transport mode

B.

ESP confidential

C.

AH permiscuous

D.

AH Tunnel mode

Discussion
Hendrix
Great website with Great Exam Dumps. Just passed my exam today.
Luka Sep 6, 2026
Absolutely. Cramkey Dumps only provides the latest and most updated exam questions and answers.
Miriam
Highly recommended Dumps. 100% authentic and reliable. Passed my exam with wonderful score.
Milan Sep 19, 2026
I see. Thanks for the information. I'll definitely keep Cramkey in mind for my next exam.
Honey
I highly recommend it. They made a big difference for me and I'm sure they'll help you too. Just make sure to use them wisely and not solely rely on them. They should be used as a supplement to your regular studies.
Antoni Sep 12, 2026
Good point. Thanks for the advice. I'll definitely keep that in mind.
Zayaan
Successfully aced the exam… Thanks a lot for providing amazing Exam Dumps.
Harmony Sep 16, 2026
That's fantastic! I'm glad to hear that their dumps helped you. I also used them and found it accurate.
Question 158

Eve is spending her day scanning the library computers. She notices that Alice is using a computer whose port 445 is active and listening. Eve uses the ENUM tool to enumerate Alice machine. From the command prompt, she types the following command.
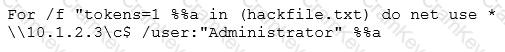
Questions 158

What is Eve trying to do?

Options:

A.

Eve is trying to connect as a user with Administrator privileges

B.

Eve is trying to enumerate all users with Administrative privileges

C.

Eve is trying to carry out a password crack for user Administrator

D.

Eve is trying to escalate privilege of the null user to that of Administrator

Discussion
Question 159

An attacker, using a rogue wireless AP, performed an MITM attack and injected an HTML code to embed a malicious applet in all HTTP connections.

When users accessed any page, the applet ran and exploited many machines. Which one of the following tools the hacker probably used to inject HTML code?

Options:

A.

Wireshark

B.

Ettercap

C.

Aircrack-ng

D.

Tcpdump

Discussion
Page: 39 / 42
Title
Questions
Posted

312-50v12
PDF

$36.75  $104.99

312-50v12 Testing Engine

$43.75  $124.99

312-50v12 PDF + Testing Engine

$57.75  $164.99

