Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

ECCouncil Updated 312-50v12 Exam Questions and Answers by nela

Page: 13 / 42

ECCouncil 312-50v12 Exam Overview :

Exam Name: Certified Ethical Hacker Exam (CEHv12)
Exam Code: 312-50v12 Dumps
Vendor: ECCouncil Certification: CEH v12
Questions: 572 Q&A's Shared By: nela
Question 52

infecting a system with malware and using phishing to gain credentials to a system or web application are examples of which phase of the ethical hacking methodology?

Options:

A.

Reconnaissance

B.

Maintaining access

C.

Scanning

D.

Gaining access

Discussion
Ari
Can anyone explain what are these exam dumps and how are they?
Ocean Oct 9, 2026
They're exam preparation materials that are designed to help you prepare for various certification exams. They provide you with up-to-date and accurate information to help you pass your exams.
Alaya
Best Dumps among other dumps providers. I like it so much because of their authenticity.
Kaiden Oct 22, 2026
That's great. I've used other dump providers in the past and they were often outdated or had incorrect information. This time I will try it.
Neve
Will I be able to achieve success after using these dumps?
Rohan Oct 26, 2026
Absolutely. It's a great way to increase your chances of success.
Mariam
Do anyone think Cramkey questions can help improve exam scores?
Katie Oct 8, 2026
Absolutely! Many people have reported improved scores after using Cramkey Dumps, and there are also success stories of people passing exams on the first try. I already passed this exam. I confirmed above questions were in exam.
Madeleine
Passed my exam with my dream score…. Guys do give these dumps a try. They are authentic.
Ziggy Oct 17, 2026
That's really impressive. I think I might give Cramkey Dumps a try for my next certification exam.
Question 53

A newly joined employee. Janet, has been allocated an existing system used by a previous employee. Before issuing the system to Janet, it was assessed by Martin, the administrator. Martin found that there were possibilities of compromise through user directories, registries, and other system parameters. He also Identified vulnerabilities such as native configuration tables, incorrect registry or file permissions, and software configuration errors. What is the type of vulnerability assessment performed by Martin?

Options:

A.

Credentialed assessment

B.

Database assessment

C.

Host-based assessment

D.

Distributed assessment

Discussion
Question 54

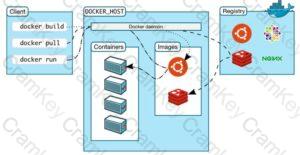
Annie, a cloud security engineer, uses the Docker architecture to employ a client/server model in the application she is working on. She utilizes a component that can process API requests and handle various Docker objects, such as containers, volumes. Images, and networks. What is the component of the Docker architecture used by Annie in the above scenario?

Options:

A.

Docker client

B.

Docker objects

C.

Docker daemon

D.

Docker registries

Discussion
Question 55

Vlady works in a fishing company where the majority of the employees have very little understanding of IT let alone IT Security. Several information security issues that Vlady often found includes, employees sharing password, writing his/her password on a post it note and stick it to his/her desk, leaving the computer unlocked, didn’t log out from emails or other social media accounts, and etc.

After discussing with his boss, Vlady decided to make some changes to improve the security environment in his company. The first thing that Vlady wanted to do is to make the employees understand the importance of keeping confidential information, such as password, a secret and they should not share it with other persons.

Which of the following steps should be the first thing that Vlady should do to make the employees in his company understand to importance of keeping confidential information a secret?

Options:

A.

Warning to those who write password on a post it note and put it on his/her desk

B.

Developing a strict information security policy

C.

Information security awareness training

D.

Conducting a one to one discussion with the other employees about the importance of information security

Discussion
Page: 13 / 42
Title
Questions
Posted

312-50v12
PDF

$38.5  $109.99

312-50v12 Testing Engine

$45.5  $129.99

312-50v12 PDF + Testing Engine

$59.5  $169.99