Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

ECCouncil Updated 312-50v12 Exam Questions and Answers by arran

Page: 2 / 42

ECCouncil 312-50v12 Exam Overview :

Exam Name: Certified Ethical Hacker Exam (CEHv12)
Exam Code: 312-50v12 Dumps
Vendor: ECCouncil Certification: CEH v12
Questions: 572 Q&A's Shared By: arran
Question 8

Jason, an attacker, targeted an organization to perform an attack on its Internet-facing web server with the intention of gaining access to backend servers, which are protected by a firewall. In this process, he used a URL https://xyz.com/feed.php?url:externaIsile.com/feed/to to obtain a remote feed and altered the URL input to the local host to view all the local resources on the target server. What is the type of attack Jason performed In the above scenario?

Options:

A.

website defacement

B.

Server-side request forgery (SSRF) attack

C.

Web server misconfiguration

D.

web cache poisoning attack

Discussion
Ivan
I tried these dumps for my recent certification exam and I found it pretty helpful.
Elis Oct 16, 2026
Agree!!! The questions in the dumps were quite similar to what came up in the actual exam. It gave me a good idea of the types of questions to expect and helped me revise efficiently.
Teddie
yes, I passed my exam with wonderful score, Accurate and valid dumps.
Isla-Rose Oct 28, 2026
Absolutely! The questions in the dumps were almost identical to the ones that appeared in the actual exam. I was able to answer almost all of them correctly.
Sarah
Yeah, I was so relieved when I saw that the question appeared in the exam were similar to their exam dumps. It made the exam a lot easier and I felt confident going into it.
Aaliyah Oct 28, 2026
Same here. I've heard mixed reviews about using exam dumps, but for us, it definitely paid off.
Josephine
I want to ask about their study material and Customer support? Can anybody guide me?
Zayd Oct 24, 2026
Yes, the dumps or study material provided by them are authentic and up to date. They have a dedicated team to assist students and make sure they have a positive experience.
Question 9

George is a security professional working for iTech Solutions. He was tasked with securely transferring sensitive data of the organization between industrial systems. In this process, he used a short-range communication protocol based on the IEEE 203.15.4 standard. This protocol is used in devices that transfer data infrequently at a low rate in a restricted area, within a range of 10-100 m. What is the short-range wireless communication technology George employed in the above scenario?

Options:

A.

MQTT

B.

LPWAN

C.

Zigbee

D.

NB-IoT

Discussion
Question 10

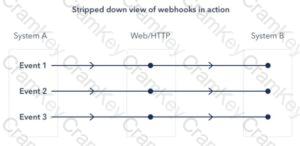
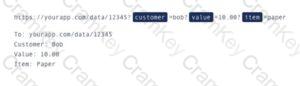
Susan, a software developer, wants her web API to update other applications with the latest information. For this purpose, she uses a user-defined HTTP tailback or push APIs that are raised based on trigger events: when invoked, this feature supplies data to other applications so that users can instantly receive real-time Information.

Which of the following techniques is employed by Susan?

Options:

A.

web shells

B.

Webhooks

C.

REST API

D.

SOAP API

Discussion
Question 11

At what stage of the cyber kill chain theory model does data exfiltration occur?

Options:

A.

Actions on objectives

B.

Weaponization

C.

installation

D.

Command and control

Discussion
Page: 2 / 42
Title
Questions
Posted

312-50v12
PDF

$27.5  $109.99

312-50v12 Testing Engine

$32.5  $129.99

312-50v12 PDF + Testing Engine

$42.5  $169.99