Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

CompTIA Updated CAS-004 Exam Questions and Answers by ruairi

Page: 14 / 46

CompTIA CAS-004 Exam Overview :

Exam Name: CompTIA SecurityX Certification Exam
Exam Code: CAS-004 Dumps
Vendor: CompTIA Certification: CompTIA CASP
Questions: 619 Q&A's Shared By: ruairi
Question 56

A security engineer was auditing an organization’s current software development practice and discovered that multiple open-source libraries were Integrated into the organization’s software. The organization currently performs SAST and DAST on the software it develops.

Which of the following should the organization incorporate into the SDLC to ensure the security of the open-source libraries?

Options:

A.

Perform additional SAST/DAST on the open-source libraries.

B.

Implement the SDLC security guidelines.

C.

Track the library versions and monitor the CVE website for related vulnerabilities.

D.

Perform unit testing of the open-source libraries.

Discussion
Question 57

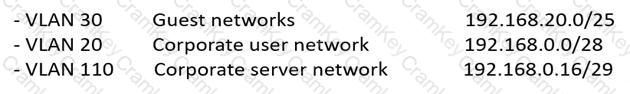
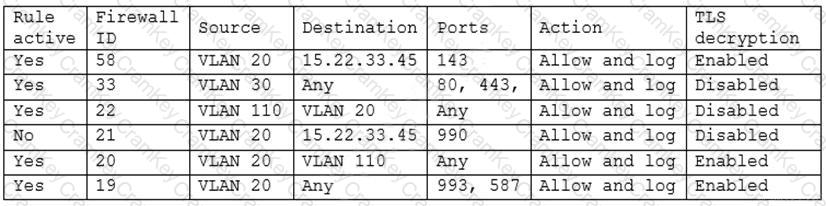
A security engineer has been asked to close all non-secure connections from the corporate network. The engineer is attempting to understand why the corporate UTM will not allow users to download email via IMAPS. The engineer formulates a theory and begins testing by creating the firewall ID 58, and users are able to download emails correctly by using IMAP instead. The network comprises three VLANs:
Questions 57

The security engineer looks at the UTM firewall rules and finds the following:
Questions 57

Which of the following should the security engineer do to ensure IMAPS functions properly on the corporate user network?

Options:

A.

Contact the email service provider and ask if the company IP is blocked.

B.

Confirm the email server certificate is installed on the corporate computers.

C.

Make sure the UTM certificate is imported on the corporate computers.

D.

Create an IMAPS firewall rule to ensure email is allowed.

Discussion
Question 58

An application server was recently upgraded to prefer TLS 1.3, and now users are unable to connect their clients to the server. Attempts to reproduce the error are confirmed, and clients are reporting the following:

ERR_SSL_VERSION_OR_CIPHER_MISMATCH

Which of the following is MOST likely the root cause?

Options:

A.

The client application is testing PFS.

B.

The client application is configured to use ECDHE.

C.

The client application is configured to use RC4.

D.

The client application is configured to use AES-256 in GCM.

Discussion
Kylo
What makes Cramkey Dumps so reliable? Please guide.
Sami Oct 20, 2026
Well, for starters, they have a team of experts who are constantly updating their material to reflect the latest changes in the industry. Plus, they have a huge database of questions and answers, which makes it easy to study and prepare for the exam.
Ava-Rose
Yes! Cramkey Dumps are amazing I passed my exam…Same these questions were in exam asked.
Ismail Oct 15, 2026
Wow, that sounds really helpful. Thanks, I would definitely consider these dumps for my certification exam.
Carson
Yeah, definitely. I would definitely recommend Cramkey Dumps to anyone who is preparing for an exam.
Rufus Oct 9, 2026
Me too. They're a lifesaver!
Josie
I just passed my certification exam using their dumps and I must say, I was thoroughly impressed.
Fatimah Oct 19, 2026
You’re right. The dumps were authentic and covered all the important topics. I felt confident going into the exam and it paid off.
Honey
I highly recommend it. They made a big difference for me and I'm sure they'll help you too. Just make sure to use them wisely and not solely rely on them. They should be used as a supplement to your regular studies.
Antoni Oct 16, 2026
Good point. Thanks for the advice. I'll definitely keep that in mind.
Question 59

An organization is referencing NIST best practices for BCP creation while reviewing current internal organizational processes for mission-essential items.

Which of the following phases establishes the identification and prioritization of critical systems and functions?

Options:

A.

Review a recent gap analysis.

B.

Perform a cost-benefit analysis.

C.

Conduct a business impact analysis.

D.

Develop an exposure factor matrix.

Discussion
Page: 14 / 46
Title
Questions
Posted

CAS-004
PDF

$31.5  $104.99

CAS-004 Testing Engine

$37.5  $124.99

CAS-004 PDF + Testing Engine

$49.5  $164.99

