Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

CompTIA Updated CAS-004 Exam Questions and Answers by zoey

Page: 17 / 46

CompTIA CAS-004 Exam Overview :

Exam Name: CompTIA SecurityX Certification Exam
Exam Code: CAS-004 Dumps
Vendor: CompTIA Certification: CompTIA CASP
Questions: 619 Q&A's Shared By: zoey
Question 68

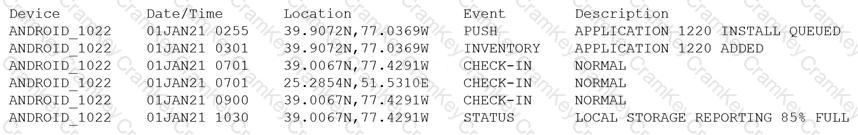
Device event logs sources from MDM software as follows:
Questions 68

Which of the following security concerns and response actions would BEST address the risks posed by the device in the logs?

Options:

A.

Malicious installation of an application; change the MDM configuration to remove application ID 1220.

B.

Resource leak; recover the device for analysis and clean up the local storage.

C.

Impossible travel; disable the device’s account and access while investigating.

D.

Falsified status reporting; remotely wipe the device.

Discussion
Question 69

A company wants to protect its intellectual property from theft. The company has already applied ACLs and DACs.

Which of the following should the company use to prevent data theft?

Options:

A.

Watermarking

B.

DRM

C.

NDA

D.

Access logging

Discussion
Annabel
I recently used them for my exam and I passed it with excellent score. I am impressed.
Amirah Aug 13, 2026
I passed too. The questions I saw in the actual exam were exactly the same as the ones in the Cramkey Dumps. I was able to answer the questions confidently because I had already seen and studied them.
Cecilia
Yes, I passed my certification exam using Cramkey Dumps.
Helena Aug 19, 2026
Great. Yes they are really effective
Honey
I highly recommend it. They made a big difference for me and I'm sure they'll help you too. Just make sure to use them wisely and not solely rely on them. They should be used as a supplement to your regular studies.
Antoni Aug 3, 2026
Good point. Thanks for the advice. I'll definitely keep that in mind.
Walter
Yayyy!!! I passed my exam with the help of Cramkey Dumps. Highly appreciated!!!!
Angus Aug 5, 2026
YES….. I saw the same questions in the exam.
Question 70

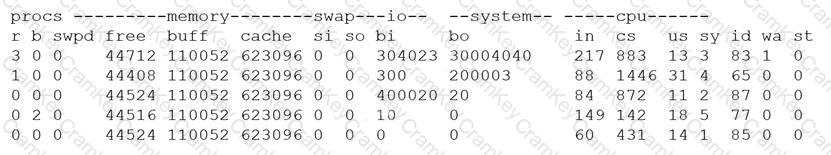
A security analyst is concerned that a malicious piece of code was downloaded on a Linux system. After some research, the analyst determines that the suspected piece of code is performing a lot of input/output (I/O) on the disk drive.
Questions 70

Based on the output above, from which of the following process IDs can the analyst begin an investigation?

Options:

A.

65

B.

77

C.

83

D.

87

Discussion
Question 71

A threat hunting team receives a report about possible APT activity in the network.

Which of the following threat management frameworks should the team implement?

Options:

A.

NIST SP 800-53

B.

MITRE ATT&CK

C.

The Cyber Kill Chain

D.

The Diamond Model of Intrusion Analysis

Discussion
Page: 17 / 46
Title
Questions
Posted

CAS-004
PDF

$36.75  $104.99

CAS-004 Testing Engine

$43.75  $124.99

CAS-004 PDF + Testing Engine

$57.75  $164.99

