Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

CompTIA Updated CAS-004 Exam Questions and Answers by juno

Page: 8 / 46

CompTIA CAS-004 Exam Overview :

Exam Name: CompTIA SecurityX Certification Exam
Exam Code: CAS-004 Dumps
Vendor: CompTIA Certification: CompTIA CASP
Questions: 619 Q&A's Shared By: juno
Question 32

An organization is prioritizing efforts to remediate or mitigate risks identified during the latest assessment. For one of the risks, a full remediation was not possible, but the organization was able to successfully apply mitigations to reduce the likelihood of impact.

Which of the following should the organization perform NEXT?

Options:

A.

Assess the residual risk.

B.

Update the organization’s threat model.

C.

Move to the next risk in the register.

D.

Recalculate the magnitude of impact.

Discussion
Question 33

A development team created a mobile application that contacts a company’s back-end APIs housed in a PaaS environment. The APIs have been experiencing high processor utilization due to scraping activities. The security engineer needs to recommend a solution that will prevent and remedy the behavior.

Which of the following would BEST safeguard the APIs? (Choose two.)

Options:

A.

Bot protection

B.

OAuth 2.0

C.

Input validation

D.

Autoscaling endpoints

E.

Rate limiting

F.

CSRF protection

Discussion
Question 34

A company hosts a large amount of data in blob storage for its customers. The company recently had a number of issues with this data being prematurely deleted before the scheduled backup processes could be completed. The management team has asked the security architect for a recommendation that allows blobs to be deleted occasionally, but only after a successful backup. Which of the following solutions will BEST meet this requirement?

Options:

A.

Mirror the blobs at a local data center.

B.

Enable fast recovery on the storage account.

C.

Implement soft delete for blobs.

D.

Make the blob immutable.

Discussion
Question 35

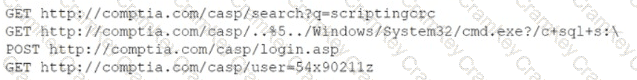
A security analyst needs to recommend a remediation to the following threat:
Questions 35

Which of the following actions should the security analyst propose to prevent this successful exploitation?

Options:

A.

Patch the system.

B.

Update the antivirus.

C.

Install a host-based firewall.

D.

Enable TLS 1.2.

Discussion
Lois
I passed my exam with wonderful score. Their dumps are 100% valid and I felt confident during the exam.
Ernie Aug 11, 2026
Absolutely. The best part is, the answers in the dumps were correct. So, I felt confident and well-prepared for the exam.
Ari
Can anyone explain what are these exam dumps and how are they?
Ocean Aug 18, 2026
They're exam preparation materials that are designed to help you prepare for various certification exams. They provide you with up-to-date and accurate information to help you pass your exams.
Kingsley
Do anyone guide my how these dumps would be helpful for new students like me?
Haris Aug 2, 2026
Absolutely! They are highly recommended for anyone looking to pass their certification exam. The dumps are easy to understand and follow, making it easier for you to study and retain the information.
Cody
I used Cramkey Dumps to prepare and a lot of the questions on the exam were exactly what I found in their study materials.
Eric Aug 3, 2026
Really? That's great to hear! I used Cramkey Dumps too and I had the same experience. The questions were almost identical.
Page: 8 / 46
Title
Questions
Posted

CAS-004
PDF

$36.75  $104.99

CAS-004 Testing Engine

$43.75  $124.99

CAS-004 PDF + Testing Engine

$57.75  $164.99

