Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

ECCouncil Updated EC0-350 Exam Questions and Answers by rome

Page: 25 / 32

ECCouncil EC0-350 Exam Overview :

Exam Name: Ethical Hacking and Countermeasures V8
Exam Code: EC0-350 Dumps
Vendor: ECCouncil Certification: Certified Ethical Hacker
Questions: 878 Q&A's Shared By: rome
Question 100

What is a sniffing performed on a switched network called?

Options:

A.

Spoofed sniffing

B.

Passive sniffing

C.

Direct sniffing

D.

Active sniffing

Discussion
Teddie
yes, I passed my exam with wonderful score, Accurate and valid dumps.
Isla-Rose Oct 28, 2026
Absolutely! The questions in the dumps were almost identical to the ones that appeared in the actual exam. I was able to answer almost all of them correctly.
Norah
Cramkey is highly recommended.
Zayan Oct 22, 2026
Definitely. If you're looking for a reliable and effective study resource, look no further than Cramkey Dumps. They're simply wonderful!
Fatima
Hey I passed my exam. The world needs to know about it. I have never seen real exam questions on any other exam preparation resource like I saw on Cramkey Dumps.
Niamh Oct 1, 2026
That's true. Cramkey Dumps are simply the best when it comes to preparing for the certification exam. They have all the key information you need and the questions are very similar to what you'll see on the actual exam.
Ernest
That's amazing. I think I'm going to give Cramkey Dumps a try for my next exam. Thanks for telling me about them! CramKey admin please share more questions……You guys are amazing.
Nate Oct 12, 2026
I failed last week, I never know this site , but amazed to see all these questions were in my exam week before. I feel bad now, why I didn’t bother this site. Thanks Cramkey, Excellent Job.
Question 101

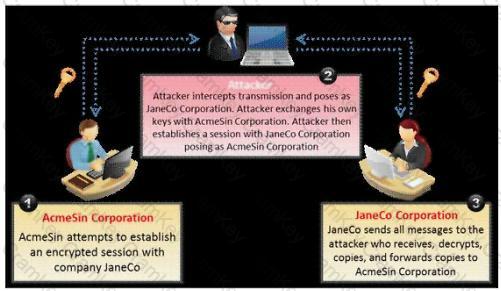
What type of attack is shown in the following diagram?

Questions 101

Options:

A.

Man-in-the-Middle (MiTM) Attack

B.

Session Hijacking Attack

C.

SSL Spoofing Attack

D.

Identity Stealing Attack

Discussion
Question 102

A common technique for luring e-mail users into opening virus-launching attachments is to send messages that would appear to be relevant or important to many of their potential recipients. One way of accomplishing this feat is to make the virus-carrying messages appear to come from some type of business entity retailing sites, UPS, FEDEX, CITIBANK or a major provider of a common service.

Here is a fraudulent e-mail claiming to be from FedEx regarding a package that could not be delivered. This mail asks the receiver to open an attachment in order to obtain the FEDEX tracking number for picking up the package. The attachment contained in this type of e-mail activates a virus.
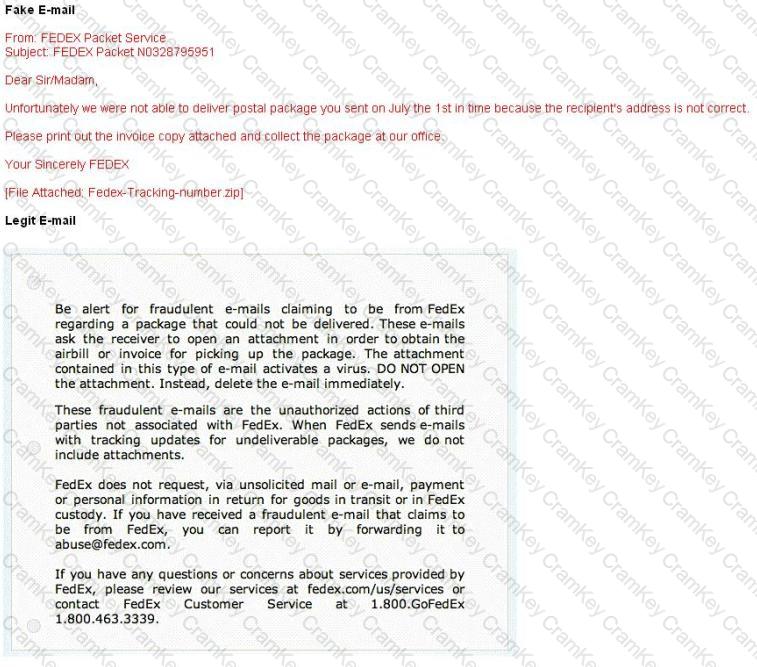
Questions 102

Vendors send e-mails like this to their customers advising them not to open any files attached with the mail, as they do not include attachments.

Fraudulent e-mail and legit e-mail that arrives in your inbox contain the fedex.com as the sender of the mail.

How do you ensure if the e-mail is authentic and sent from fedex.com?

Options:

A.

Verify the digital signature attached with the mail, the fake mail will not have Digital ID at all

B.

Check the Sender ID against the National Spam Database (NSD)

C.

Fake mail will have spelling/grammatical errors

D.

Fake mail uses extensive images, animation and flash content

Discussion
Question 103

Why would an ethical hacker use the technique of firewalking?

Options:

A.

It is a technique used to discover wireless network on foot.

B.

It is a technique used to map routers on a network link.

C.

It is a technique used to discover the nature of rules configured on a gateway.

D.

It is a technique used to discover interfaces in promiscuous mode.

Discussion
Page: 25 / 32
Title
Questions
Posted

EC0-350
PDF

$27.5  $109.99

EC0-350 Testing Engine

$32.5  $129.99

EC0-350 PDF + Testing Engine

$42.5  $169.99