Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

GAQM Updated CEH-001 Exam Questions and Answers by ronald

Page: 32 / 32

GAQM CEH-001 Exam Overview :

Exam Name: Certified Ethical Hacker (CEH)
Exam Code: CEH-001 Dumps
Vendor: GAQM Certification: Certified Ethical Hacker CEH
Questions: 878 Q&A's Shared By: ronald
Question 128

After a client sends a connection request (SYN) packet to the server, the server will respond (SYN-ACK) with a sequence number of its choosing, which then must be acknowledged (ACK) by the client. This sequence number is predictable; the attack connects to a service first with its own IP address, records the sequence number chosen, and then opens a second connection from a forged IP address. The attack doesn't see the SYN-ACK (or any other packet) from the server, but can guess the correct responses. If the source IP address is used for authentication, then the attacker can use the one-sided communication to break into the server. What attacks can you successfully launch against a server using the above technique?

Options:

A.

Denial of Service attacks

B.

Session Hijacking attacks

C.

Web page defacement attacks

D.

IP spoofing attacks

Discussion
Question 129

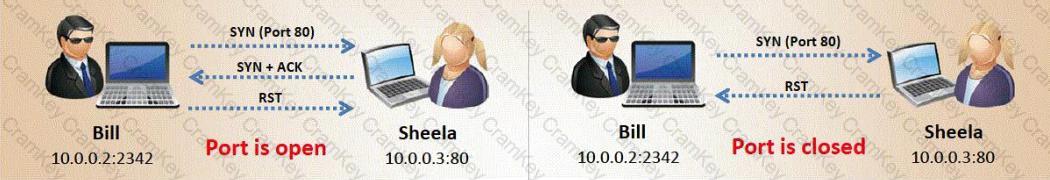
What type of port scan is represented here.
Questions 129

Options:

A.

Stealth Scan

B.

Full Scan

C.

XMAS Scan

D.

FIN Scan

Discussion
Inaya
Passed the exam. questions are valid. The customer support is top-notch. They were quick to respond to any questions I had and provided me with all the information I needed.
Cillian Sep 22, 2026
That's a big plus. I've used other dump providers in the past and the customer support was often lacking.
Josephine
I want to ask about their study material and Customer support? Can anybody guide me?
Zayd Sep 9, 2026
Yes, the dumps or study material provided by them are authentic and up to date. They have a dedicated team to assist students and make sure they have a positive experience.
Nylah
I've been looking for good study material for my upcoming certification exam. Need help.
Dolly Sep 16, 2026
Then you should definitely give Cramkey Dumps a try. They have a huge database of questions and answers, making it easy to study and prepare for the exam. And the best part is, you can be sure the information is accurate and relevant.
River
Hey, I used Cramkey Dumps to prepare for my recent exam and I passed it.
Lewis Sep 10, 2026
Yeah, I used these dumps too. And I have to say, I was really impressed with the results.
Kylo
What makes Cramkey Dumps so reliable? Please guide.
Sami Sep 10, 2026
Well, for starters, they have a team of experts who are constantly updating their material to reflect the latest changes in the industry. Plus, they have a huge database of questions and answers, which makes it easy to study and prepare for the exam.
Question 130

During a penetration test, the tester conducts an ACK scan using NMAP against the external interface of the DMZ firewall. NMAP reports that port 80 is unfiltered. Based on this response, which type of packet inspection is the firewall conducting?

Options:

A.

Host

B.

Stateful

C.

Stateless

D.

Application

Discussion
Question 131

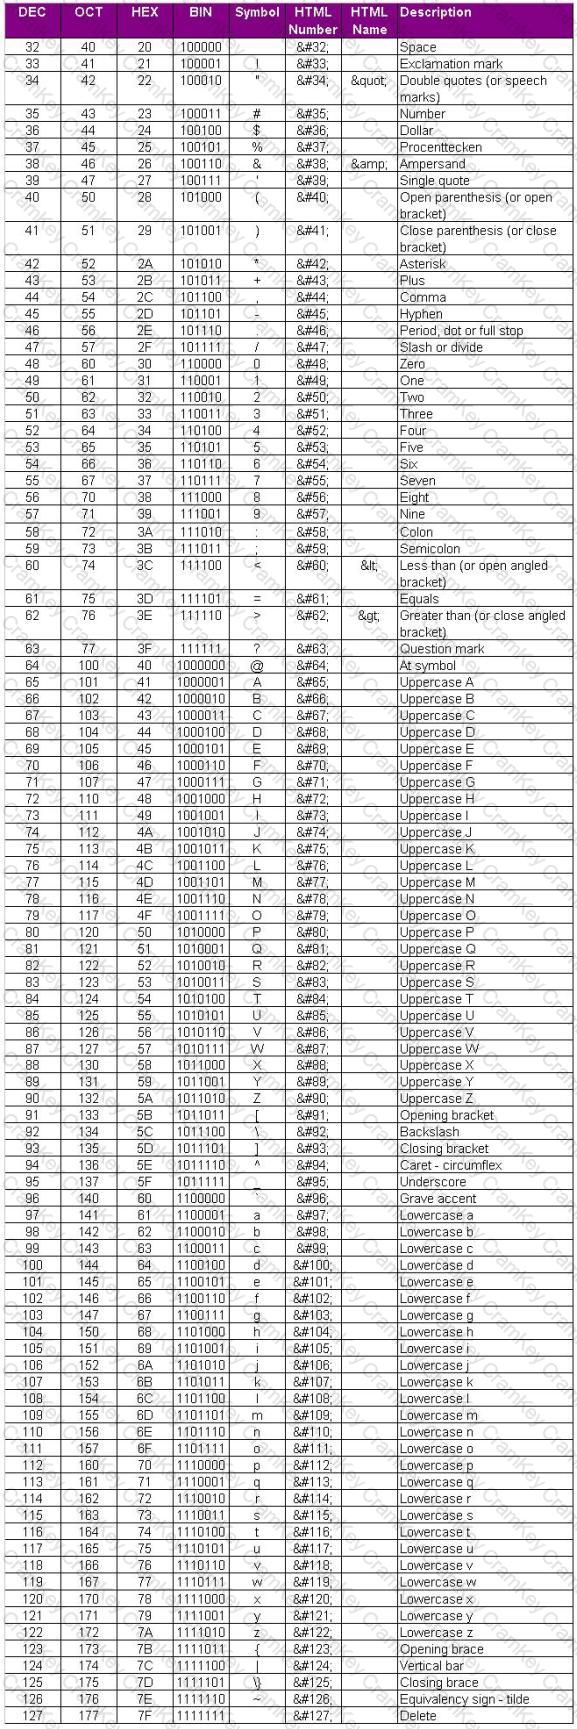
Here is the ASCII Sheet.

Questions 131

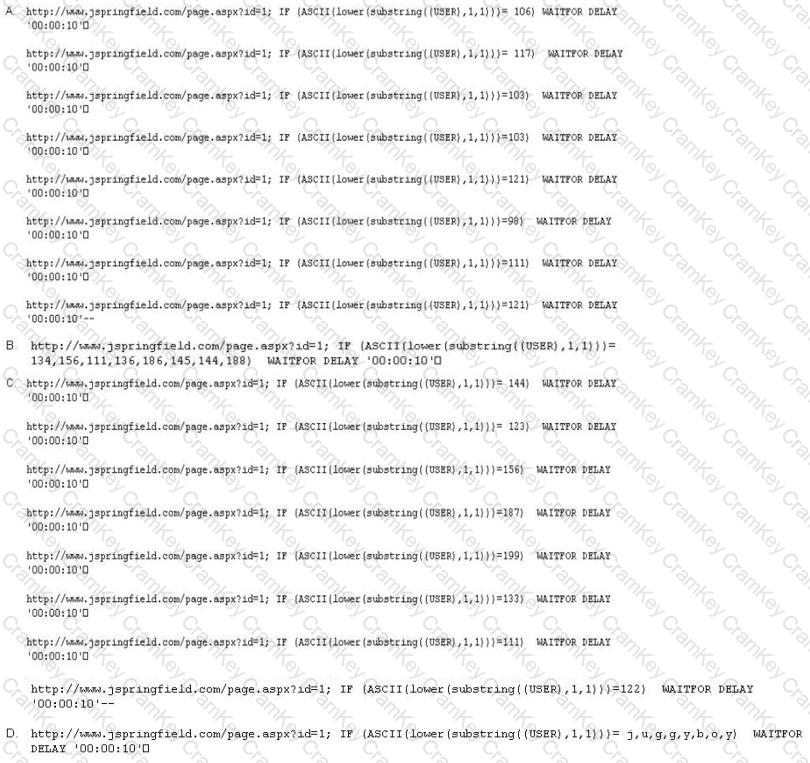
You want to guess the DBO username juggyboy (8 characters) using Blind SQL Injection technique.

What is the correct syntax?
Questions 131

Options:

A.

Option A

B.

Option B

C.

Option C

D.

Option D

Discussion
Page: 32 / 32
Title
Questions
Posted

CEH-001
PDF

$31.5  $104.99

CEH-001 Testing Engine

$37.5  $124.99

CEH-001 PDF + Testing Engine

$49.5  $164.99