Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

Page: 1 / 35

PenTest+ CompTIA PenTest+ Certification Exam

CompTIA PenTest+ Certification Exam

Last Update Sep 8, 2026
Total Questions : 464

To help you prepare for the PT0-002 CompTIA exam, we are offering free PT0-002 CompTIA exam questions. All you need to do is sign up, provide your details, and prepare with the free PT0-002 practice questions. Once you have done that, you will have access to the entire pool of CompTIA PenTest+ Certification Exam PT0-002 test questions which will help you better prepare for the exam. Additionally, you can also find a range of CompTIA PenTest+ Certification Exam resources online to help you better understand the topics covered on the exam, such as CompTIA PenTest+ Certification Exam PT0-002 video tutorials, blogs, study guides, and more. Additionally, you can also practice with realistic CompTIA PT0-002 exam simulations and get feedback on your progress. Finally, you can also share your progress with friends and family and get encouragement and support from them.

Questions 2

Which of the following types of information would MOST likely be included in an application security assessment report addressed to developers? (Choose two.)

Options:

A.  

Use of non-optimized sort functions

B.  

Poor input sanitization

C.  

Null pointer dereferences

D.  

Non-compliance with code style guide

E.  

Use of deprecated Javadoc tags

F.  

A cydomatic complexity score of 3

Discussion 0
Questions 3

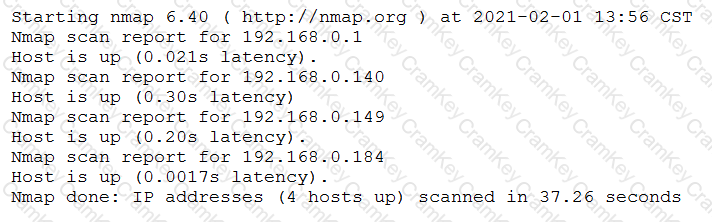
A penetration tester conducted a discovery scan that generated the following:
Questions 3

Which of the following commands generated the results above and will transform them into a list of active hosts for further analysis?

Options:

A.  

nmap –oG list.txt 192.168.0.1-254 , sort

B.  

nmap –sn 192.168.0.1-254 , grep “Nmap scan” | awk ‘{print S5}’

C.  

nmap –-open 192.168.0.1-254, uniq

D.  

nmap –o 192.168.0.1-254, cut –f 2

Discussion 0
Ella-Rose
Amazing website with excellent Dumps. I passed my exam and secured excellent marks!!!
Alisha Aug 19, 2026
Extremely accurate. They constantly update their materials with the latest exam questions and answers, so you can be confident that what you're studying is up-to-date.
Inaya
Passed the exam. questions are valid. The customer support is top-notch. They were quick to respond to any questions I had and provided me with all the information I needed.
Cillian Aug 25, 2026
That's a big plus. I've used other dump providers in the past and the customer support was often lacking.
Billy
It was like deja vu! I was confident going into the exam because I had already seen those questions before.
Vincent Aug 25, 2026
Definitely. And the best part is, I passed! I feel like all that hard work and preparation paid off. Cramkey is the best resource for all students!!!
Anya
I must say they're considered the best dumps available and the questions are very similar to what you'll see in the actual exam. Recommended!!!
Cassius Aug 10, 2026
Yes, they offer a 100% success guarantee. And many students who have used them have reported passing their exams with flying colors.
Stefan
Thank you so much Cramkey I passed my exam today due to your highly up to date dumps.
Ocean Aug 6, 2026
Agree….Cramkey Dumps are constantly updated based on changes in the exams. They also have a team of experts who regularly review the materials to ensure their accuracy and relevance. This way, you can be sure you're studying the most up-to-date information available.
Questions 4

Which of the following types of information should be included when writing the remediation section of a penetration test report to be viewed by the systems administrator and technical staff?

Options:

A.  

A quick description of the vulnerability and a high-level control to fix it

B.  

Information regarding the business impact if compromised

C.  

The executive summary and information regarding the testing company

D.  

The rules of engagement from the assessment

Discussion 0
Questions 5

A company is concerned that its cloud service provider is not adequately protecting the VMs housing its software development. The VMs are housed in a datacenter with other companies sharing physical resources. Which of the following attack types is MOST concerning to the company?

Options:

A.  

Data flooding

B.  

Session riding

C.  

Cybersquatting

D.  

Side channel

Discussion 0
Title
Questions
Posted

PT0-002
PDF

$36.75  $104.99

PT0-002 Testing Engine

$43.75  $124.99

PT0-002 PDF + Testing Engine

$57.75  $164.99

