Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

GAQM Updated CPEH-001 Exam Questions and Answers by rae

Page: 16 / 27

GAQM CPEH-001 Exam Overview :

Exam Name: Certified Professional Ethical Hacker (CPEH)
Exam Code: CPEH-001 Dumps
Vendor: GAQM Certification: Information Systems Security
Questions: 736 Q&A's Shared By: rae
Question 64

The Open Web Application Security Project (OWASP) is the worldwide not-for-profit charitable organization focused on improving the security of software. What item is the primary concern on OWASP's Top Ten Project Most Critical Web Application Security Risks?

Options:

A.

Injection

B.

Cross Site Scripting

C.

Cross Site Request Forgery

D.

Path disclosure

Discussion
Question 65

Which among the following is a Windows command that a hacker can use to list all the shares to which the current user context has access?

Options:

A.

NET FILE

B.

NET USE

C.

NET CONFIG

D.

NET VIEW

Discussion
Question 66

(Note: the student is being tested on concepts learnt during passive OS fingerprinting, basic TCP/IP connection concepts and the ability to read packet signatures from a sniff dump.). Snort has been used to capture packets on the network. On studying the packets, the penetration tester finds it to be abnormal. If you were the penetration tester, why would you find this abnormal?

What is odd about this attack? Choose the best answer.
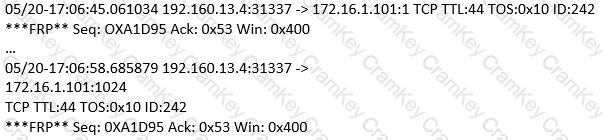
Questions 66

Options:

A.

This is not a spoofed packet as the IP stack has increasing numbers for the three flags.

B.

This is back orifice activity as the scan comes from port 31337.

C.

The attacker wants to avoid creating a sub-carries connection that is not normally valid.

D.

These packets were crafted by a tool, they were not created by a standard IP stack.

Discussion
Question 67

Which access control mechanism allows for multiple systems to use a central authentication server (CAS) that permits users to authenticate once and gain access to multiple systems?

Options:

A.

Role Based Access Control (RBAC)

B.

Discretionary Access Control (DAC)

C.

Windows authentication

D.

Single sign-on

Discussion
Miriam
Highly recommended Dumps. 100% authentic and reliable. Passed my exam with wonderful score.
Milan Oct 22, 2026
I see. Thanks for the information. I'll definitely keep Cramkey in mind for my next exam.
Inaya
Passed the exam. questions are valid. The customer support is top-notch. They were quick to respond to any questions I had and provided me with all the information I needed.
Cillian Oct 21, 2026
That's a big plus. I've used other dump providers in the past and the customer support was often lacking.
Reeva
Wow what a success I achieved today. Thank you so much Cramkey for amazing Dumps. All students must try it.
Amari Oct 27, 2026
Wow, that's impressive. I'll definitely keep Cramkey in mind for my next exam.
Aryan
Absolutely rocked! They are an excellent investment for anyone who wants to pass the exam on the first try. They save you time and effort by providing a comprehensive overview of the exam content, and they give you a competitive edge by giving you access to the latest information. So, I definitely recommend them to new students.
Jessie Oct 23, 2026
did you use PDF or Engine? Which one is most useful?
Page: 16 / 27
Title
Questions
Posted

CPEH-001
PDF

$27.5  $109.99

CPEH-001 Testing Engine

$32.5  $129.99

CPEH-001 PDF + Testing Engine

$42.5  $169.99

