Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

ECCouncil Updated 312-49v10 Exam Questions and Answers by philippa

Page: 15 / 26

ECCouncil 312-49v10 Exam Overview :

Exam Name: Computer Hacking Forensic Investigator (CHFI-v10)
Exam Code: 312-49v10 Dumps
Vendor: ECCouncil Certification: CHFI v10
Questions: 704 Q&A's Shared By: philippa
Question 60

Chloe is a forensic examiner who is currently cracking hashed passwords for a crucial mission and hopefully solve the case. She is using a lookup table used for recovering a plain text password from cipher text; it contains word list and brute-force list along with their computed hash values. Chloe Is also using a graphical generator that supports SHA1.

a. What password technique is being used?

b. What tool is Chloe using?

Options:

A.

Dictionary attack b. Cisco PIX

B.

Cain & Able b. Rten

C.

Brute-force b. MScache

D.

Rainbow Tables b. Winrtgen

Discussion
Question 61

Which of the following applications will allow a forensic investigator to track the user login sessions and user transactions that have occurred on an MS SQL Server?

Options:

A.

ApexSQL Audit

B.

netcat

C.

Notepad++

D.

Event Log Explorer

Discussion
Kingsley
Do anyone guide my how these dumps would be helpful for new students like me?
Haris Sep 22, 2026
Absolutely! They are highly recommended for anyone looking to pass their certification exam. The dumps are easy to understand and follow, making it easier for you to study and retain the information.
Andrew
Are these dumps helpful?
Jeremiah Sep 19, 2026
Yes, Don’t worry!!! I'm confident you'll find them to be just as helpful as I did. Good luck with your exam!
Alaya
Best Dumps among other dumps providers. I like it so much because of their authenticity.
Kaiden Sep 17, 2026
That's great. I've used other dump providers in the past and they were often outdated or had incorrect information. This time I will try it.
Ernest
That's amazing. I think I'm going to give Cramkey Dumps a try for my next exam. Thanks for telling me about them! CramKey admin please share more questions……You guys are amazing.
Nate Sep 5, 2026
I failed last week, I never know this site , but amazed to see all these questions were in my exam week before. I feel bad now, why I didn’t bother this site. Thanks Cramkey, Excellent Job.
Rosalie
I passed. I would like to tell all students that they should definitely give Cramkey Dumps a try.
Maja Sep 6, 2026
That sounds great. I'll definitely check them out. Thanks for the suggestion!
Question 62

You are the incident response manager at a regional bank. While performing routine auditing of web application logs, you find several attempted login submissions that contain the following strings:
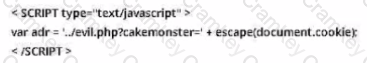
Questions 62

What kind of attack has occurred?

Options:

A.

SQL injection

B.

Buffer overflow

C.

Cross-size scripting

D.

Cross-size request forgery

Discussion
Question 63

What happens lo the header of the file once It Is deleted from the Windows OS file systems?

Options:

A.

The OS replaces the first letter of a deleted file name with a hex byte code: E5h

B.

The OS replaces the entire hex byte coding of the file.

C.

The hex byte coding of the file remains the same, but the file location differs

D.

The OS replaces the second letter of a deleted file name with a hex byte code: Eh5

Discussion
Page: 15 / 26
Title
Questions
Posted

312-49v10
PDF

$31.5  $104.99

312-49v10 Testing Engine

$37.5  $124.99

312-49v10 PDF + Testing Engine

$49.5  $164.99

