Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

ECCouncil Updated 312-49v10 Exam Questions and Answers by herbie

Page: 22 / 26

ECCouncil 312-49v10 Exam Overview :

Exam Name: Computer Hacking Forensic Investigator (CHFI-v10)
Exam Code: 312-49v10 Dumps
Vendor: ECCouncil Certification: CHFI v10
Questions: 704 Q&A's Shared By: herbie
Question 88

Which program uses different techniques to conceal a malware's code, thereby making it difficult for security mechanisms to detect or remove it?

Options:

A.

Dropper

B.

Packer

C.

Injector

D.

Obfuscator

Discussion
Question 89

What is the investigator trying to analyze if the system gives the following image as output?
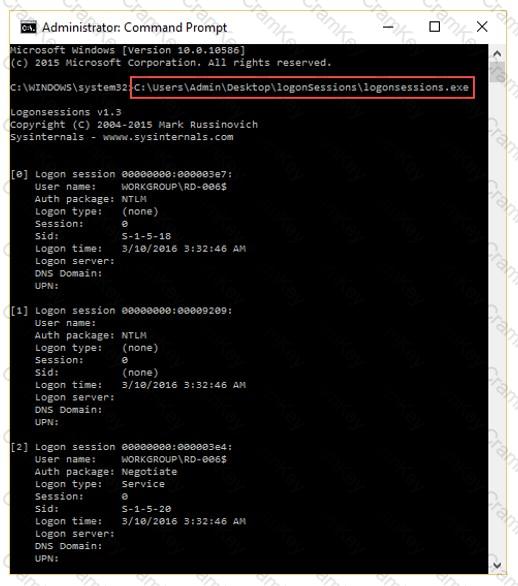
Questions 89

Options:

A.

All the logon sessions

B.

Currently active logon sessions

C.

Inactive logon sessions

D.

Details of users who can logon

Discussion
Hassan
Highly Recommended Dumps… today I passed my exam! Same questions appear. I bought Full Access.
Kasper Sep 6, 2026
Hey wonderful….so same questions , sounds good. Planning to write this week, I will go for full access today.
Josie
I just passed my certification exam using their dumps and I must say, I was thoroughly impressed.
Fatimah Sep 9, 2026
You’re right. The dumps were authentic and covered all the important topics. I felt confident going into the exam and it paid off.
Miriam
Highly recommended Dumps. 100% authentic and reliable. Passed my exam with wonderful score.
Milan Sep 19, 2026
I see. Thanks for the information. I'll definitely keep Cramkey in mind for my next exam.
Alessia
Amazing Dumps. Found almost all questions in actual exam whih I prepared from these valuable dumps. Recommended!!!!
Belle Sep 22, 2026
That's impressive. I've been struggling with finding good study material for my certification. Maybe I should give Cramkey Dumps a try.
Nia
Why are these Dumps so important for students these days?
Mary Sep 27, 2026
With the constantly changing technology and advancements in the industry, it's important for students to have access to accurate and valid study material. Cramkey Dumps provide just that. They are constantly updated to reflect the latest changes and ensure that the information is up-to-date.
Question 90

Which layer of iOS architecture should a forensics investigator evaluate to analyze services such as Threading, File Access, Preferences, Networking and high-level features?

Options:

A.

Core Services

B.

Media services

C.

Cocoa Touch

D.

Core OS

Discussion
Question 91

Consider that you are investigating a machine running an Windows OS released prior to Windows Vista. You are trying to gather information about the deleted files by examining the master database file named INFO2 located at C:\Recycler\\. You read an entry named "Dd5.exe". What does Dd5.exe mean?

Options:

A.

D drive. fifth file deleted, a .exe file

B.

D drive, fourth file restored, a .exe file

C.

D drive, fourth file deleted, a .exe file

D.

D drive, sixth file deleted, a .exe file

Discussion
Page: 22 / 26
Title
Questions
Posted

312-49v10
PDF

$36.75  $104.99

312-49v10 Testing Engine

$43.75  $124.99

312-49v10 PDF + Testing Engine

$57.75  $164.99


