Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

CompTIA Updated CS0-003 Exam Questions and Answers by aliza

Page: 25 / 36

CompTIA CS0-003 Exam Overview :

Exam Name: CompTIA CyberSecurity Analyst CySA+ Certification Exam
Exam Code: CS0-003 Dumps
Vendor: CompTIA Certification: CompTIA CySA+
Questions: 515 Q&A's Shared By: aliza
Question 100

The vulnerability analyst reviews threat intelligence regarding emerging vulnerabilities affecting workstations that are used within the company:
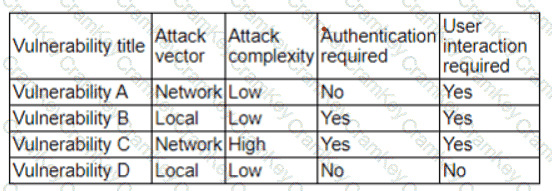
Questions 100

Which of the following vulnerabilities should the analyst be most concerned about, knowing that end users frequently click on malicious links sent via email?

Options:

A.

Vulnerability A

B.

Vulnerability B

C.

Vulnerability C

D.

Vulnerability D

Discussion
Fatima
Hey I passed my exam. The world needs to know about it. I have never seen real exam questions on any other exam preparation resource like I saw on Cramkey Dumps.
Niamh Sep 16, 2026
That's true. Cramkey Dumps are simply the best when it comes to preparing for the certification exam. They have all the key information you need and the questions are very similar to what you'll see on the actual exam.
Andrew
Are these dumps helpful?
Jeremiah Sep 19, 2026
Yes, Don’t worry!!! I'm confident you'll find them to be just as helpful as I did. Good luck with your exam!
Yusra
I passed my exam. Cramkey Dumps provides detailed explanations for each question and answer, so you can understand the concepts better.
Alisha Sep 11, 2026
I recently used their dumps for the certification exam I took and I have to say, I was really impressed.
Inaaya
Are these Dumps worth buying?
Fraser Sep 20, 2026
Yes, of course, they are necessary to pass the exam. They give you an insight into the types of questions that could come up and help you prepare effectively.
Question 101

During an incident, a security analyst discovers a large amount of Pll has been emailed externally from an employee to a public email address. The analyst finds that the external email is the employee ' s

personal email. Which of the following should the analyst recommend be done first?

Options:

A.

Place a legal hold on the employee ' s mailbox.

B.

Enable filtering on the web proxy.

C.

Disable the public email access with CASB.

D.

Configure a deny rule on the firewall.

Discussion
Question 102

Which of the following best describes the threat concept in which an organization works to ensure that all network users only open attachments from known sources?

Options:

A.

Hacktivist threat

B.

Advanced persistent threat

C.

Unintentional insider threat

D.

Nation-state threat

Discussion
Question 103

A web application team notifies a SOC analyst that there are thousands of HTTP/404 events on the public-facing web server. Which of the following is the next step for the analyst to take?

Options:

A.

Instruct the firewall engineer that a rule needs to be added to block this external server.

B.

Escalate the event to an incident and notify the SOC manager of the activity.

C.

Notify the incident response team that a DDoS attack is occurring.

D.

Identify the IP/hostname for the requests and look at the related activity.

Discussion
Page: 25 / 36
Title
Questions
Posted

CS0-003
PDF

$31.5  $104.99

CS0-003 Testing Engine

$37.5  $124.99

CS0-003 PDF + Testing Engine

$49.5  $164.99

