Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

CompTIA Updated CS0-003 Exam Questions and Answers by alannah

Page: 12 / 36

CompTIA CS0-003 Exam Overview :

Exam Name: CompTIA CyberSecurity Analyst CySA+ Certification Exam
Exam Code: CS0-003 Dumps
Vendor: CompTIA Certification: CompTIA CySA+
Questions: 515 Q&A's Shared By: alannah
Question 48

A security analyst found the following vulnerability on the company’s website:

< INPUT TYPE=“IMAGE” SRC=“javascript:alert(‘test’);” >

Which of the following should be implemented to prevent this type of attack in the future?

Options:

A.

Input sanitization

B.

Output encoding

C.

Code obfuscation

D.

Prepared statements

Discussion
Question 49

Which of the following is most appropriate to use with SOAR when the security team would like to automate actions across different vendor platforms?

Options:

A.

STIX/TAXII

B.

APIs

C.

Data enrichment

D.

Threat feed

Discussion
Amy
I passed my exam and found your dumps 100% relevant to the actual exam.
Lacey Sep 5, 2026
Yeah, definitely. I experienced the same.
Esmae
I highly recommend Cramkey Dumps to anyone preparing for the certification exam.
Mollie Sep 15, 2026
Absolutely. They really make it easier to study and retain all the important information. I'm so glad I found Cramkey Dumps.
Elise
I've heard that Cramkey is one of the best websites for exam dumps. They have a high passing rate and the questions are always up-to-date. Is it true?
Cian Sep 26, 2026
Definitely. The dumps are constantly updated to reflect the latest changes in the certification exams. And I also appreciate how they provide explanations for the answers, so I could understand the reasoning behind each question.
Vienna
I highly recommend them. They are offering exact questions that we need to prepare our exam.
Jensen Sep 6, 2026
That's great. I think I'll give Cramkey a try next time I take a certification exam. Thanks for the recommendation!
Question 50

The threat intelligence team is using the MITRE ATT & CK framework to map threat actors’ TTPs to the team’s internal reference library. Which of the following best describes the reason visualization and stage alignment are helpful for the incident response team?

Options:

A.

Having a common framework provides structure for relaying the known indicators of concern to the security monitoring team.

B.

Knowing the attack stage helps the incident response team determine how to structure custom SIEM alerts to detect security events of interest.

C.

A visual mapping helps the incident response team identify the stage and relevant TTPs faster than a white paper for each threat actor.

D.

Aligning an action to a specific stage in an incident allows the incident response team to better define intent and anticipate the next action.

Discussion
Question 51

Patches for two highly exploited vulnerabilities were released on the same Friday afternoon. Information about the systems and vulnerabilities is shown in the tables below:
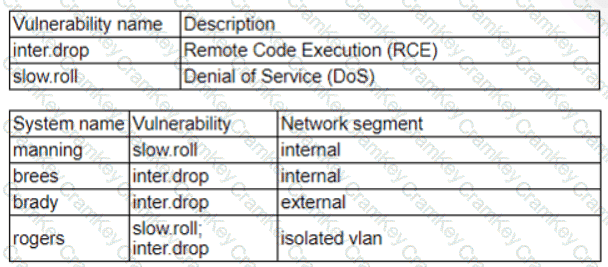
Questions 51

Which of the following should the security analyst prioritize for remediation?

Options:

A.

rogers

B.

brady

C.

brees

D.

manning

Discussion
Page: 12 / 36
Title
Questions
Posted

CS0-003
PDF

$31.5  $104.99

CS0-003 Testing Engine

$37.5  $124.99

CS0-003 PDF + Testing Engine

$49.5  $164.99

