Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

CompTIA Updated CS0-003 Exam Questions and Answers by niall

Page: 5 / 36

CompTIA CS0-003 Exam Overview :

Exam Name: CompTIA CyberSecurity Analyst CySA+ Certification Exam
Exam Code: CS0-003 Dumps
Vendor: CompTIA Certification: CompTIA CySA+
Questions: 515 Q&A's Shared By: niall
Question 20

An incident response analyst notices multiple emails traversing the network that target only the administrators of the company. The email contains a concealed URL that leads to an unknown website in another country. Which of the following best describes what is happening? (Choose two.)

Options:

A.

Beaconinq

B.

Domain Name System hijacking

C.

Social engineering attack

D.

On-path attack

E.

Obfuscated links

F.

Address Resolution Protocol poisoning

Discussion
Pippa
I was so happy to see that almost all the questions on the exam were exactly what I found in their Dumps.
Anastasia Sep 23, 2026
You are right…It was amazing! The Cramkey Dumps were so comprehensive and well-organized, it made studying for the exam a breeze.
Conor
I recently used these dumps for my exam and I must say, I was impressed with their authentic material.
Yunus Sep 22, 2026
Exactly…….The information in the dumps is so authentic and up-to-date. Plus, the questions are very similar to what you'll see on the actual exam. I felt confident going into the exam because I had studied using Cramkey Dumps.
Sam
Can I get help from these dumps and their support team for preparing my exam?
Audrey Sep 25, 2026
Definitely, you won't regret it. They've helped so many people pass their exams and I'm sure they'll help you too. Good luck with your studies!
Nell
Are these dumps reliable?
Ernie Sep 23, 2026
Yes, very much so. Cramkey Dumps are created by experienced and certified professionals who have gone through the exams themselves. They understand the importance of providing accurate and relevant information to help you succeed.
Question 21

A laptop that is company owned and managed is suspected to have malware. The company implemented centralized security logging. Which of the following log sources will confirm the malware infection?

Options:

A.

XDR logs

B.

Firewall logs

C.

IDS logs

D.

MFA logs

Discussion
Question 22

A security analyst is trying to validate the results of a web application scan with Burp Suite. The security analyst performs the following:
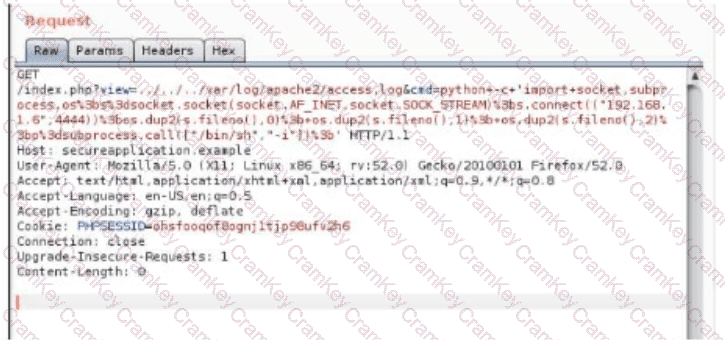
Questions 22

Which of the following vulnerabilitles Is the securlty analyst trylng to valldate?

Options:

A.

SQL injection

B.

LFI

C.

XSS

D.

CSRF

Discussion
Question 23

A regulated organization experienced a security breach that exposed a list of customer names with corresponding PH data. Which of the following is the best reason for developing the organization ' s communication plans?

Options:

A.

For the organization ' s public relations department to have a standard notification

B.

To ensure incidents are immediately reported to a regulatory agency

C.

To automate the notification to customers who were impacted by the breach

D.

To have approval from executive leadership on when communication should occur

Discussion
Page: 5 / 36
Title
Questions
Posted

CS0-003
PDF

$31.5  $104.99

CS0-003 Testing Engine

$37.5  $124.99

CS0-003 PDF + Testing Engine

$49.5  $164.99

