Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

PECB Updated ISO-IEC-27001-Lead-Auditor Exam Questions and Answers by abbas

Page: 27 / 31

PECB ISO-IEC-27001-Lead-Auditor Exam Overview :

Exam Name: PECB Certified ISO/IEC 27001 2022 Lead Auditor exam
Exam Code: ISO-IEC-27001-Lead-Auditor Dumps
Vendor: PECB Certification: ISO 27001
Questions: 418 Q&A's Shared By: abbas
Question 108

You are performing an ISMS initial certification audit at a residential nursing home that provides healthcare services. The next step in your audit plan is to conduct the closing meeting. During the final audit team meeting, as an audit team leader, you agree to report 2 minor nonconformities and 1 opportunity for improvement as below:
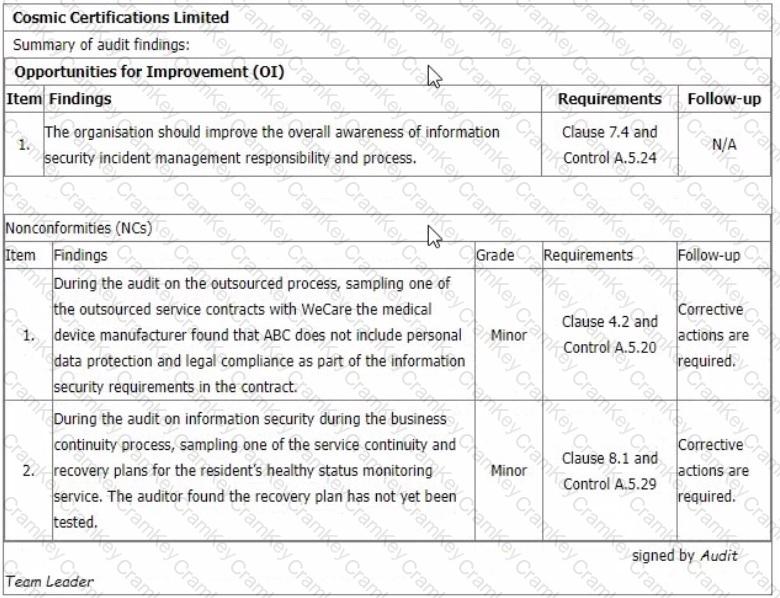
Questions 108

Select one option of the recommendation to the audit programme manager you are going to advise to the auditee at the closing meeting.

Options:

A.

Recommend certification immediately

B.

Recommend that a full scope re-audit is required within 6 months

C.

Recommend that an unannounced audit is carried out at a future date

D.

Recommend certification after your approval of the proposed corrective action plan Recommend that the findings can be closed out at a surveillance audit in 1 year

E.

Recommend that a partial audit is required within 3 months

Discussion
Question 109

Which is an example of a qualitative evidence?

Options:

A.

The documented results of an intrusion-detection test from an information security expert from an external organization

B.

A defined sample analysis of nonconformity reports drafted by the audited organization from the time their ISMS was implemented

C.

An interview with the information security personnel to validate if the information security process complies with the standard requirements

Discussion
Question 110

Scenario 7: Lawsy is a leading law firm with offices in New Jersey and New York City. It has over 50 attorneys offering sophisticated legal services to clients in business and commercial law, intellectual property, banking, and financial services. They believe they have a comfortable position in the market thanks to their commitment to implement information security best practices and remain up to date with technological developments.

Lawsy has implemented, evaluated, and conducted internal audits for an ISMS rigorously for two years now. Now, they have applied for ISO/IEC 27001 certification to ISMA, a well-known and trusted certification body.

During stage 1 audit, the audit team reviewed all the ISMS documents created during the implementation. They also reviewed and evaluated the records from management reviews and internal audits.

Lawsy submitted records of evidence that corrective actions on nonconformities were performed when necessary, so the audit team interviewed the internal auditor. The interview validated the adequacy and frequency of the internal audits by providing detailed insight into the internal audit plan and procedures.

The audit team continued with the verification of strategic documents, including the information security policy and risk evaluation criteria. During the information security policy review, the team noticed inconsistencies between the documented information describing governance framework (i.e., the information security policy) and the procedures.

Although the employees were allowed to take the laptops outside the workplace, Lawsy did not have procedures in place regarding the use of laptops in such cases. The policy only provided general information about the use of laptops. The company relied on employees' common knowledge to protect the confidentiality and integrity of information stored in the laptops. This issue was documented in the stage 1 audit report.

Upon completing stage 1 audit, the audit team leader prepared the audit plan, which addressed the audit objectives, scope, criteria, and procedures.

During stage 2 audit, the audit team interviewed the information security manager, who drafted the information security policy. He justified the Issue identified in stage 1 by stating that Lawsy conducts mandatory information security training and awareness sessions every three months.

Following the interview, the audit team examined 15 employee training records (out of 50) and concluded that Lawsy meets requirements of ISO/IEC 27001 related to training and awareness. To support this conclusion, they photocopied the examined employee training records.

Based on the scenario above, answer the following question:

The audit team photocopied the examined employee training records to support their conclusion. Should the audit team obtain an approval from Lawsy before taking this action? Refer to scenario 7.

Options:

A.

Yes. the audit team should obtain the approval of the auditee when verifying the existence of a process in all cases, including when taking notes and photocopying documents

B.

Yes, the audit team can photocopy documents observed during the audit if the auditee agrees to it

C.

No, the audit team has the authority to photocopy documents in order to verify the conformity of a certain document to the audit criteria

Discussion
Joey
I highly recommend Cramkey Dumps to anyone preparing for the certification exam. They have all the key information you need and the questions are very similar to what you'll see on the actual exam.
Dexter Sep 18, 2026
Agreed. It's definitely worth checking out if you're looking for a comprehensive and reliable study resource.
Nell
Are these dumps reliable?
Ernie Sep 23, 2026
Yes, very much so. Cramkey Dumps are created by experienced and certified professionals who have gone through the exams themselves. They understand the importance of providing accurate and relevant information to help you succeed.
Neve
Will I be able to achieve success after using these dumps?
Rohan Sep 25, 2026
Absolutely. It's a great way to increase your chances of success.
Stefan
Thank you so much Cramkey I passed my exam today due to your highly up to date dumps.
Ocean Sep 8, 2026
Agree….Cramkey Dumps are constantly updated based on changes in the exams. They also have a team of experts who regularly review the materials to ensure their accuracy and relevance. This way, you can be sure you're studying the most up-to-date information available.
Kingsley
Do anyone guide my how these dumps would be helpful for new students like me?
Haris Sep 22, 2026
Absolutely! They are highly recommended for anyone looking to pass their certification exam. The dumps are easy to understand and follow, making it easier for you to study and retain the information.
Question 111

When preparing for an audit, which of the following statements is false?

Options:

A.

Each auditor creates their own audit checklist for use during the audit

B.

The audit checklists are shared and agreed with the auditee in advance of the audit

C.

The audit plan is shared with the auditee in advance of the audit

D.

The audit plan may be changed during the audit

Discussion
Page: 27 / 31
Title
Questions
Posted

ISO-IEC-27001-Lead-Auditor
PDF

$31.5  $104.99

ISO-IEC-27001-Lead-Auditor Testing Engine

$37.5  $124.99

ISO-IEC-27001-Lead-Auditor PDF + Testing Engine

$49.5  $164.99

