Month End Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: mystc75

ECCouncil Updated 312-49v9 Exam Questions and Answers by kylian

Page: 14 / 21

ECCouncil 312-49v9 Exam Overview :

Exam Name: Computer Hacking Forensic Investigator (v9)
Exam Code: 312-49v9 Dumps
Vendor: ECCouncil Certification: CHFIv9
Questions: 589 Q&A's Shared By: kylian
Question 56

A picture file is recovered from a computer under investigation. During the investigation process, the file is enlarged 500% to get a better view of its contents. The picture quality is not degraded at all from this process. What kind of picture is this file. What kind of picture is this file?

Options:

A.

Raster image

B.

Vector image

C.

Metafile image

D.

Catalog image

Discussion
Walter
Yayyy!!! I passed my exam with the help of Cramkey Dumps. Highly appreciated!!!!
Angus Aug 5, 2026
YES….. I saw the same questions in the exam.
Billy
It was like deja vu! I was confident going into the exam because I had already seen those questions before.
Vincent Aug 25, 2026
Definitely. And the best part is, I passed! I feel like all that hard work and preparation paid off. Cramkey is the best resource for all students!!!
Kingsley
Do anyone guide my how these dumps would be helpful for new students like me?
Haris Aug 2, 2026
Absolutely! They are highly recommended for anyone looking to pass their certification exam. The dumps are easy to understand and follow, making it easier for you to study and retain the information.
Joey
I highly recommend Cramkey Dumps to anyone preparing for the certification exam. They have all the key information you need and the questions are very similar to what you'll see on the actual exam.
Dexter Aug 25, 2026
Agreed. It's definitely worth checking out if you're looking for a comprehensive and reliable study resource.
Question 57

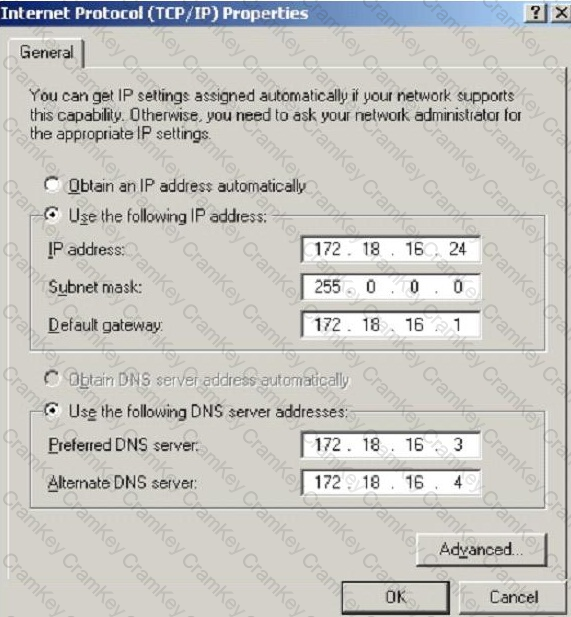
What is the CIDR from the following screenshot?

Questions 57

Options:

A.

/24A./24A./24

B.

/32 B./32 B./32

C.

/16 C./16 C./16

D.

/8D./8D./8

Discussion
Question 58

Pagefile.sys is a virtual memory file used to expand the physical memory of a computer. Select the registry path for the page file:

Options:

A.

HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Session Manager\Memory Management

B.

HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Session Manager\System Management

C.

HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Session Manager\Device Management

D.

HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Session Manager\Memory Management\PrefetchParameters

Discussion
Question 59

Why would you need to find out the gateway of a device when investigating a wireless attack?

Options:

A.

The gateway will be the IP of the proxy server used by the attacker to launch the attack

B.

The gateway will be the IP of the attacker computer

C.

The gateway will be the IP used to manage the RADIUS server

D.

The gateway will be the IP used to manage the access point

Discussion
Page: 14 / 21
Title
Questions
Posted

312-49v9
PDF

$26.25  $104.99

312-49v9 Testing Engine

$31.25  $124.99

312-49v9 PDF + Testing Engine

$41.25  $164.99