Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

ECCouncil Updated 312-50 Exam Questions and Answers by yasir

Page: 10 / 20

ECCouncil 312-50 Exam Overview :

Exam Name: Certified Ethical Hacker Exam
Exam Code: 312-50 Dumps
Vendor: ECCouncil Certification: Certified Ethical Hacker
Questions: 614 Q&A's Shared By: yasir
Question 40

Which of the following conditions must be given to allow a tester to exploit a Cross-Site Request Forgery (CSRF) vulnerable web application?

Options:

A.

The victim user must open the malicious link with an Internet Explorer prior to version 8.

B.

The session cookies generated by the application do not have the HttpOnly flag set.

C.

The victim user must open the malicious link with a Firefox prior to version 3.

D.

The web application should not use random tokens.

Discussion
River
Hey, I used Cramkey Dumps to prepare for my recent exam and I passed it.
Lewis Aug 1, 2026
Yeah, I used these dumps too. And I have to say, I was really impressed with the results.
Kylo
What makes Cramkey Dumps so reliable? Please guide.
Sami Aug 6, 2026
Well, for starters, they have a team of experts who are constantly updating their material to reflect the latest changes in the industry. Plus, they have a huge database of questions and answers, which makes it easy to study and prepare for the exam.
Andrew
Are these dumps helpful?
Jeremiah Aug 8, 2026
Yes, Don’t worry!!! I'm confident you'll find them to be just as helpful as I did. Good luck with your exam!
Yusra
I passed my exam. Cramkey Dumps provides detailed explanations for each question and answer, so you can understand the concepts better.
Alisha Aug 8, 2026
I recently used their dumps for the certification exam I took and I have to say, I was really impressed.
Zayaan
Successfully aced the exam… Thanks a lot for providing amazing Exam Dumps.
Harmony Aug 5, 2026
That's fantastic! I'm glad to hear that their dumps helped you. I also used them and found it accurate.
Question 41

A company firewall engineer has configured a new DMZ to allow public systems to be located away from the internal network. The engineer has three security zones set:
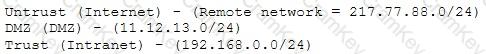
Questions 41

The engineer wants to configure remote desktop access from a fixed IP on the remote network to a remote desktop server in the DMZ. Which rule would best fit this requirement?

Options:

A.

Permit 217.77.88.0/24 11.12.13.0/24 RDP 3389

B.

Permit 217.77.88.12 11.12.13.50 RDP 3389

C.

Permit 217.77.88.12 11.12.13.0/24 RDP 3389

D.

Permit 217.77.88.0/24 11.12.13.50 RDP 3389

Discussion
Question 42

Which of the following is a strong post designed to stop a car?

Options:

A.

Gate

B.

Fence

C.

Bollard

D.

Reinforced rebar

Discussion
Question 43

An attacker uses a communication channel within an operating system that is neither designed nor intended to transfer information. What is the name of the communications channel?

Options:

A.

Classified

B.

Overt

C.

Encrypted

D.

Covert

Discussion
Page: 10 / 20
Title
Questions
Posted

312-50
PDF

$31.5  $104.99

312-50 Testing Engine

$37.5  $124.99

312-50 PDF + Testing Engine

$49.5  $164.99

