Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

Cisco Updated 200-201 Exam Questions and Answers by milly

Page: 31 / 35

Cisco 200-201 Exam Overview :

Exam Name: Understanding Cisco Cybersecurity Operations Fundamentals
Exam Code: 200-201 Dumps
Vendor: Cisco Certification: CCNA Cybersecurity
Questions: 476 Q&A's Shared By: milly
Question 124

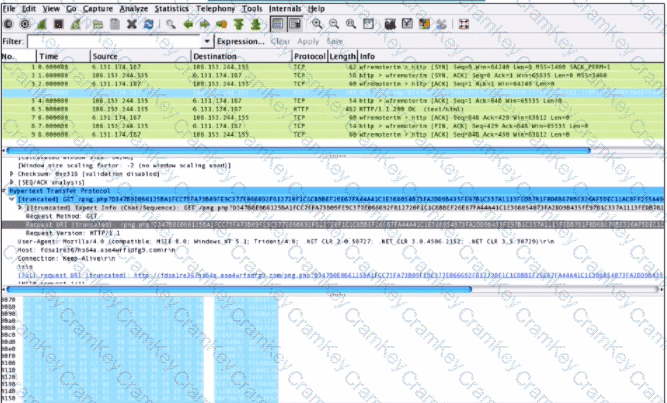
Refer to the exhibit.

Questions 124

What is shown in this PCAP file?

Options:

A.

Timestamps are indicated with error.

B.

The protocol is TCP.

C.

The User-Agent is Mozilla/5.0.

D.

The HTTP GET is encoded.

Discussion
Question 125

A network engineer noticed in the NetFlow report that internal hosts are sending many DNS requests to external DNS servers A SOC analyst checked the endpoints and discovered that they are infected and became part of the botnet Endpoints are sending multiple DNS requests but with spoofed IP addresses of valid external sources What kind of attack are infected endpoints involved in1?
Options:

A.

DNS hijacking

B.

DNS tunneling

C.

DNS flooding

D.

DNS amplification

Discussion
Ace
No problem! I highly recommend Cramkey Dumps to anyone looking to pass their certification exams. They will help you feel confident and prepared on exam day. Good luck!
Harris Oct 18, 2026
That sounds amazing. I'll definitely check them out. Thanks for the recommendation!
Cecilia
Yes, I passed my certification exam using Cramkey Dumps.
Helena Oct 6, 2026
Great. Yes they are really effective
Mylo
Excellent dumps with authentic information… I passed my exam with brilliant score.
Dominik Oct 12, 2026
That's amazing! I've been looking for good study material that will help me prepare for my upcoming certification exam. Now, I will try it.
Mariam
Do anyone think Cramkey questions can help improve exam scores?
Katie Oct 8, 2026
Absolutely! Many people have reported improved scores after using Cramkey Dumps, and there are also success stories of people passing exams on the first try. I already passed this exam. I confirmed above questions were in exam.
Question 126

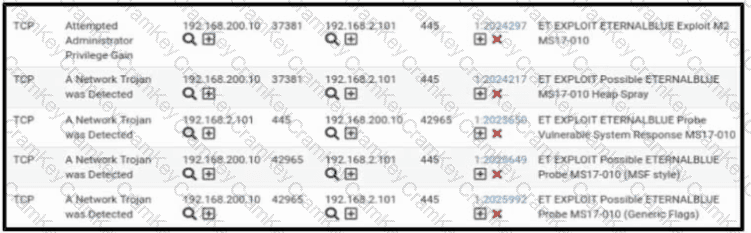
Questions 126

Refer to the exhibit. A security engineer receives several alerts from the SNORT IPS/IDS reporting malicious traffic. What should the engineer understand by examining the SNORT logs?

Options:

A.

A remote threat performs an EternalBlue attack on a Windows system on several ports.

B.

An inside threat performs an EternalBlue attack on hosts 192.168.2.101 and 192.168.200.10 on port 445.

C.

A remote threat performs an EternalBlue attack on several hosts and different ports.

D.

An inside threat performs an EternalBlue attack on a Windows system on port 445.

Discussion
Question 127

A security engineer has a video of a suspect entering a data center that was captured on the same day that files in the same data center were transferred to a competitor.

Which type of evidence is this?

Options:

A.

best evidence

B.

prima facie evidence

C.

indirect evidence

D.

physical evidence

Discussion
Page: 31 / 35
Title
Questions
Posted

200-201
PDF

$30  $119.99

200-201 Testing Engine

$35  $139.99

200-201 PDF + Testing Engine

$45  $179.99