Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

Cisco Updated 200-201 Exam Questions and Answers by wilf

Page: 12 / 35

Cisco 200-201 Exam Overview :

Exam Name: Understanding Cisco Cybersecurity Operations Fundamentals
Exam Code: 200-201 Dumps
Vendor: Cisco Certification: CCNA Cybersecurity
Questions: 476 Q&A's Shared By: wilf
Question 48

What is the purpose of command and control for network-aware malware?

Options:

A.

It contacts a remote server for commands and updates

B.

It takes over the user account for analysis

C.

It controls and shuts down services on the infected host.

D.

It helps the malware to profile the host

Discussion
Question 49

Which information must an organization use to understand the threats currently targeting the organization?

Options:

A.

threat intelligence

B.

risk scores

C.

vendor suggestions

D.

vulnerability exposure

Discussion
Victoria
Hey, guess what? I passed the certification exam! I couldn't have done it without Cramkey Dumps.
Isabel Aug 17, 2026
Same here! I was so surprised when I saw that almost all the questions on the exam were exactly what I found in their study materials.
Lennie
I passed my exam and achieved wonderful score, I highly recommend it.
Emelia Aug 13, 2026
I think I'll give Cramkey a try next time I take a certification exam. Thanks for the recommendation!
Annabel
I recently used them for my exam and I passed it with excellent score. I am impressed.
Amirah Aug 13, 2026
I passed too. The questions I saw in the actual exam were exactly the same as the ones in the Cramkey Dumps. I was able to answer the questions confidently because I had already seen and studied them.
Zayaan
Successfully aced the exam… Thanks a lot for providing amazing Exam Dumps.
Harmony Aug 5, 2026
That's fantastic! I'm glad to hear that their dumps helped you. I also used them and found it accurate.
Question 50

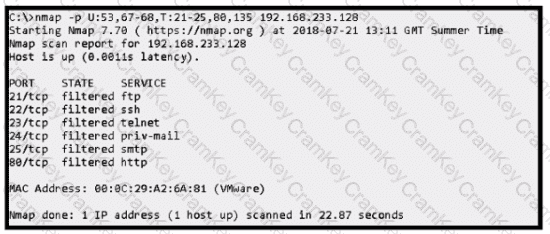
Refer to the exhibit.

Questions 50

An attacker scanned the server using Nmap.

What did the attacker obtain from this scan?

Options:

A.

Identified a firewall device preventing the port state from being returned

B.

Identified open SMB ports on the server

C.

Gathered information on processes running on the server

D.

Gathered a list of Active Directory users.

Discussion
Question 51

How does an attacker observe network traffic exchanged between two users?

Options:

A.

port scanning

B.

man-in-the-middle

C.

command injection

D.

denial of service

Discussion
Page: 12 / 35
Title
Questions
Posted

200-201
PDF

$40.25  $114.99

200-201 Testing Engine

$47.25  $134.99

200-201 PDF + Testing Engine

$61.25  $174.99