Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

Cisco Updated 200-201 Exam Questions and Answers by morgan

Page: 3 / 35

Cisco 200-201 Exam Overview :

Exam Name: Understanding Cisco Cybersecurity Operations Fundamentals
Exam Code: 200-201 Dumps
Vendor: Cisco Certification: CCNA Cybersecurity
Questions: 476 Q&A's Shared By: morgan
Question 12

Which type of data must an engineer capture to analyze payload and header information?

Options:

A.

frame check sequence

B.

alert data

C.

full packet

D.

session logs

Discussion
Amy
I passed my exam and found your dumps 100% relevant to the actual exam.
Lacey Oct 18, 2026
Yeah, definitely. I experienced the same.
Andrew
Are these dumps helpful?
Jeremiah Oct 12, 2026
Yes, Don’t worry!!! I'm confident you'll find them to be just as helpful as I did. Good luck with your exam!
Cody
I used Cramkey Dumps to prepare and a lot of the questions on the exam were exactly what I found in their study materials.
Eric Oct 3, 2026
Really? That's great to hear! I used Cramkey Dumps too and I had the same experience. The questions were almost identical.
Conor
I recently used these dumps for my exam and I must say, I was impressed with their authentic material.
Yunus Oct 16, 2026
Exactly…….The information in the dumps is so authentic and up-to-date. Plus, the questions are very similar to what you'll see on the actual exam. I felt confident going into the exam because I had studied using Cramkey Dumps.
Question 13

A cyberattacker notices a security flaw in a software that a company is using They decide to tailor a specific worm to exploit this flaw and extract saved passwords from the software To which category of the Cyber Kill Cham model does this event belong?

Options:

A.

reconnaissance

B.

delivery

C.

weaponization

D.

exploitation

Discussion
Question 14

An engineer needs to configure network systems to detect command and control communications by decrypting ingress and egress perimeter traffic and allowing network security devices to detect malicious outbound communications. Which technology should be used to accomplish the task?

Options:

A.

digital certificates

B.

static IP addresses

C.

signatures

D.

cipher suite

Discussion
Question 15

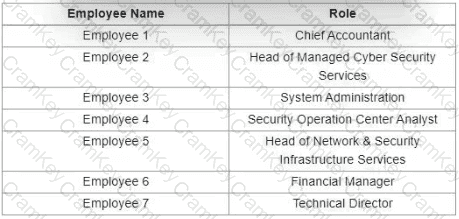
Refer to the exhibit.

Questions 15

Which stakeholders must be involved when a company workstation is compromised?

Options:

A.

Employee 1 Employee 2, Employee 3, Employee 4, Employee 5, Employee 7

B.

Employee 1, Employee 2, Employee 4, Employee 5

C.

Employee 4, Employee 6, Employee 7

D.

Employee 2, Employee 3, Employee 4, Employee 5

Discussion
Page: 3 / 35
Title
Questions
Posted

200-201
PDF

$36  $119.99

200-201 Testing Engine

$42  $139.99

200-201 PDF + Testing Engine

$54  $179.99