Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

Microsoft Updated SC-200 Exam Questions and Answers by nia

Page: 2 / 10

Microsoft SC-200 Exam Overview :

Exam Name: Microsoft Security Operations Analyst
Exam Code: SC-200 Dumps
Vendor: Microsoft Certification: Microsoft Certified: Security Operations Analyst Associate
Questions: 430 Q&A's Shared By: nia
Question 8

You need to ensure that the configuration of HuntingQuery1 meets the Microsoft Sentinel requirements.

What should you do?

Options:

A.

Add HuntingQuery1 to a livestream.

B.

Create a watch list.

C.

Create an Azure Automation rule.

D.

Add HuntingQuery1 to favorites.

Discussion
Honey
I highly recommend it. They made a big difference for me and I'm sure they'll help you too. Just make sure to use them wisely and not solely rely on them. They should be used as a supplement to your regular studies.
Antoni Oct 16, 2026
Good point. Thanks for the advice. I'll definitely keep that in mind.
Peyton
Hey guys. Guess what? I passed my exam. Thanks a lot Cramkey, your provided information was relevant and reliable.
Coby Oct 9, 2026
Thanks for sharing your experience. I think I'll give Cramkey a try for my next exam.
Ayesha
They are study materials that are designed to help students prepare for exams and certification tests. They are basically a collection of questions and answers that are likely to appear on the test.
Ayden Oct 13, 2026
That sounds interesting. Why are they useful? Planning this week, hopefully help me. Can you give me PDF if you have ?
Laila
They're such a great resource for anyone who wants to improve their exam results. I used these dumps and passed my exam!! Happy customer, always prefer. Yes, same questions as above I know you guys are perfect.
Keira Oct 26, 2026
100% right….And they're so affordable too. It's amazing how much value you get for the price.
Question 9

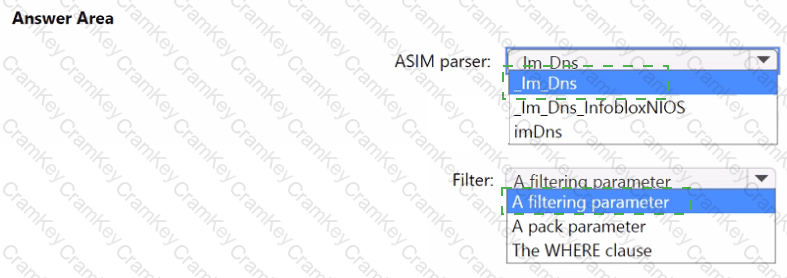
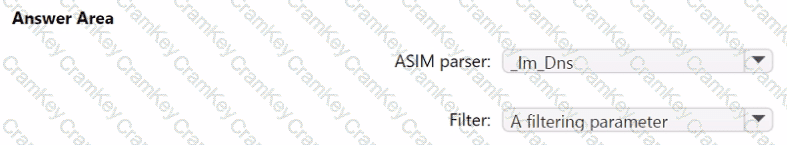
You need to implement the ASIM query for DNS requests. The solution must meet the Microsoft Sentinel requirements. How should you configure the query? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
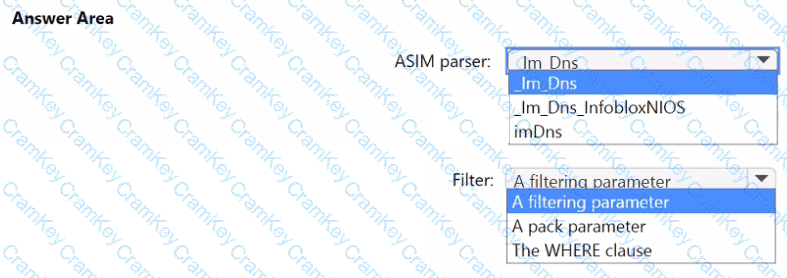
Questions 9

Options:

Discussion
Question 10

You need to ensure that the processing of incidents generated by rulequery1 meets the Microsoft Sentinel requirements.

What should you create first?

Options:

A.

a playbook with an incident trigger

B.

a playbook with an entity trigger

C.

an Azure Automation rule

D.

a playbook with an alert trigger

Discussion
Question 11

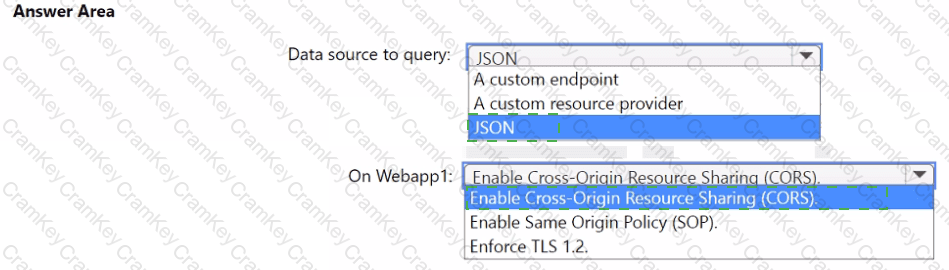
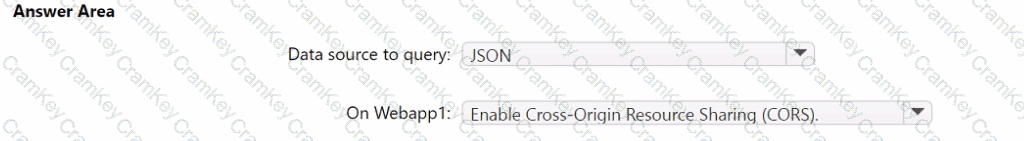
You need to implement the query for Workbook1 and Webapp1. The solution must meet the Microsoft Sentinel requirements. How should you configure the query? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
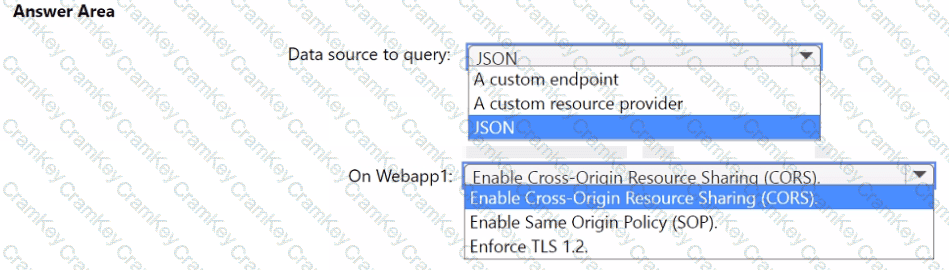

Questions 11

Options:

Discussion
Page: 2 / 10

SC-200
PDF

$42  $119.99

SC-200 Testing Engine

$49  $139.99

SC-200 PDF + Testing Engine

$63  $179.99