Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

Microsoft Updated SC-200 Exam Questions and Answers by alissa

Page: 6 / 10

Microsoft SC-200 Exam Overview :

Exam Name: Microsoft Security Operations Analyst
Exam Code: SC-200 Dumps
Vendor: Microsoft Certification: Microsoft Certified: Security Operations Analyst Associate
Questions: 430 Q&A's Shared By: alissa
Question 24

You have a Microsoft Sentinel workspace.

You need to prevent a built-in Advance Security information Model (ASIM) parse from being updated automatically.

What are two ways to achieve this goal? Each correct answer presents a complete solution.

NOTE: Each correct selection is worth one point.

Options:

A.

Redeploy the built-in parse and specify a CallerContext parameter of any and a SourceSpecificParse parameter of any.

B.

Create a hunting query that references the built-in parse.

C.

Redeploy the built-in parse and specify a CallerContext parameter of built-in.

D.

Build a custom unify parse and include the build- parse version

E.

Create an analytics rule that includes the built-in parse

Discussion
Josie
I just passed my certification exam using their dumps and I must say, I was thoroughly impressed.
Fatimah Oct 19, 2026
You’re right. The dumps were authentic and covered all the important topics. I felt confident going into the exam and it paid off.
Mariam
Do anyone think Cramkey questions can help improve exam scores?
Katie Oct 8, 2026
Absolutely! Many people have reported improved scores after using Cramkey Dumps, and there are also success stories of people passing exams on the first try. I already passed this exam. I confirmed above questions were in exam.
Josephine
I want to ask about their study material and Customer support? Can anybody guide me?
Zayd Oct 24, 2026
Yes, the dumps or study material provided by them are authentic and up to date. They have a dedicated team to assist students and make sure they have a positive experience.
Everleigh
I must say that they are updated regularly to reflect the latest exam content, so you can be sure that you are getting the most accurate information. Plus, they are easy to use and understand, so even new students can benefit from them.
Huxley Oct 10, 2026
That's great to know. So, you think new students should buy these dumps?
Miriam
Highly recommended Dumps. 100% authentic and reliable. Passed my exam with wonderful score.
Milan Oct 22, 2026
I see. Thanks for the information. I'll definitely keep Cramkey in mind for my next exam.
Question 25

You need to receive a security alert when a user attempts to sign in from a location that was never used by the other users in your organization to sign in.

Which anomaly detection policy should you use?

Options:

A.

Impossible travel

B.

Activity from anonymous IP addresses

C.

Activity from infrequent country

D.

Malware detection

Discussion
Question 26

You have a Microsoft Sentinel workspace that contains a custom workbook named Workbook1.

You need to create a visual based on the SecuntyEvent table. The solution must meet the following requirements:

• Identify the number of security events ingested during the past week.

• Display the count of events by day in a timechart

What should you add to Workbook1?

Options:

A.

a query

B.

a metric

C.

a group

D.

links or tabs

Discussion
Question 27

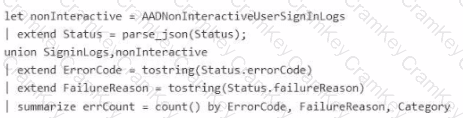
You have a Microsoft Sentinel workbook that contains the following KQL query.
Questions 27

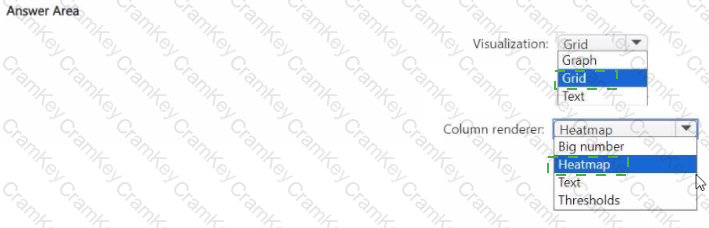
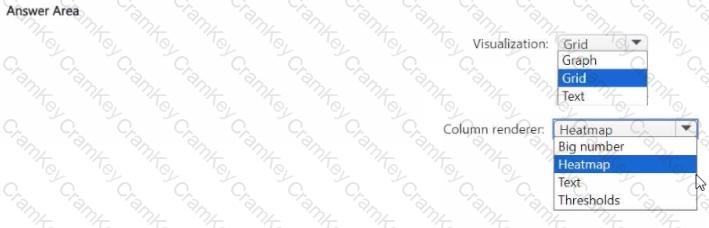
You need to create a visual that will change the color of the errCount column based on the value returned. How should you configure the visual? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.

Questions 27

Options:

Discussion
Page: 6 / 10

SC-200
PDF

$36  $119.99

SC-200 Testing Engine

$42  $139.99

SC-200 PDF + Testing Engine

$54  $179.99