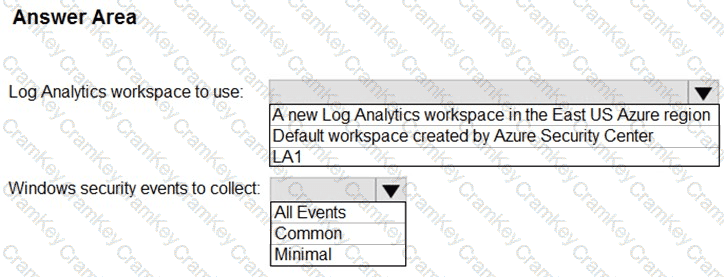
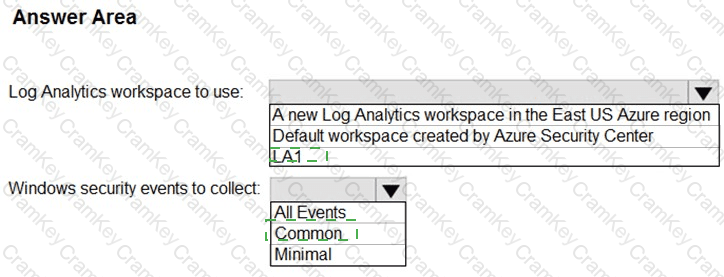
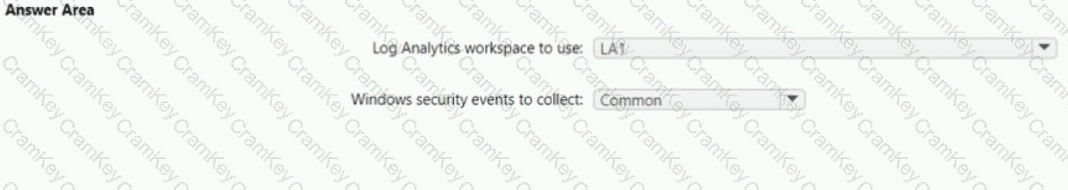
The test analytics rule must generate alerts for inbound Office 365 access by several test users and group those alerts into separate incidents—one per user . In Azure Sentinel, incident grouping by entity depends on the rule’s Entity mapping . When you create a scheduled analytics rule, under Set rule logic you map columns from your query to entities like Account , IP , or Host . Once mapped, you can configure Event grouping so alerts with the same entity value (e.g., the same Account ) are automatically grouped into a single incident. Turning suppression on/off or changing severity/tactics doesn’t influence entity-based incident grouping. Therefore, to ensure “one incident per test user account,” you must map the Acco unt entity (and any other relevant entities) in Set rule logic , then enable grouping by that entity—fulfilling the Sentinel requirement.QUESTION NO: 3 HOTSPOT
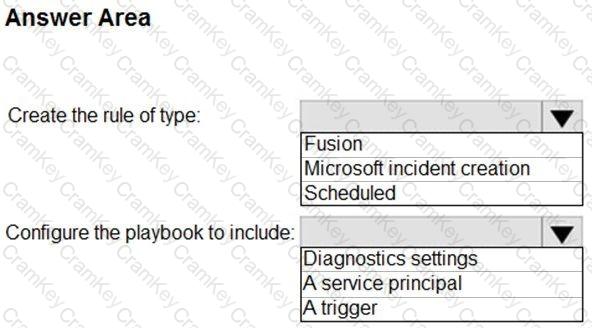
You need to create the analytics rule to meet the Azure Sentinel requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer: < map > < m x1= " 300 " x2= " 402 " y1= " 181 " y2= " 204 " ss= " 0 " a= " 0 " / > < m x1= " 294 " x2= " 386 " y1= " 295 " y2= " 321 " ss= " 0 " a= " 0 " / > < /map >
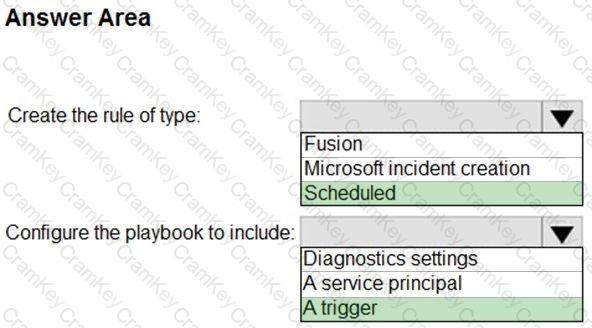
Acc ording to Microsoft Security Operations (SecOps) and Azure Sentinel documentation, when you need to create an analytics rule that executes a custom KQL query and automatically initiates a playbook , the correct configuration is to create a Scheduled rule an d ensure the playbook includes a trigger .
Here’s why:
A Scheduled analytics rule in Microsoft Sentinel (Microsoft Defender XDR portal) is designed for running custom KQL queries at defined intervals (for example, every hour or every few minutes) to detect specific patterns of suspicious activity. When the rule’s conditions are met, Sentinel generates alerts that can automatically trigger a playbook for response and automation.
A playbook in Sentinel is an Azure Logic App that automates responses to incident s or alerts. To connect a playbook to an analytics rule, it must include a trigger —specifically, the “Microsoft Sentinel Alert” or “Incident trigger.” This allows the rule to start the playbook automatically when the defined condition is met.
The other opt ions are incorrect because:
Fusion rules are built-in and use Microsoft’s machine learning to correlate signals automatically; they can’t be used for custom queries.
Microsoft incident creation rules are also built-in and handle alert-to-incident grouping logic, not custom query execution.
A service principal would be needed for permissions (e.g., admin1 configuring playbooks), but not inside the playbook itself.
Diagnostics settings apply to log collection and retention, not rule automation.
Therefore, bas ed on Microsoft Sentinel best practices and documentation:
✅ Create the rule of type: Scheduled
✅ Configure the playbook to include: A trigger