| Exam Name: | Microsoft Cybersecurity Architect | ||
| Exam Code: | SC-100 Dumps | ||
| Vendor: | Microsoft | Certification: | Microsoft Certified: Cybersecurity Architect Expert |
| Questions: | 341 Q&A's | Shared By: | ava-mae |
Your company has an Azure subscription that uses Microsoft Defender for Cloud. The company signs a contract with the United States government. You need to review the current subscription for NIST 800-53 compliance. What should you do first?
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure subscription that has Microsoft Defender for Cloud enabled.
You are evaluating the Azure Security Benchmark V3 report.
In the Secure management ports controls, you discover that you have 0 out of a potential 8 points.
You need to recommend configurations to increase the score of the Secure management ports controls.
Solution: You recommend enabling the VM Access extension on all virtual machines.
Does this meet the goal?
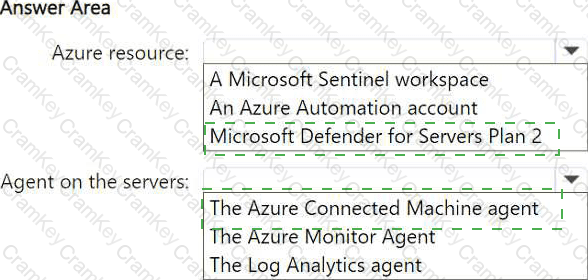
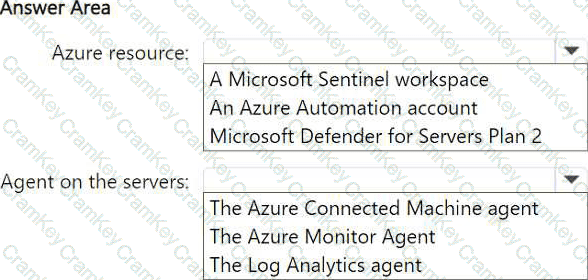
You have 1,000 on-premises servers that run Windows Server 2022 and 500 on-premises servers that run Linux.
You have an Azure subscription that contains the following resources:
• A Log Analytics workspace
• A Microsoft Defender Cloud Security Posture Management (CSPM) plan
You need to deploy Update Management for the servers.
What should you configure? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
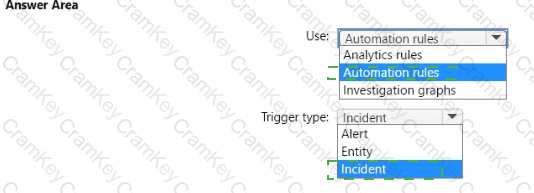
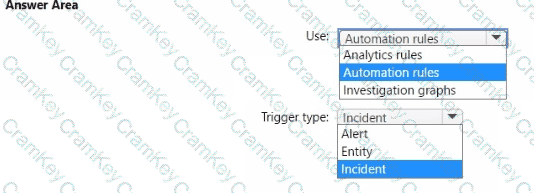
You have an Azure subscription that contains a Microsoft Sentinel workspace named MSW1. MSW1 includes 50 scheduled analytics rules.
You need to design a security orchestration automated response (SOAR) solution by using Microsoft Sentinel playbooks. The solution must meet the following requirements:
• Ensure that expiration dates can be configured when a playbook runs.
• Minimize the administrative effort required to configure individual analytics rules.
What should you use to invoke the playbooks, and which type of Microsoft Sentinel trigger should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

TESTED 14 Sep 2026