| Exam Name: | Microsoft Cybersecurity Architect | ||
| Exam Code: | SC-100 Dumps | ||
| Vendor: | Microsoft | Certification: | Microsoft Certified: Cybersecurity Architect Expert |
| Questions: | 341 Q&A's | Shared By: | veronica |
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have a Microsoft 365 subscription that uses Microsoft Defender XDR. The subscription contains 500 devices that are enrolled in Microsoft Intune. The subscription contains 500 users that connect to external software as a service (SaaS) apps by using the devices.
You need to implement a solution that meets the following requirements:
• Allows user access to SaaS apps that Microsoft has identified as low risk.
• Blocks user access to Saas apps that Microsoft has identified as high risk.
Solution: From Microsoft Defender for Cloud Apps, you configure a cloud discovery policy and unsanction risky apps.
Does this meet the goal?
You have an Azure subscription that contains 15 custom apps. The source files for the apps are stored in Git repositories. The apps are deployed by using Azure DevOps.
You need to recommend a DevSecOps solution to implement static application security testing (SAST) of the app code to identify hard-coded secrets.
What should you include in the recommendation?
Your company is designing an application architecture for Azure App Service Environment (ASE) web apps as shown in the exhibit. (Click the Exhibit tab.)
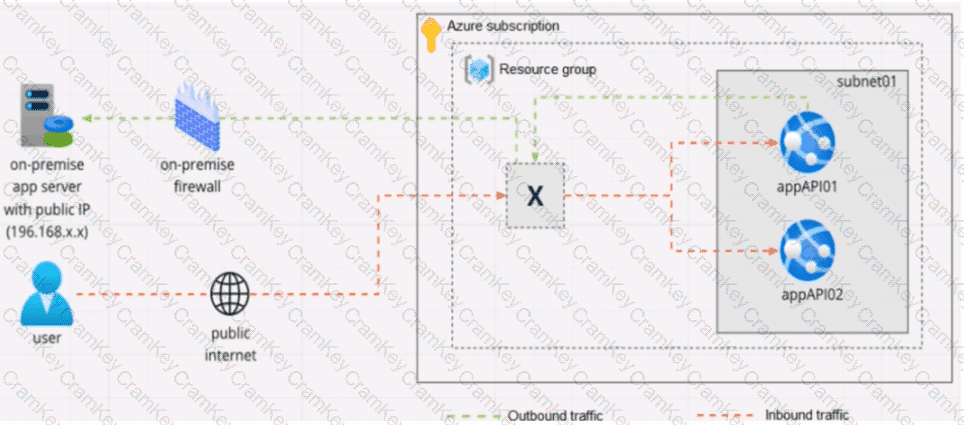
Communication between the on-premises network and Azure uses an ExpressRoute connection.
You need to recommend a solution to ensure that the web apps can communicate with the on-premises application server. The solution must minimize the number of public IP addresses that are allowed to access the on-premises network.
What should you include in the recommendation?
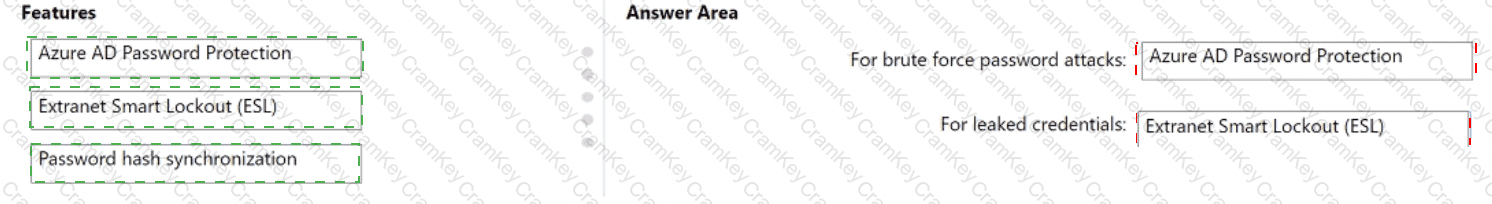
You have a hybrid Azure AD tenant that has pass-through authentication enabled.
You are designing an identity security strategy.
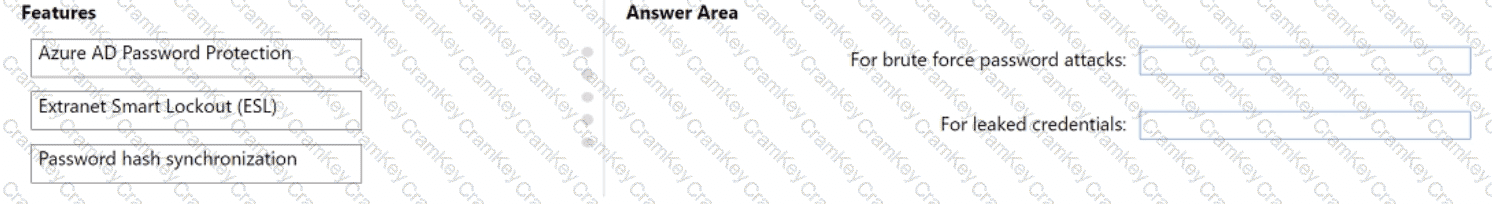
You need to minimize the impact of brute force password attacks and leaked credentials of hybrid identities.
What should you include in the design? To answer, drag the appropriate features to the correct requirements. Each feature may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.

TESTED 14 Sep 2026