Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

Cisco Updated 350-201 Exam Questions and Answers by bobbie

Page: 3 / 10

Cisco 350-201 Exam Overview :

Exam Name: Performing Cybersecurity Using Cisco Security Technologies
Exam Code: 350-201 Dumps
Vendor: Cisco Certification: CCNP Cybersecurity
Questions: 139 Q&A's Shared By: bobbie
Question 12

An engineer returned to work and realized that payments that were received over the weekend were sent to the wrong recipient. The engineer discovered that the SaaS tool that processes these payments was down over the weekend. Which step should the engineer take first?

Options:

A.

Utilize the SaaS tool team to gather more information on the potential breach

B.

Contact the incident response team to inform them of a potential breach

C.

Organize a meeting to discuss the services that may be affected

D.

Request that the purchasing department creates and sends the payments manually

Discussion
Question 13

A SOC analyst is notified by the network monitoring tool that there are unusual types of internal traffic on IP subnet 103.861.2117.0/24. The analyst discovers unexplained encrypted data files on a computer system that belongs on that specific subnet. What is the cause of the issue?

Options:

A.

DDoS attack

B.

phishing attack

C.

virus outbreak

D.

malware outbreak

Discussion
Question 14

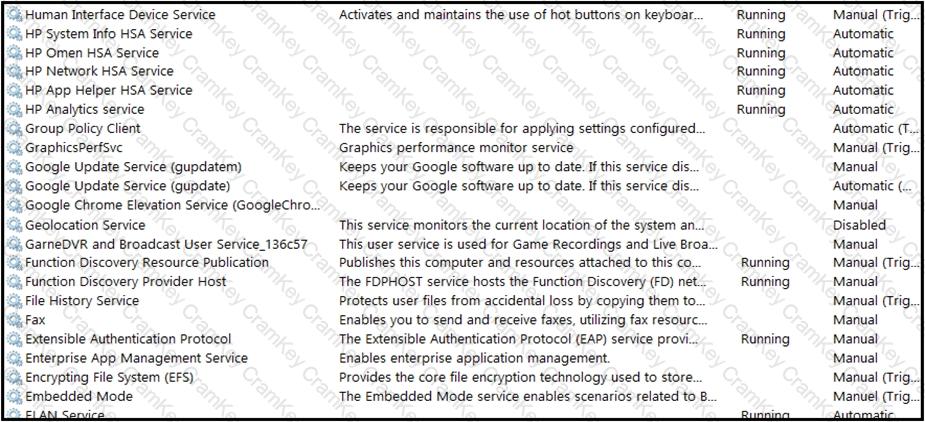
Refer to the exhibit.

Questions 14

An engineer received multiple reports from employees unable to log into systems with the error: The Group Policy Client service failed to logon – Access is denied. Through further analysis, the engineer discovered several unexpected modifications to system settings. Which type of breach is occurring?

Options:

A.

malware break

B.

data theft

C.

elevation of privileges

D.

denial-of-service

Discussion
Question 15

A malware outbreak is detected by the SIEM and is confirmed as a true positive. The incident response team follows the playbook to mitigate the threat. What is the first action for the incident response team?

Options:

A.

Assess the network for unexpected behavior

B.

Isolate critical hosts from the network

C.

Patch detected vulnerabilities from critical hosts

D.

Perform analysis based on the established risk factors

Discussion
Nadia
Why these dumps are important? Can I pass my exam without these dumps?
Julian Sep 19, 2026
The questions in the Cramkey dumps are explained in detail and there are also study notes and reference materials provided. This made it easier for me to understand the concepts and retain the information better.
Kingsley
Do anyone guide my how these dumps would be helpful for new students like me?
Haris Sep 22, 2026
Absolutely! They are highly recommended for anyone looking to pass their certification exam. The dumps are easy to understand and follow, making it easier for you to study and retain the information.
Lennie
I passed my exam and achieved wonderful score, I highly recommend it.
Emelia Sep 25, 2026
I think I'll give Cramkey a try next time I take a certification exam. Thanks for the recommendation!
Ernest
That's amazing. I think I'm going to give Cramkey Dumps a try for my next exam. Thanks for telling me about them! CramKey admin please share more questions……You guys are amazing.
Nate Sep 5, 2026
I failed last week, I never know this site , but amazed to see all these questions were in my exam week before. I feel bad now, why I didn’t bother this site. Thanks Cramkey, Excellent Job.
Page: 3 / 10

350-201
PDF

$34.5  $114.99

350-201 Testing Engine

$40.5  $134.99

350-201 PDF + Testing Engine

$52.5  $174.99