Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

Cisco Updated 350-201 Exam Questions and Answers by lucie

Page: 7 / 10

Cisco 350-201 Exam Overview :

Exam Name: Performing Cybersecurity Using Cisco Security Technologies
Exam Code: 350-201 Dumps
Vendor: Cisco Certification: CCNP Cybersecurity
Questions: 139 Q&A's Shared By: lucie
Question 28

An engineer wants to review the packet overviews of SNORT alerts. When printing the SNORT alerts, all the packet headers are included, and the file is too large to utilize. Which action is needed to correct this problem?

Options:

A.

Modify the alert rule to “output alert_syslog: output log”

B.

Modify the output module rule to “output alert_quick: output filename”

C.

Modify the alert rule to “output alert_syslog: output header”

D.

Modify the output module rule to “output alert_fast: output filename”

Discussion
Question 29

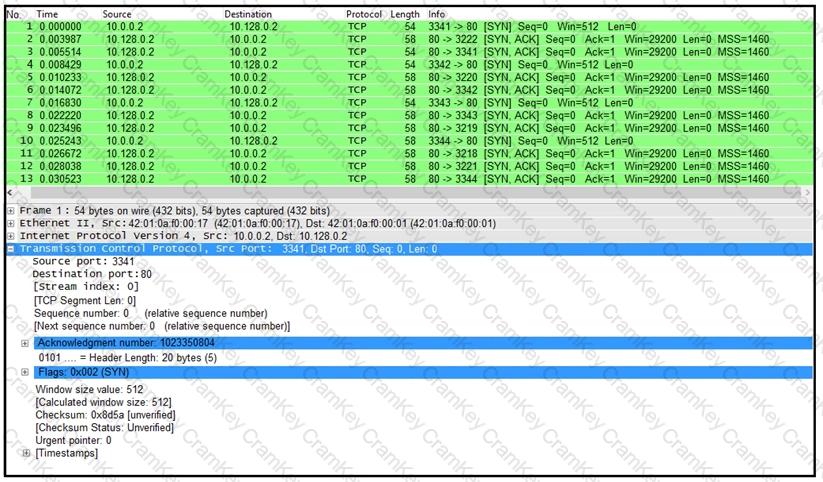
Refer to the exhibit.

Questions 29

What is the threat in this Wireshark traffic capture?

Options:

A.

A high rate of SYN packets being sent from multiple sources toward a single destination IP

B.

A flood of ACK packets coming from a single source IP to multiple destination IPs

C.

A high rate of SYN packets being sent from a single source IP toward multiple destination IPs

D.

A flood of SYN packets coming from a single source IP to a single destination IP

Discussion
Question 30

A payroll administrator noticed unexpected changes within a piece of software and reported the incident to the incident response team. Which actions should be taken at this step in the incident response workflow?

Options:

A.

Classify the criticality of the information, research the attacker’s motives, and identify missing patches

B.

Determine the damage to the business, extract reports, and save evidence according to a chain of custody

C.

Classify the attack vector, understand the scope of the event, and identify the vulnerabilities being exploited

D.

Determine the attack surface, evaluate the risks involved, and communicate the incident according to the escalation plan

Discussion
Pippa
I was so happy to see that almost all the questions on the exam were exactly what I found in their Dumps.
Anastasia Sep 23, 2026
You are right…It was amazing! The Cramkey Dumps were so comprehensive and well-organized, it made studying for the exam a breeze.
Annabel
I recently used them for my exam and I passed it with excellent score. I am impressed.
Amirah Sep 4, 2026
I passed too. The questions I saw in the actual exam were exactly the same as the ones in the Cramkey Dumps. I was able to answer the questions confidently because I had already seen and studied them.
Anaya
I found so many of the same questions on the real exam that I had already seen in the Cramkey Dumps. Thank you so much for making exam so easy for me. I passed it successfully!!!
Nina Sep 20, 2026
It's true! I felt so much more confident going into the exam because I had already seen and understood the questions.
Lois
I passed my exam with wonderful score. Their dumps are 100% valid and I felt confident during the exam.
Ernie Sep 1, 2026
Absolutely. The best part is, the answers in the dumps were correct. So, I felt confident and well-prepared for the exam.
Inaaya
Are these Dumps worth buying?
Fraser Sep 20, 2026
Yes, of course, they are necessary to pass the exam. They give you an insight into the types of questions that could come up and help you prepare effectively.
Question 31

An engineer implemented a SOAR workflow to detect and respond to incorrect login attempts and anomalous user behavior. Since the implementation, the security team has received dozens of false positive alerts and negative feedback from system administrators and privileged users. Several legitimate users were tagged as a threat and their accounts blocked, or credentials reset because of unexpected login times and incorrectly

typed credentials. How should the workflow be improved to resolve these issues?

Options:

A.

Meet with privileged users to increase awareness and modify the rules for threat tags and anomalous behavior alerts

B.

Change the SOAR configuration flow to remove the automatic remediation that is increasing the false positives and triggering threats

C.

Add a confirmation step through which SOAR informs the affected user and asks them to confirm whether they made the attempts

D.

Increase incorrect login tries and tune anomalous user behavior not to affect privileged accounts

Discussion
Page: 7 / 10

350-201
PDF

$40.25  $114.99

350-201 Testing Engine

$47.25  $134.99

350-201 PDF + Testing Engine

$61.25  $174.99