Month End Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: mystc75

Cisco Updated 350-201 Exam Questions and Answers by aron

Page: 2 / 10

Cisco 350-201 Exam Overview :

Exam Name: Performing Cybersecurity Using Cisco Security Technologies
Exam Code: 350-201 Dumps
Vendor: Cisco Certification: CCNP Cybersecurity
Questions: 139 Q&A's Shared By: aron
Question 8

What is needed to assess risk mitigation effectiveness in an organization?

Options:

A.

analysis of key performance indicators

B.

compliance with security standards

C.

cost-effectiveness of control measures

D.

updated list of vulnerable systems

Discussion
Josie
I just passed my certification exam using their dumps and I must say, I was thoroughly impressed.
Fatimah Aug 26, 2026
You’re right. The dumps were authentic and covered all the important topics. I felt confident going into the exam and it paid off.
Alessia
Amazing Dumps. Found almost all questions in actual exam whih I prepared from these valuable dumps. Recommended!!!!
Belle Aug 11, 2026
That's impressive. I've been struggling with finding good study material for my certification. Maybe I should give Cramkey Dumps a try.
Ernest
That's amazing. I think I'm going to give Cramkey Dumps a try for my next exam. Thanks for telling me about them! CramKey admin please share more questions……You guys are amazing.
Nate Aug 4, 2026
I failed last week, I never know this site , but amazed to see all these questions were in my exam week before. I feel bad now, why I didn’t bother this site. Thanks Cramkey, Excellent Job.
Cody
I used Cramkey Dumps to prepare and a lot of the questions on the exam were exactly what I found in their study materials.
Eric Aug 3, 2026
Really? That's great to hear! I used Cramkey Dumps too and I had the same experience. The questions were almost identical.
Question 9

An engineer is going through vulnerability triage with company management because of a recent malware outbreak from which 21 affected assets need to be patched or remediated. Management decides not to prioritize fixing the assets and accepts the vulnerabilities. What is the next step the engineer should take?

Options:

A.

Investigate the vulnerability to prevent further spread

B.

Acknowledge the vulnerabilities and document the risk

C.

Apply vendor patches or available hot fixes

D.

Isolate the assets affected in a separate network

Discussion
Question 10

Which command does an engineer use to set read/write/execute access on a folder for everyone who reaches the resource?

Options:

A.

chmod 666

B.

chmod 774

C.

chmod 775

D.

chmod 777

Discussion
Question 11

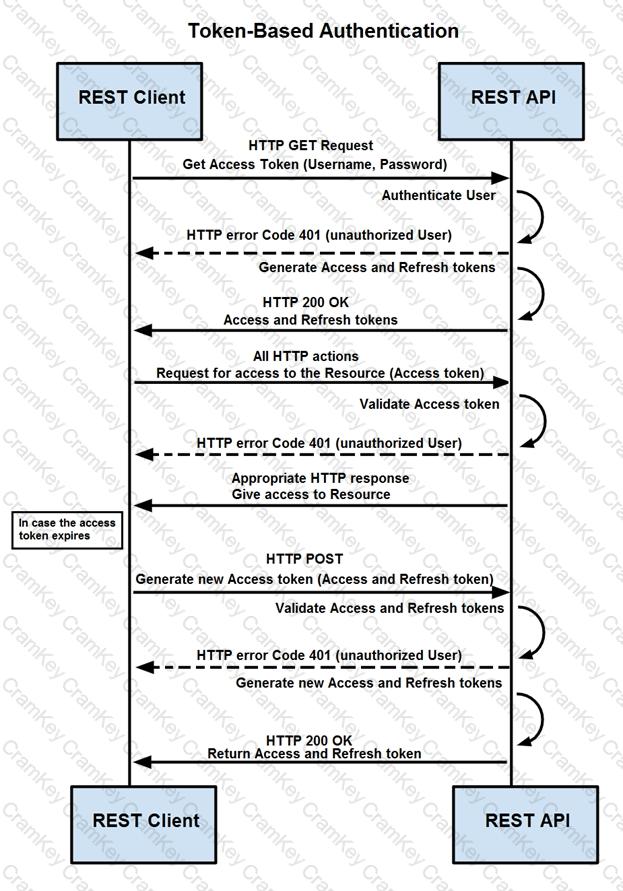
Refer to the exhibit.

Questions 11

How are tokens authenticated when the REST API on a device is accessed from a REST API client?

Options:

A.

The token is obtained by providing a password. The REST client requests access to a resource using the access token. The REST API validates the access token and gives access to the resource.

B.

The token is obtained by providing a password. The REST API requests access to a resource using the access token, validates the access token, and gives access to the resource.

C.

The token is obtained before providing a password. The REST API provides resource access, refreshes

tokens, and returns them to the REST client. The REST client requests access to a resource using the access token.

D.

The token is obtained before providing a password. The REST client provides access to a resource using the access token. The REST API encrypts the access token and gives access to the resource.

Discussion
Page: 2 / 10

350-201
PDF

$28.75  $114.99

350-201 Testing Engine

$33.75  $134.99

350-201 PDF + Testing Engine

$43.75  $174.99