Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

Cisco Updated 350-201 Exam Questions and Answers by ella-mae

Page: 6 / 10

Cisco 350-201 Exam Overview :

Exam Name: Performing Cybersecurity Using Cisco Security Technologies
Exam Code: 350-201 Dumps
Vendor: Cisco Certification: CCNP Cybersecurity
Questions: 139 Q&A's Shared By: ella-mae
Question 24

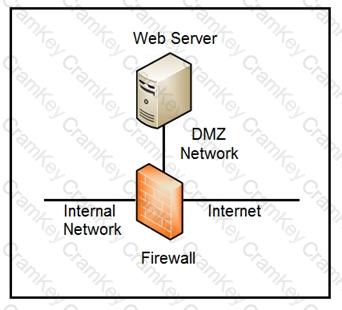
Refer to the exhibit.

Questions 24

Which two steps mitigate attacks on the webserver from the Internet? (Choose two.)

Options:

A.

Create an ACL on the firewall to allow only TLS 1.3

B.

Implement a proxy server in the DMZ network

C.

Create an ACL on the firewall to allow only external connections

D.

Move the webserver to the internal network

Discussion
Question 25

What is a limitation of cyber security risk insurance?

Options:

A.

It does not cover the costs to restore stolen identities as a result of a cyber attack

B.

It does not cover the costs to hire forensics experts to analyze the cyber attack

C.

It does not cover the costs of damage done by third parties as a result of a cyber attack

D.

It does not cover the costs to hire a public relations company to help deal with a cyber attack

Discussion
Question 26

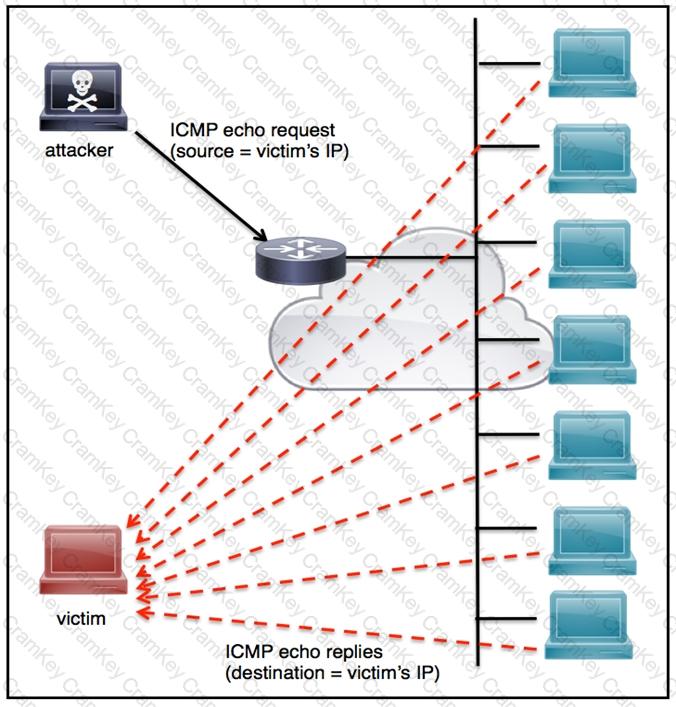
Refer to the exhibit.

Questions 26

An engineer must tune the Cisco IOS device to mitigate an attack that is broadcasting a large number of ICMP packets. The attack is sending the victim’s spoofed source IP to a network using an IP broadcast address that causes devices in the network to respond back to the source IP address. Which action does the engineer recommend?

Options:

A.

Use command ip verify reverse-path interface

B.

Use global configuration command service tcp-keepalives-out

C.

Use subinterface command no ip directed-broadcast

D.

Use logging trap 6

Discussion
Question 27

A SOC analyst is investigating a recent email delivered to a high-value user for a customer whose network their organization monitors. The email includes a suspicious attachment titled “Invoice RE: 0004489”. The

hash of the file is gathered from the Cisco Email Security Appliance. After searching Open Source Intelligence, no available history of this hash is found anywhere on the web. What is the next step in analyzing this attachment to allow the analyst to gather indicators of compromise?

Options:

A.

Run and analyze the DLP Incident Summary Report from the Email Security Appliance

B.

Ask the company to execute the payload for real time analysis

C.

Investigate further in open source repositories using YARA to find matches

D.

Obtain a copy of the file for detonation in a sandbox

Discussion
Cody
I used Cramkey Dumps to prepare and a lot of the questions on the exam were exactly what I found in their study materials.
Eric Oct 3, 2026
Really? That's great to hear! I used Cramkey Dumps too and I had the same experience. The questions were almost identical.
Kylo
What makes Cramkey Dumps so reliable? Please guide.
Sami Oct 20, 2026
Well, for starters, they have a team of experts who are constantly updating their material to reflect the latest changes in the industry. Plus, they have a huge database of questions and answers, which makes it easy to study and prepare for the exam.
Vienna
I highly recommend them. They are offering exact questions that we need to prepare our exam.
Jensen Oct 3, 2026
That's great. I think I'll give Cramkey a try next time I take a certification exam. Thanks for the recommendation!
Wyatt
Passed my exam… Thank you so much for your excellent Exam Dumps.
Arjun Oct 19, 2026
That sounds really useful. I'll definitely check it out.
Faye
Yayyyy. I passed my exam. I think all students give these dumps a try.
Emmeline Oct 7, 2026
Definitely! I have no doubt new students will find them to be just as helpful as I did.
Page: 6 / 10

350-201
PDF

$36  $119.99

350-201 Testing Engine

$42  $139.99

350-201 PDF + Testing Engine

$54  $179.99