Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

CompTIA Updated PT0-003 Exam Questions and Answers by aron

Page: 15 / 24

CompTIA PT0-003 Exam Overview :

Exam Name: CompTIA PenTest+ Exam
Exam Code: PT0-003 Dumps
Vendor: CompTIA Certification: PenTest+
Questions: 364 Q&A's Shared By: aron
Question 60

A penetration tester identifies multiple connections to public LLMs. The client’s IT team has not authorized the use of all of these LLMs. Which of the following best describes the risk to the client?

Options:

A.

Accidental loss of internal data

B.

Public disclosure of intellectual property

C.

Exfiltration of employee credentials

D.

Prompt injection vulnerability

Discussion
Anaya
I found so many of the same questions on the real exam that I had already seen in the Cramkey Dumps. Thank you so much for making exam so easy for me. I passed it successfully!!!
Nina Sep 20, 2026
It's true! I felt so much more confident going into the exam because I had already seen and understood the questions.
Vienna
I highly recommend them. They are offering exact questions that we need to prepare our exam.
Jensen Sep 6, 2026
That's great. I think I'll give Cramkey a try next time I take a certification exam. Thanks for the recommendation!
Nia
Why are these Dumps so important for students these days?
Mary Sep 27, 2026
With the constantly changing technology and advancements in the industry, it's important for students to have access to accurate and valid study material. Cramkey Dumps provide just that. They are constantly updated to reflect the latest changes and ensure that the information is up-to-date.
Ace
No problem! I highly recommend Cramkey Dumps to anyone looking to pass their certification exams. They will help you feel confident and prepared on exam day. Good luck!
Harris Sep 15, 2026
That sounds amazing. I'll definitely check them out. Thanks for the recommendation!
Ivan
I tried these dumps for my recent certification exam and I found it pretty helpful.
Elis Aug 31, 2026
Agree!!! The questions in the dumps were quite similar to what came up in the actual exam. It gave me a good idea of the types of questions to expect and helped me revise efficiently.
Question 61

A penetration tester exports the following CSV data from a scanner. The tester wants to parse the data using Bash and input it into another tool.

CSV data before parsing:

cat data.csv

Host, IP, Username, Password

WINS212, 10.111.41.74, admin, Spring11

HRDB, 10.13.9.212, hradmin, HRForTheWin

WAS01, 192.168.23.13, admin, Snowfall97

Intended output:

admin Spring11

hradmin HRForTheWin

admin Snowfall97

Which of the following will provide the intended output?

Options:

A.

cat data.csv | grep -v " IP " | cut -d " , " -f 3,4 | sed -e ' s/,/ / '

B.

cat data.csv | find . -iname Username,Password

C.

cat data.csv | grep ' username|Password '

D.

cat data.csv | grep -i " admin " | grep -v " WINS212\|HRDB\|WAS01\|10.111.41.74\|10.13.9.212\|192.168.23.13 "

Discussion
Question 62

A penetration tester runs a vulnerability scan that identifies several issues across numerous customer hosts. The executive report outlines the following:
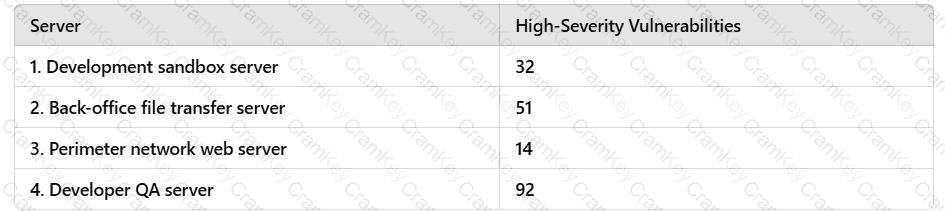
Questions 62

The client is concerned about the availability of its consumer-facing production application. Which of the following hosts should the penetration tester select for additional manual testing?

Options:

A.

Server 1

B.

Server 2

C.

Server 3

D.

Server 4

Discussion
Question 63

Which of the following best describes the importance of including the attack steps in a penetration test report?

Options:

A.

It easily provides the recommended mitigations.

B.

It ensures results can be independently verified.

C.

It proves the penetration tester’s competency to the customer.

D.

It demonstrates the difficulty of exploiting specific vulnerabilities in the kill chain.

Discussion
Page: 15 / 24
Title
Questions
Posted

PT0-003
PDF

$36.75  $104.99

PT0-003 Testing Engine

$43.75  $124.99

PT0-003 PDF + Testing Engine

$57.75  $164.99

