Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

CompTIA Updated PT0-003 Exam Questions and Answers by uthman

Page: 21 / 24

CompTIA PT0-003 Exam Overview :

Exam Name: CompTIA PenTest+ Exam
Exam Code: PT0-003 Dumps
Vendor: CompTIA Certification: PenTest+
Questions: 375 Q&A's Shared By: uthman
Question 84

A penetration tester completes a scan and sees the following output on a host:

bash

Copy code

Nmap scan report for victim (10.10.10.10)

Host is up (0.0001s latency)

PORT STATE SERVICE

161/udp open|filtered snmp

445/tcp open microsoft-ds

3389/tcp open microsoft-ds

Running Microsoft Windows 7

OS CPE: cpe:/o:microsoft:windows_7_sp0

The tester wants to obtain shell access. Which of the following related exploits should the tester try first?

Options:

A.

exploit/windows/smb/psexec

B.

exploit/windows/smb/ms08_067_netapi

C.

exploit/windows/smb/ms17_010_eternalblue

D.

auxiliary/scanner/snmp/snmp_login

Discussion
Question 85

As part of a security audit, a penetration tester finds an internal application that accepts unexpected user inputs, leading to the execution of arbitrary commands. Which of the following techniques would the penetration tester most likely use to access the sensitive data?

Options:

A.

Logic bomb

B.

SQL injection

C.

Brute-force attack

D.

Cross-site scripting

Discussion
Question 86

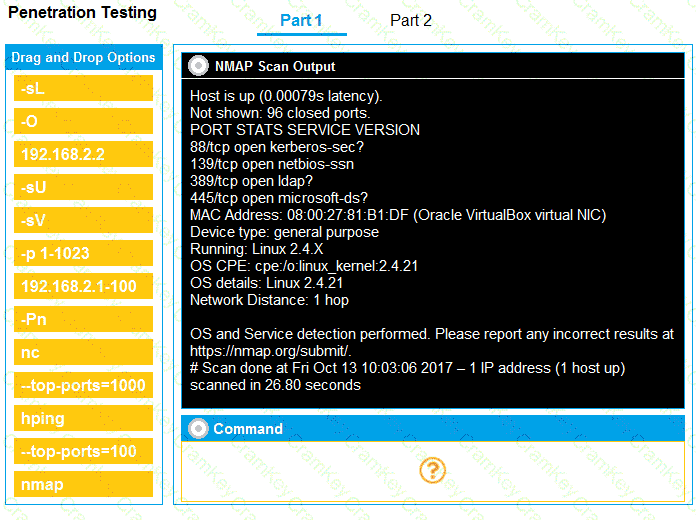
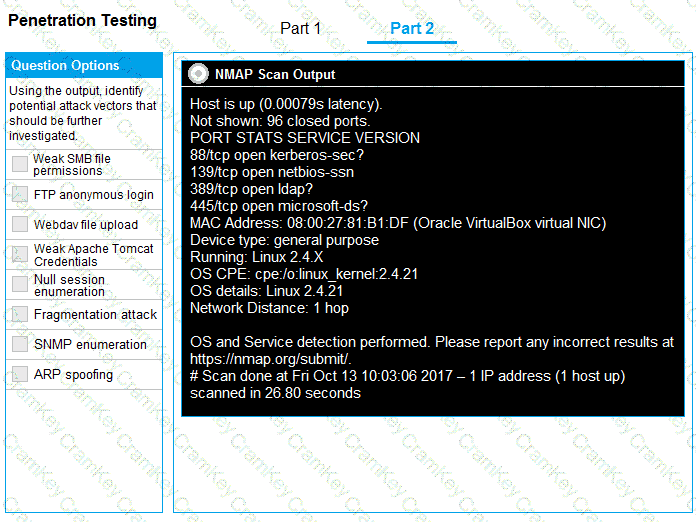
You are a penetration tester running port scans on a server.

INSTRUCTIONS

Part 1: Given the output, construct the command that was used to generate this output from the available options.

Part 2: Once the command is appropriately constructed, use the given output to identify the potential attack vectors that should be investigated further.

If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
Questions 86

Questions 86

Options:

Discussion
Ace
No problem! I highly recommend Cramkey Dumps to anyone looking to pass their certification exams. They will help you feel confident and prepared on exam day. Good luck!
Harris Oct 18, 2026
That sounds amazing. I'll definitely check them out. Thanks for the recommendation!
Faye
Yayyyy. I passed my exam. I think all students give these dumps a try.
Emmeline Oct 7, 2026
Definitely! I have no doubt new students will find them to be just as helpful as I did.
Reeva
Wow what a success I achieved today. Thank you so much Cramkey for amazing Dumps. All students must try it.
Amari Oct 27, 2026
Wow, that's impressive. I'll definitely keep Cramkey in mind for my next exam.
Elise
I've heard that Cramkey is one of the best websites for exam dumps. They have a high passing rate and the questions are always up-to-date. Is it true?
Cian Oct 27, 2026
Definitely. The dumps are constantly updated to reflect the latest changes in the certification exams. And I also appreciate how they provide explanations for the answers, so I could understand the reasoning behind each question.
Rosalie
I passed. I would like to tell all students that they should definitely give Cramkey Dumps a try.
Maja Oct 21, 2026
That sounds great. I'll definitely check them out. Thanks for the suggestion!
Question 87

A penetration tester completes a scan and sees the following Nmap output on a host:

Nmap scan report for victim (10.10.10.10)

Host is up (0.0001s latency)

PORT STATE SERVICE

161/udp open snmp

445/tcp open microsoft-ds

3389/tcp open ms-wbt-server

Running Microsoft Windows 7

OS CPE: cpe:/o:microsoft:windows_7::sp0

The tester wants to obtain shell access. Which of the following related exploits should the tester try first?

Options:

A.

exploit/windows/smb/psexec

B.

exploit/windows/smb/ms08_067_netapi

C.

exploit/windows/smb/ms17_010_eternalblue

D.

auxiliary/scanner/snmp/snmp_login

Discussion
Page: 21 / 24
Title
Questions
Posted

PT0-003
PDF

$27.5  $109.99

PT0-003 Testing Engine

$32.5  $129.99

PT0-003 PDF + Testing Engine

$42.5  $169.99

