Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

CompTIA Updated PT0-003 Exam Questions and Answers by tessa

Page: 18 / 24

CompTIA PT0-003 Exam Overview :

Exam Name: CompTIA PenTest+ Exam
Exam Code: PT0-003 Dumps
Vendor: CompTIA Certification: PenTest+
Questions: 364 Q&A's Shared By: tessa
Question 72

A penetration tester gains access to a host with many applications that load at startup and run as SYSTEM. The penetration tester runs a command and receives the following output:

User accounts for \COMPTIA-Host

CompTIA User DefaultAccount Guest

CompTIA Admin CompTIA Accountant

The command completed successfully.

Which of the following attacks will most likely allow the penetration tester to escalate privileges?

Options:

A.

Credential dumping

B.

Local file inclusion

C.

Unquoted service path injection

D.

Process hijacking

Discussion
Nia
Why are these Dumps so important for students these days?
Mary Sep 27, 2026
With the constantly changing technology and advancements in the industry, it's important for students to have access to accurate and valid study material. Cramkey Dumps provide just that. They are constantly updated to reflect the latest changes and ensure that the information is up-to-date.
Teddie
yes, I passed my exam with wonderful score, Accurate and valid dumps.
Isla-Rose Sep 25, 2026
Absolutely! The questions in the dumps were almost identical to the ones that appeared in the actual exam. I was able to answer almost all of them correctly.
Fatima
Hey I passed my exam. The world needs to know about it. I have never seen real exam questions on any other exam preparation resource like I saw on Cramkey Dumps.
Niamh Sep 16, 2026
That's true. Cramkey Dumps are simply the best when it comes to preparing for the certification exam. They have all the key information you need and the questions are very similar to what you'll see on the actual exam.
Miley
Hey, I tried Cramkey Dumps for my IT certification exam. They are really awesome and helped me pass my exam with wonderful score.
Megan Sep 16, 2026
That’s great!!! I’ll definitely give it a try. Thanks!!!
Wyatt
Passed my exam… Thank you so much for your excellent Exam Dumps.
Arjun Sep 19, 2026
That sounds really useful. I'll definitely check it out.
Question 73

During an assessment, a penetration tester runs the following command from a Linux machine:

GetUsersSPNs.py -dc-ip 172.16.1.1 DOMAIN.LOCAL/aholliday -request

Which of the following is the penetration tester trying to do?

Options:

A.

Crack the user password for aholliday

B.

Download all TGS tickets for offline processing

C.

Perform a pass-the-hash attack using the hash for aholliday

D.

Perform password spraying

Discussion
Question 74

Which of the following methods should a physical penetration tester employ to access a rarely used door that has electronic locking mechanisms?

Options:

A.

Lock picking

B.

Impersonating

C.

Jamming

D.

Tailgating

E.

Bypassing

Discussion
Question 75

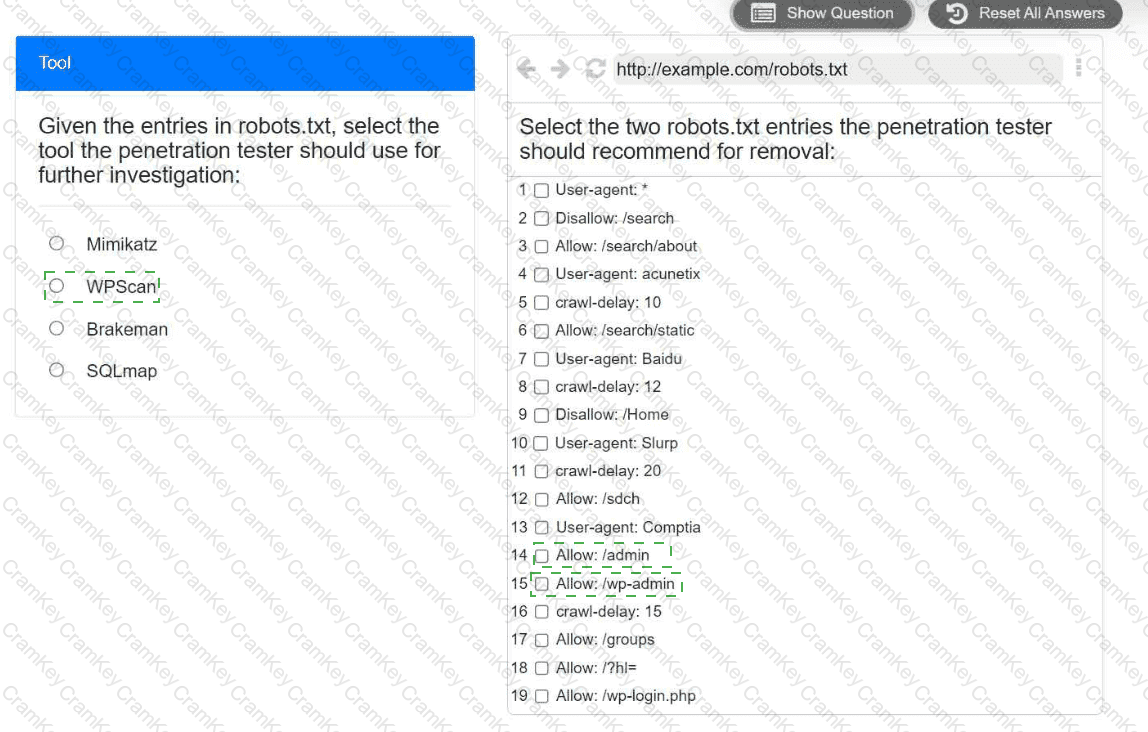
A penetration tester is performing reconnaissance for a web application assessment. Upon investigation, the tester reviews the robots.txt file for items of interest.

INSTRUCTIONS

Select the tool the penetration tester should use for further investigation.

Select the two entries in the robots.txt file that the penetration tester should recommend for removal.
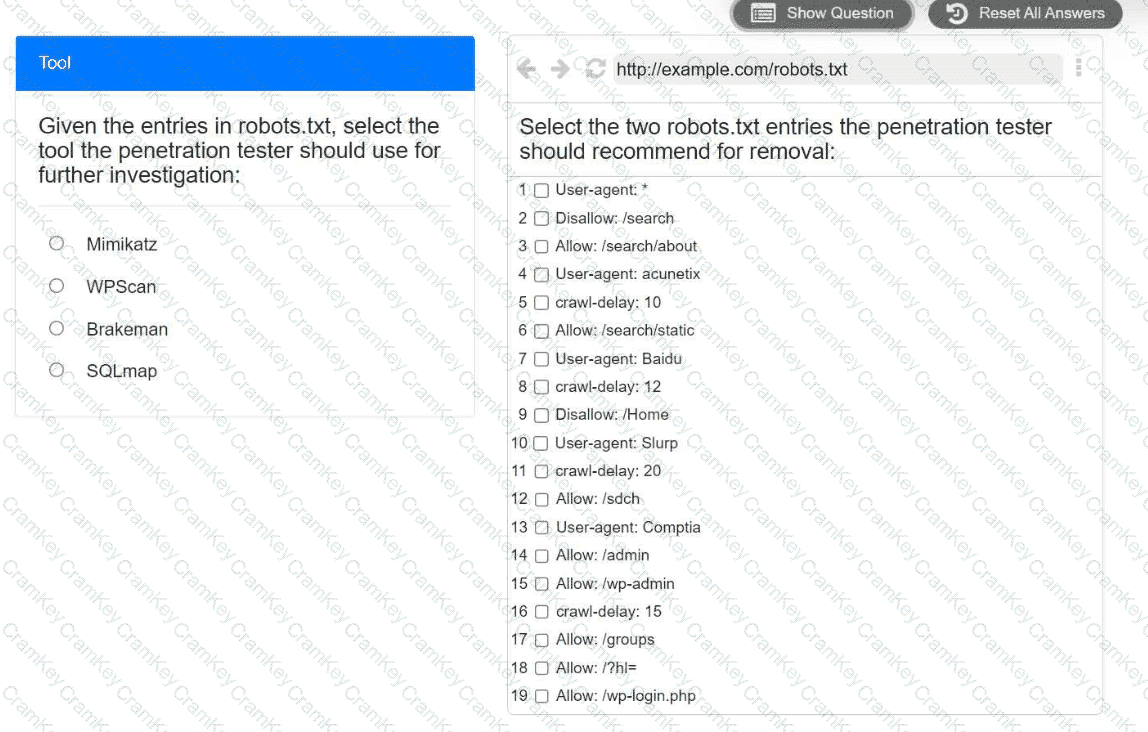

Questions 75

Options:

Discussion
Page: 18 / 24
Title
Questions
Posted

PT0-003
PDF

$31.5  $104.99

PT0-003 Testing Engine

$37.5  $124.99

PT0-003 PDF + Testing Engine

$49.5  $164.99