Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

Page: 1 / 25

CompTIA CASP CompTIA SecurityX Certification Exam

CompTIA SecurityX Certification Exam

Last Update Nov 17, 2026
Total Questions : 344

To help you prepare for the CAS-005 CompTIA exam, we are offering free CAS-005 CompTIA exam questions. All you need to do is sign up, provide your details, and prepare with the free CAS-005 practice questions. Once you have done that, you will have access to the entire pool of CompTIA SecurityX Certification Exam CAS-005 test questions which will help you better prepare for the exam. Additionally, you can also find a range of CompTIA SecurityX Certification Exam resources online to help you better understand the topics covered on the exam, such as CompTIA SecurityX Certification Exam CAS-005 video tutorials, blogs, study guides, and more. Additionally, you can also practice with realistic CompTIA CAS-005 exam simulations and get feedback on your progress. Finally, you can also share your progress with friends and family and get encouragement and support from them.

Questions 2

A systems engineer is configuring SSO for a business that will be using SaaS applications for its remote-only workforce. Privileged actions in SaaS applications must be allowed only from corporate mobile devices that meet minimum security requirements, but BYOD must also be permitted for other activity. Which of the following would best meet this objective?

Options:

A.  

Block any connections from outside the business ' s network security boundary.

B.  

Install machine certificates on corporate devices and perform checks against the clients.

C.  

Configure device attestations and continuous authorization controls.

D.  

Deploy application protection policies using a corporate, cloud-based MDM solution.

Discussion 0
Questions 3

An organization with a remote workforce has a new client with the following requirements:

    Consultants need to travel to the client site.

    The company has proprietary information on its hard drives.

    The company prohibits BYOD.

Which of the following would be the most beneficial for the organization to implement?

Options:

A.  

Virtual hardware

B.  

Measured boot

C.  

Secure enclave

D.  

Host-based encryption

Discussion 0
Questions 4

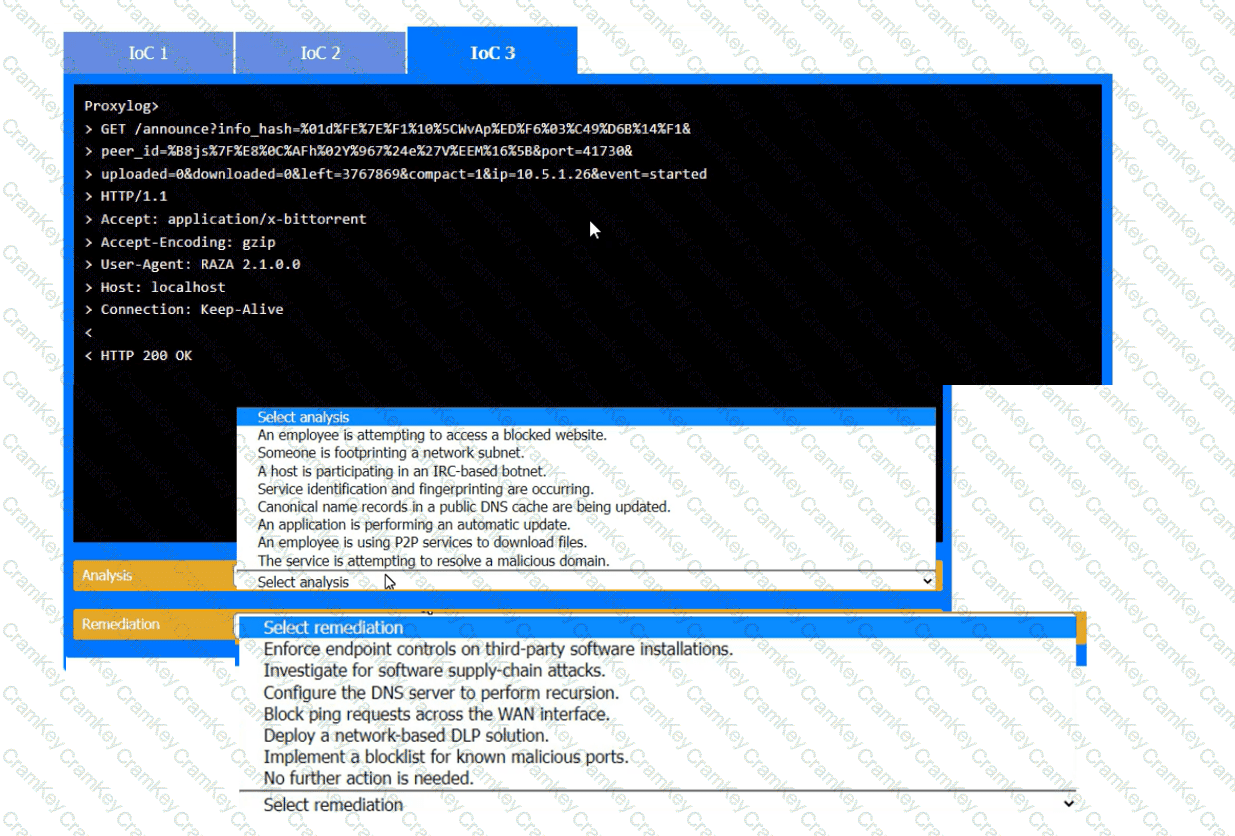
During the course of normal SOC operations, three anomalous events occurred and were flagged as potential IoCs. Evidence for each of these potential IoCs is provided.

INSTRUCTIONS

Review each of the events and select the appropriate analysis and remediation options for each IoC.
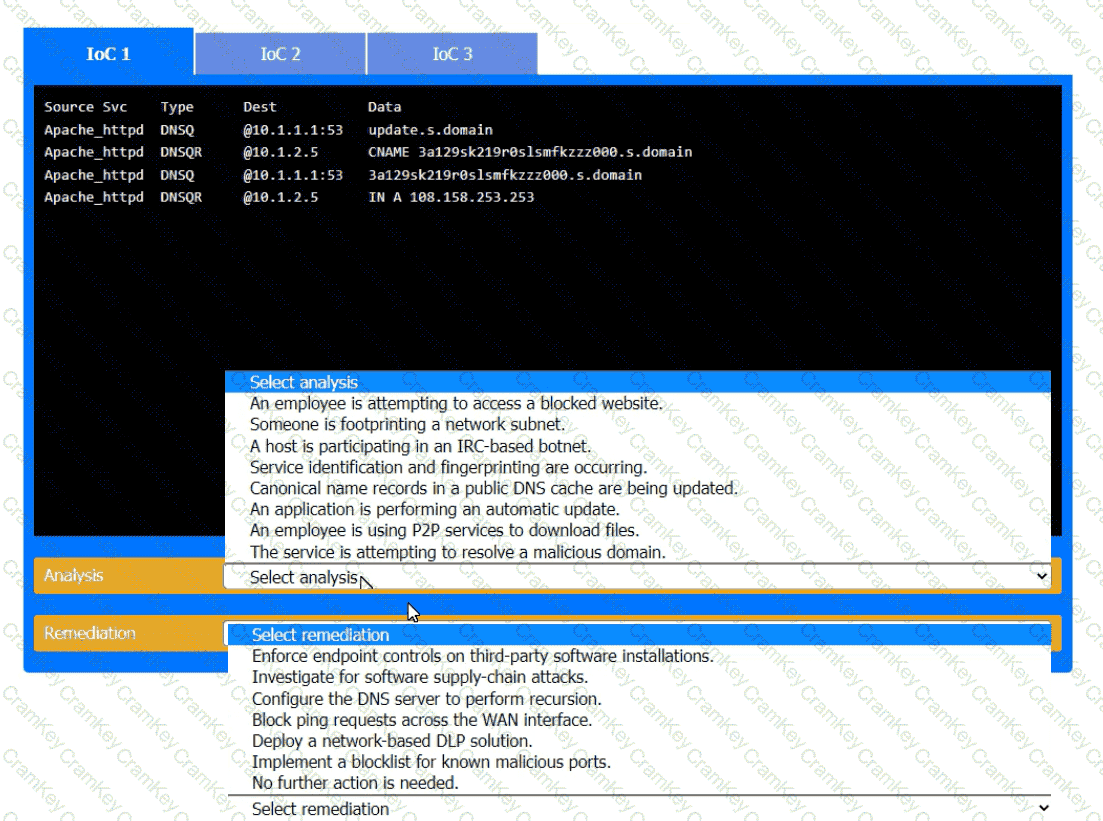
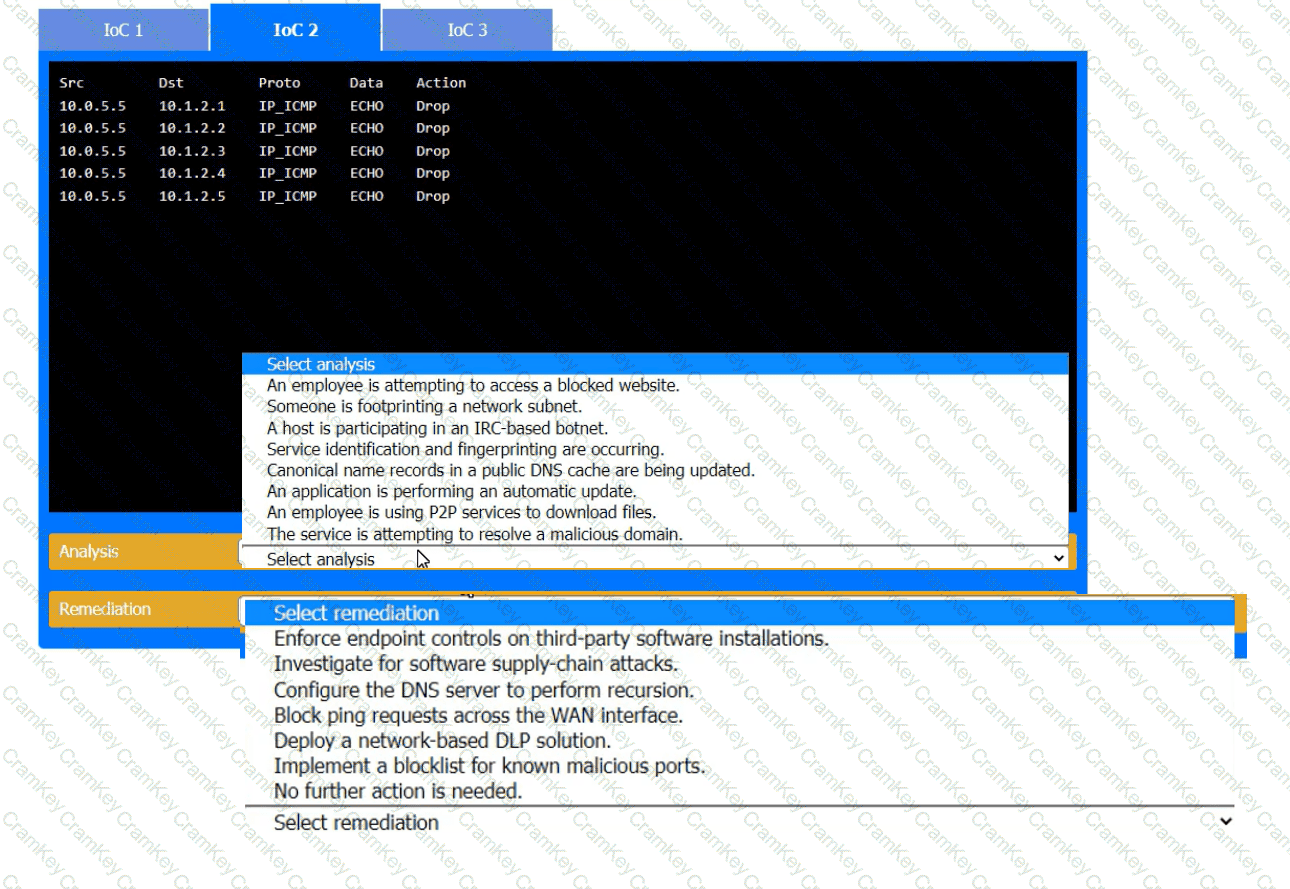
Questions 4

Questions 4

Questions 4

Options:

Discussion 0
Kylo
What makes Cramkey Dumps so reliable? Please guide.
Sami Oct 20, 2026
Well, for starters, they have a team of experts who are constantly updating their material to reflect the latest changes in the industry. Plus, they have a huge database of questions and answers, which makes it easy to study and prepare for the exam.
Billy
It was like deja vu! I was confident going into the exam because I had already seen those questions before.
Vincent Oct 1, 2026
Definitely. And the best part is, I passed! I feel like all that hard work and preparation paid off. Cramkey is the best resource for all students!!!
Mylo
Excellent dumps with authentic information… I passed my exam with brilliant score.
Dominik Oct 12, 2026
That's amazing! I've been looking for good study material that will help me prepare for my upcoming certification exam. Now, I will try it.
Marley
Hey, I heard the good news. I passed the certification exam!
Jaxson Oct 1, 2026
Yes, I passed too! And I have to say, I couldn't have done it without Cramkey Dumps.
Everleigh
I must say that they are updated regularly to reflect the latest exam content, so you can be sure that you are getting the most accurate information. Plus, they are easy to use and understand, so even new students can benefit from them.
Huxley Oct 10, 2026
That's great to know. So, you think new students should buy these dumps?
Questions 5

As part of a security audit in the software development life cycle, a product manager must demonstrate and provide evidence of a complete representation of the code and modules used within the production-deployed application prior to the build. Which of the following best provides the required evidence?

Options:

A.  

Software composition analysis

B.  

Runtime application inspection

C.  

Static application security testing

D.  

Interactive application security testing

Discussion 0
Title
Questions
Posted

CAS-005
PDF

$27.5  $109.99

CAS-005 Testing Engine

$32.5  $129.99

CAS-005 PDF + Testing Engine

$42.5  $169.99