Month End Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: mystc75

CompTIA Updated CAS-005 Exam Questions and Answers by romie

Page: 8 / 25

CompTIA CAS-005 Exam Overview :

Exam Name: CompTIA SecurityX Certification Exam
Exam Code: CAS-005 Dumps
Vendor: CompTIA Certification: CompTIA CASP
Questions: 344 Q&A's Shared By: romie
Question 32

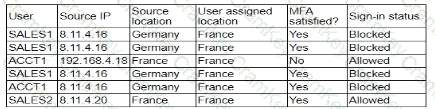
A security analyst is troubleshooting the reason a specific user is having difficulty accessing company resources The analyst reviews the following information:
Questions 32

Which of the following is most likely the cause of the issue?

Options:

A.

The local network access has been configured tobypass MFA requirements.

B.

A network geolocation is being misidentified by the authentication server

C.

Administrator access from an alternate location is blocked by company policy

D.

Several users have not configured their mobile devices toreceive OTP codes

Discussion
Question 33

A company isolated its OT systems from other areas of the corporate network These systems are required to report usage information over the internet to the vendor Which oi the following b*st reduces the risk of compromise or sabotage ' (Select two).

Options:

A.

Implementing allow lists

B.

Monitoring network behavior

C.

Encrypting data at rest

D.

Performing boot Integrity checks

E.

Executing daily health checks

F.

Implementing a site-to-site IPSec VPN

Discussion
Erik
Hey, I have passed my exam using Cramkey Dumps?
Freyja Sep 15, 2026
Really, what are they? All come in your pool? Please give me more details, I am going to have access their subscription. Please brother, give me more details.
Neve
Will I be able to achieve success after using these dumps?
Rohan Sep 25, 2026
Absolutely. It's a great way to increase your chances of success.
Amy
I passed my exam and found your dumps 100% relevant to the actual exam.
Lacey Sep 5, 2026
Yeah, definitely. I experienced the same.
Syeda
I passed, Thank you Cramkey for your precious Dumps.
Stella Sep 19, 2026
That's great. I think I'll give Cramkey Dumps a try.
Everleigh
I must say that they are updated regularly to reflect the latest exam content, so you can be sure that you are getting the most accurate information. Plus, they are easy to use and understand, so even new students can benefit from them.
Huxley Sep 11, 2026
That's great to know. So, you think new students should buy these dumps?
Question 34

Engineers at a cloud service provider can now access newly deployed customer environments from their personal laptops. The engineers are concerned that unmanaged systems may present unknown vulnerabilities to customer environments, which might become a significant liability to the service provider. Which of the following deployments provides the most secure solution to prevent access through non-authorized endpoints?

Options:

A.

Modifying MDM policies to provide device attestation on all devices connecting to the cloud service ' s management console

B.

Requiring that a corporate-licensed and -managed EDR solution is installed on employee-owned laptops

C.

Configuring the device ' s certificate-based authentication on the corporate VPN and requiring that all activity in customer environments be performed using the VPN

D.

Implementing host checking on remote desktop sessions to jump boxes used for managing customer environments

Discussion
Question 35

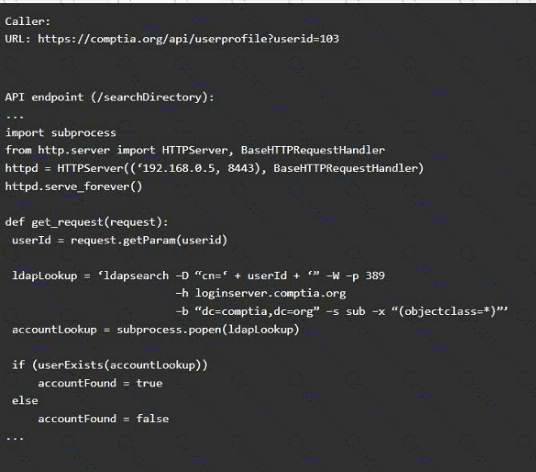
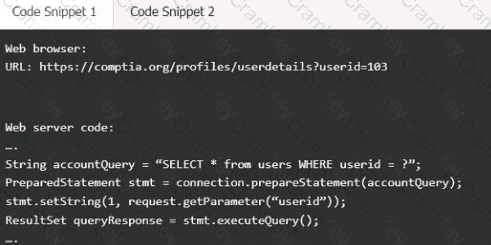
A product development team has submitted code snippets for review prior to release.

INSTRUCTIONS

Analyze the code snippets, and then select one vulnerability, and one fix for each code snippet.

Code Snippet 1
Questions 35

Code Snippet 2

Questions 35

Vulnerability 1:

SQL injection

Cross-site request forgery

Server-side request forgery

Indirect object reference

Cross-site scripting

Fix 1:

Perform input sanitization of the userid field.

Perform output encoding of queryResponse,

Ensure usex:ia belongs to logged-in user.

Inspect URLS and disallow arbitrary requests.

Implementanti-forgery tokens.

Vulnerability 2

1) Denial of service

2) Command injection

3) SQL injection

4) Authorization bypass

5) Credentials passed via GET

Fix 2

A) Implement prepared statements and bind

variables.

B) Remove the serve_forever instruction.

C) Prevent the " authenticated " value from being overridden by a GET parameter.

D) HTTP POST should be used for sensitive parameters.

E) Perform input sanitization of the userid field.

Options:

Discussion
Page: 8 / 25
Title
Questions
Posted

CAS-005
PDF

$26.25  $104.99

CAS-005 Testing Engine

$31.25  $124.99

CAS-005 PDF + Testing Engine

$41.25  $164.99