Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

CompTIA Updated CAS-005 Exam Questions and Answers by carmen

Page: 17 / 25

CompTIA CAS-005 Exam Overview :

Exam Name: CompTIA SecurityX Certification Exam
Exam Code: CAS-005 Dumps
Vendor: CompTIA Certification: CompTIA CASP
Questions: 361 Q&A's Shared By: carmen
Question 68

A security engineer receives an alert from the SIEM platform indicating a possible malicious action on the internal network. The engineer generates a report that outputs the logs associated with the incident:
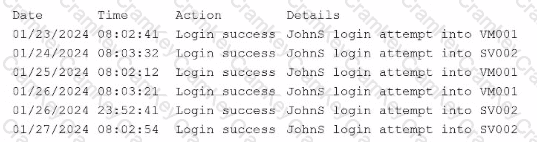
Questions 68

Which of the following actions best enables the engineer to investigate further?

Options:

A.

Consulting logs from the enterprise password manager

B.

Searching dark web monitoring resources for exposure

C.

Reviewing audit logs from privileged actions

D.

Querying user behavior analytics data

Discussion
Question 69

A company discovers intellectual property data on commonly known collaboration web applications that allow the use of slide templates. The systems administrator is reviewing the configurations of each tool to determine how to prevent this issue. The following security solutions are deployed:

    CASB

    SASE

    WAF

    EDR

    Firewall

    IDS

    SIEM

    DLP endpoints

Which of the following should the administrator do to address the issue?

Options:

A.

Enable blocking for all WAF policies.

B.

Enforce a policy to block unauthorized web applications within CASB.

C.

Create an alert within the SIEM for outgoing network traffic to the suspected website.

D.

Configure DLP endpoints to block sensitive data to removable storage.

Discussion
Question 70

An organization is increasing its focus on training that addresses new social engineering and phishing attacks. Which of the following is the organization most concerned about?

Options:

A.

Meeting existing regulatory compliance

B.

Overreliance on AI support bots

C.

Generative AI tools increasing the quality of exploits

D.

Differential analysis using AI models

Discussion
Sarah
Yeah, I was so relieved when I saw that the question appeared in the exam were similar to their exam dumps. It made the exam a lot easier and I felt confident going into it.
Aaliyah Oct 28, 2026
Same here. I've heard mixed reviews about using exam dumps, but for us, it definitely paid off.
Stefan
Thank you so much Cramkey I passed my exam today due to your highly up to date dumps.
Ocean Oct 12, 2026
Agree….Cramkey Dumps are constantly updated based on changes in the exams. They also have a team of experts who regularly review the materials to ensure their accuracy and relevance. This way, you can be sure you're studying the most up-to-date information available.
Vienna
I highly recommend them. They are offering exact questions that we need to prepare our exam.
Jensen Oct 3, 2026
That's great. I think I'll give Cramkey a try next time I take a certification exam. Thanks for the recommendation!
Aryan
Absolutely rocked! They are an excellent investment for anyone who wants to pass the exam on the first try. They save you time and effort by providing a comprehensive overview of the exam content, and they give you a competitive edge by giving you access to the latest information. So, I definitely recommend them to new students.
Jessie Oct 23, 2026
did you use PDF or Engine? Which one is most useful?
Question 71

A security engineer needs to remediate a SWEET32 vulnerability in an OpenSSH-based application and review existing configurations. Which of the following should the security engineer do? (Select two.)

Options:

A.

Disable Twofish algorithms

B.

cat /etc/ashd/ash_config | grep " HMAC "

C.

Disable RSA algorithms

D.

cat /etc/sshd/ssh_config | grep " PermitRootLogin "

E.

Disable 3DES algorithms

F.

cat /etc/sshd/ssh_config | grep " Ciphers "

Discussion
Page: 17 / 25
Title
Questions
Posted

CAS-005
PDF

$27.5  $109.99

CAS-005 Testing Engine

$32.5  $129.99

CAS-005 PDF + Testing Engine

$42.5  $169.99

