Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

Fortinet Updated NSE4_FGT-7.2 Exam Questions and Answers by claire

Page: 6 / 12

Fortinet NSE4_FGT-7.2 Exam Overview :

Exam Name: Fortinet NSE 4 - FortiOS 7.2
Exam Code: NSE4_FGT-7.2 Dumps
Vendor: Fortinet Certification: NSE4
Questions: 170 Q&A's Shared By: claire
Question 24

An administrator wants to configure Dead Peer Detection (DPD) on IPSEC VPN for detecting dead tunnels. The requirement is that FortiGate sends DPD probes only when no traffic is observed in the tunnel.

Which DPD mode on FortiGate will meet the above requirement?

Options:

A.

Disabled

B.

On Demand

C.

Enabled

D.

On Idle

Discussion
Annabel
I recently used them for my exam and I passed it with excellent score. I am impressed.
Amirah Sep 4, 2026
I passed too. The questions I saw in the actual exam were exactly the same as the ones in the Cramkey Dumps. I was able to answer the questions confidently because I had already seen and studied them.
Pippa
I was so happy to see that almost all the questions on the exam were exactly what I found in their Dumps.
Anastasia Sep 23, 2026
You are right…It was amazing! The Cramkey Dumps were so comprehensive and well-organized, it made studying for the exam a breeze.
Addison
Want to tell everybody through this platform that I passed my exam with excellent score. All credit goes to Cramkey Exam Dumps.
Libby Sep 19, 2026
That's good to know. I might check it out for my next IT certification exam. Thanks for the info.
Ayra
How these dumps are necessary for passing the certification exam?
Damian Sep 15, 2026
They give you a competitive edge and help you prepare better.
Question 25

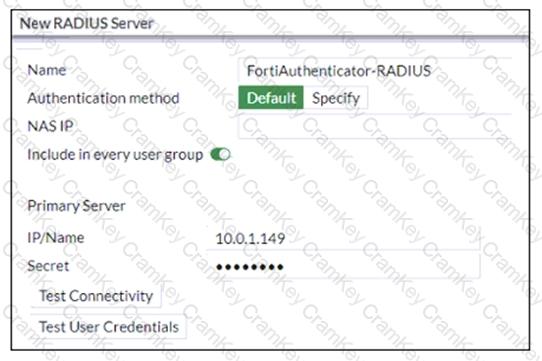
Refer to the exhibit.

An administrator added a configuration for a new RADIUS server. While configuring, the administrator selected the Include in every user group option.
Questions 25

What is the impact of using the Include in every user group option in a RADIUS configuration?

Options:

A.

This option places the RADIUS server, and all users who can authenticate against that server, into every FortiGate user group.

B.

This option places all FortiGate users and groups required to authenticate into the RADIUS server, which, in this case, is FortiAuthenticator.

C.

This option places all users into every RADIUS user group, including groups that are used for the LDAP server on FortiGate.

D.

This option places the RADIUS server, and all users who can authenticate against that server, into every RADIUS group.

Discussion
Question 26

44

Which statement about the policy ID number of a firewall policy is true?

Options:

A.

It is required to modify a firewall policy using the CLI.

B.

It represents the number of objects used in the firewall policy.

C.

It changes when firewall policies are reordered.

D.

It defines the order in which rules are processed.

Discussion
Question 27

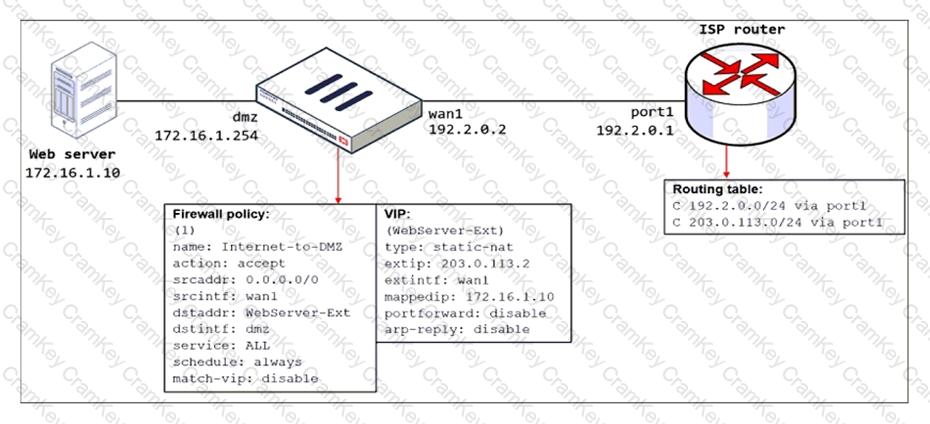
Refer to the exhibit.

The exhibit shows a diagram of a FortiGate device connected to the network, the firewall policy and VIP configuration on the FortiGate device, and the routing table on the ISP router.

When the administrator tries to access the web server public address (203.0.113.2) from the internet, the connection times out. At the same time, the administrator runs a sniffer on FortiGate to capture incoming web traffic to the server and does not see any output.
Questions 27

Based on the information shown in the exhibit, what configuration change must the administrator make to fix the connectivity issue?

Options:

A.

Configure a loopback interface with address 203.0.113.2/32.

B.

In the VIP configuration, enable arp-reply.

C.

Enable port forwarding on the server to map the external service port to the internal service port.

D.

In the firewall policy configuration, enable match-vip.

Discussion
Page: 6 / 12

NSE4_FGT-7.2
PDF

$36.75  $104.99

NSE4_FGT-7.2 Testing Engine

$43.75  $124.99

NSE4_FGT-7.2 PDF + Testing Engine

$57.75  $164.99

