Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

Cisco Updated 300-215 Exam Questions and Answers by rares

Page: 2 / 9

Cisco 300-215 Exam Overview :

Exam Name: Conducting Forensic Analysis and Incident Response Using Cisco CyberOps Technologies (CBRFIR v1.2)
Exam Code: 300-215 Dumps
Vendor: Cisco Certification: CyberOps Professional
Questions: 184 Q&A's Shared By: rares
Question 8

Which scripts will search a log file for the IP address of 192.168.100.100 and create an output file named parsed_host.log while printing results to the console?
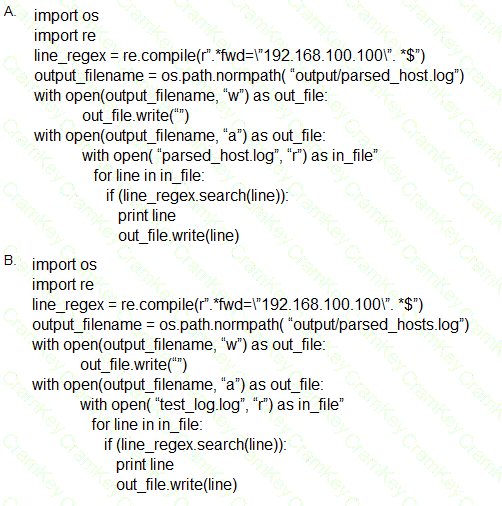
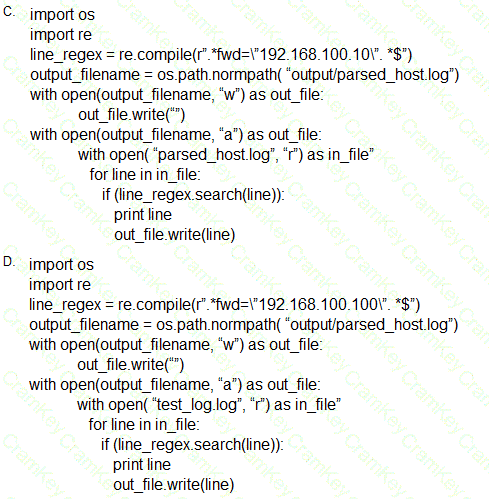
Questions 8

Questions 8

Options:

A.

Option A

B.

Option B

C.

Option C

D.

Option D

Discussion
Question 9

During an overnight shift, a cybersecurity team at a global trading firm detects irregular activity The network intrusion system flags an encrypted traffic spike from high-value transaction servers to an anonymous Tor exit node Simultaneously, internal surveillance tools report unusual database queries and access patterns resembling exfiltration techniques Which focused action should the team take first to analyze and address these potential security threats?

Options:

A.

Initiate immediate containment protocols tor transaction servers.

B.

Implement dynamic firewall rules to block suspicious outbound connections

C.

Cross-reference database access logs with user activity profiles

D.

Engage advanced decryption and anomaly analysis for the flagged traffic

Discussion
Nylah
I've been looking for good study material for my upcoming certification exam. Need help.
Dolly Oct 13, 2026
Then you should definitely give Cramkey Dumps a try. They have a huge database of questions and answers, making it easy to study and prepare for the exam. And the best part is, you can be sure the information is accurate and relevant.
Anaya
I found so many of the same questions on the real exam that I had already seen in the Cramkey Dumps. Thank you so much for making exam so easy for me. I passed it successfully!!!
Nina Oct 18, 2026
It's true! I felt so much more confident going into the exam because I had already seen and understood the questions.
Atlas
What are these Dumps? Would anybody please explain it to me.
Reign Oct 22, 2026
These are exam dumps for a variety of IT certifications. They have a vast collection of updated questions and answers, which are very helpful in preparing for the exams.
Victoria
Hey, guess what? I passed the certification exam! I couldn't have done it without Cramkey Dumps.
Isabel Oct 13, 2026
Same here! I was so surprised when I saw that almost all the questions on the exam were exactly what I found in their study materials.
Melody
My experience with Cramkey was great! I was surprised to see that many of the questions in my exam appeared in the Cramkey dumps.
Colby Oct 22, 2026
Yes, In fact, I got a score of above 85%. And I attribute a lot of my success to Cramkey's dumps.
Question 10

A threat actor has successfully attacked an organization and gained access to confidential files on a laptop. What plan should the organization initiate to contain the attack and prevent it from spreading to other network devices?

Options:

A.

root cause

B.

intrusion prevention

C.

incident response

D.

attack surface

Discussion
Question 11

An organization experienced a sophisticated phishing attack that resulted in the compromise of confidential information from thousands of user accounts. The threat actor used a land and expand approach, where initially accessed account was used to spread emails further. The organization's cybersecurity team must conduct an in-depth root cause analysis to uncover the central factor or factors responsible for the success of the phishing attack. The very first victim of the attack was user with email 500236186@test.com. The primary objective is to formulate effective strategies for preventing similar incidents in the future. What should the cybersecurity engineer prioritize in the root cause analysis report to demonstrate the underlying cause of the incident?

Options:

A.

investigation into the specific vulnerabilities or weaknesses in the organization's email security systems that were exploited by the attackers

B.

evaluation of the organization's incident response procedures and the performance of the incident response team

C.

examination of the organization's network traffic logs to identify patterns of unusual behavior leading up to the attack

D.

comprehensive analysis of the initial user for presence of an insider who gained monetary value by allowing the attack to happen

Discussion
Page: 2 / 9

300-215
PDF

$34.5  $114.99

300-215 Testing Engine

$40.5  $134.99

300-215 PDF + Testing Engine

$52.5  $174.99

