Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

Page: 1 / 10

CyberOps Professional Conducting Forensic Analysis and Incident Response Using Cisco CyberOps Technologies (CBRFIR v1.2)

Conducting Forensic Analysis and Incident Response Using Cisco CyberOps Technologies (CBRFIR v1.2)

Last Update Nov 14, 2026
Total Questions : 184

To help you prepare for the 300-215 Cisco exam, we are offering free 300-215 Cisco exam questions. All you need to do is sign up, provide your details, and prepare with the free 300-215 practice questions. Once you have done that, you will have access to the entire pool of Conducting Forensic Analysis and Incident Response Using Cisco CyberOps Technologies (CBRFIR v1.2) 300-215 test questions which will help you better prepare for the exam. Additionally, you can also find a range of Conducting Forensic Analysis and Incident Response Using Cisco CyberOps Technologies (CBRFIR v1.2) resources online to help you better understand the topics covered on the exam, such as Conducting Forensic Analysis and Incident Response Using Cisco CyberOps Technologies (CBRFIR v1.2) 300-215 video tutorials, blogs, study guides, and more. Additionally, you can also practice with realistic Cisco 300-215 exam simulations and get feedback on your progress. Finally, you can also share your progress with friends and family and get encouragement and support from them.

Questions 2

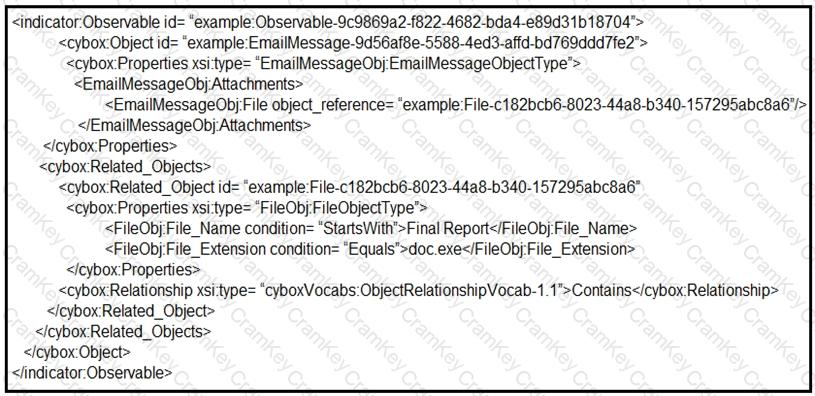
Refer to the exhibit.

Questions 2

Which determination should be made by a security analyst?

Options:

A.  

An email was sent with an attachment named “Grades.doc.exe”.

B.  

An email was sent with an attachment named “Grades.doc”.

C.  

An email was sent with an attachment named “Final Report.doc”.

D.  

An email was sent with an attachment named “Final Report.doc.exe”.

Discussion 0
Alessia
Amazing Dumps. Found almost all questions in actual exam whih I prepared from these valuable dumps. Recommended!!!!
Belle Oct 28, 2026
That's impressive. I've been struggling with finding good study material for my certification. Maybe I should give Cramkey Dumps a try.
Ilyas
Definitely. I felt much more confident and prepared because of the Cramkey Dumps. I was able to answer most of the questions with ease and I think that helped me to score well on the exam.
Saoirse Oct 26, 2026
That's amazing. I'm glad you found something that worked for you. Maybe I should try them out for my next exam.
Stefan
Thank you so much Cramkey I passed my exam today due to your highly up to date dumps.
Ocean Oct 12, 2026
Agree….Cramkey Dumps are constantly updated based on changes in the exams. They also have a team of experts who regularly review the materials to ensure their accuracy and relevance. This way, you can be sure you're studying the most up-to-date information available.
Zayaan
Successfully aced the exam… Thanks a lot for providing amazing Exam Dumps.
Harmony Oct 19, 2026
That's fantastic! I'm glad to hear that their dumps helped you. I also used them and found it accurate.
Kylo
What makes Cramkey Dumps so reliable? Please guide.
Sami Oct 20, 2026
Well, for starters, they have a team of experts who are constantly updating their material to reflect the latest changes in the industry. Plus, they have a huge database of questions and answers, which makes it easy to study and prepare for the exam.
Questions 3

An organization experienced a ransomware attack that resulted in the successful infection of their workstations within their network. As part of the incident response process, the organization's cybersecurity team must prepare a comprehensive root cause analysis report. This report aims to identify the primary factor or factors responsible for the successful ransomware attack and to formulate effective strategies to prevent similar incidents in the future. In this context, what should the cybersecurity engineer emphasize in the root cause analysis report to demonstrate the underlying cause of the incident?

Options:

A.  

evaluation of user awareness and training programs aimed at preventing ransomware attacks

B.  

analysis of the organization's network architecture and security infrastructure

C.  

detailed examination of the ransomware variant, its encryption techniques, and command-and-control servers

D.  

vulnerabilities present in the organization's software and systems that were exploited by the ransomware

Discussion 0
Questions 4

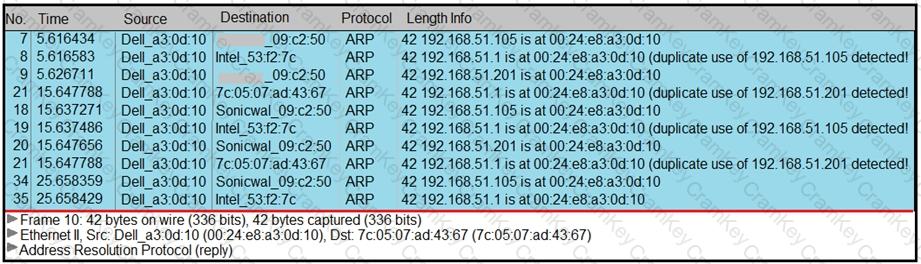
Refer to the exhibit.

Questions 4

A security analyst notices unusual connections while monitoring traffic. What is the attack vector, and which action should be taken to prevent this type of event?

Options:

A.  

DNS spoofing; encrypt communication protocols

B.  

SYN flooding; block malicious packets

C.  

ARP spoofing; configure port security

D.  

MAC flooding; assign static entries

Discussion 0
Questions 5

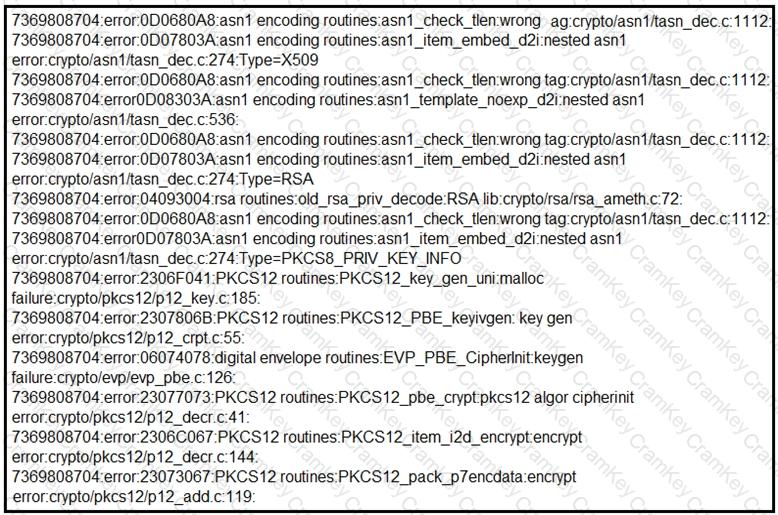
Refer to the exhibit.

Questions 5

What should be determined from this Apache log?

Options:

A.  

A module named mod_ssl is needed to make SSL connections.

B.  

The private key does not match with the SSL certificate.

C.  

The certificate file has been maliciously modified

D.  

The SSL traffic setup is improper

Discussion 0

300-215
PDF

$30  $119.99

300-215 Testing Engine

$35  $139.99

300-215 PDF + Testing Engine

$45  $179.99