Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

Page: 1 / 2

Fortinet Certified Professional Security Operations FCP - FortiSIEM 7.2 Analyst

FCP - FortiSIEM 7.2 Analyst

Last Update Oct 6, 2026
Total Questions : 32

To help you prepare for the FCP_FSM_AN-7.2 Fortinet exam, we are offering free FCP_FSM_AN-7.2 Fortinet exam questions. All you need to do is sign up, provide your details, and prepare with the free FCP_FSM_AN-7.2 practice questions. Once you have done that, you will have access to the entire pool of FCP - FortiSIEM 7.2 Analyst FCP_FSM_AN-7.2 test questions which will help you better prepare for the exam. Additionally, you can also find a range of FCP - FortiSIEM 7.2 Analyst resources online to help you better understand the topics covered on the exam, such as FCP - FortiSIEM 7.2 Analyst FCP_FSM_AN-7.2 video tutorials, blogs, study guides, and more. Additionally, you can also practice with realistic Fortinet FCP_FSM_AN-7.2 exam simulations and get feedback on your progress. Finally, you can also share your progress with friends and family and get encouragement and support from them.

Questions 2

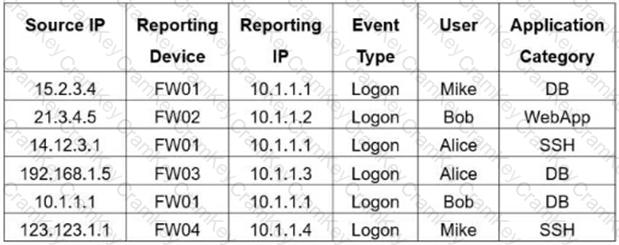
Refer to the exhibit.

Questions 2

If you group the events by Reporting Device, Reporting IP, and Application Category, how many results will FortiSIEM display?

Options:

A.  

Four

B.  

Five

C.  

One

D.  

Six

E.  

Two

Discussion 0
Questions 3

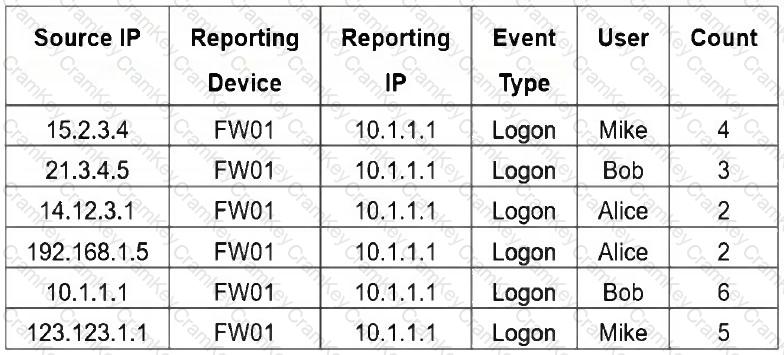
Refer to the exhibit.

Questions 3

If you group the events by User, Source IP, and Count attributes, how many results will FortiSIEM display?

Options:

A.  

Two

B.  

Six

C.  

Three

D.  

Five

E.  

Four

Discussion 0
Questions 4

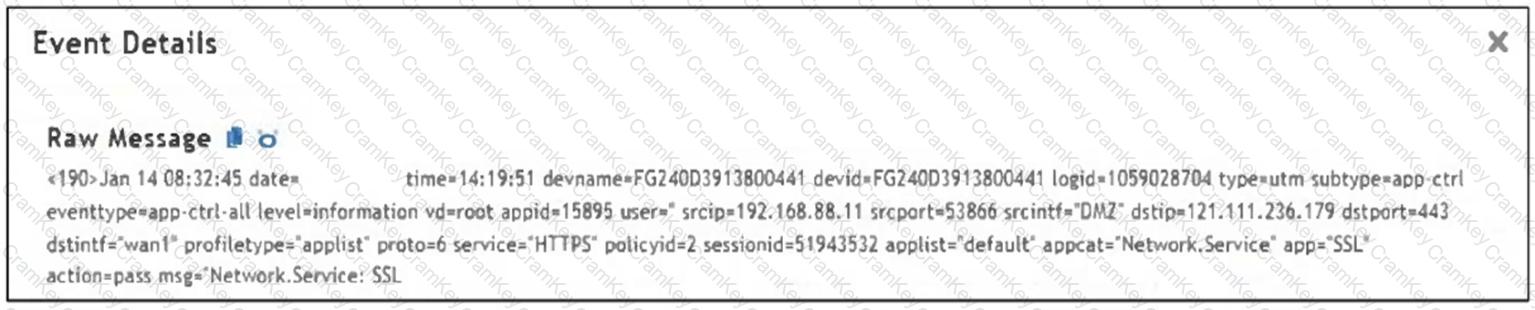
Refer to the exhibit.

Questions 4

Which value would you expect the FortiSIEM parser to use to populate the Application Name field?

Options:

A.  

applist

B.  

Network.Service

C.  

SSL

D.  

wan1

Discussion 0
Questions 5

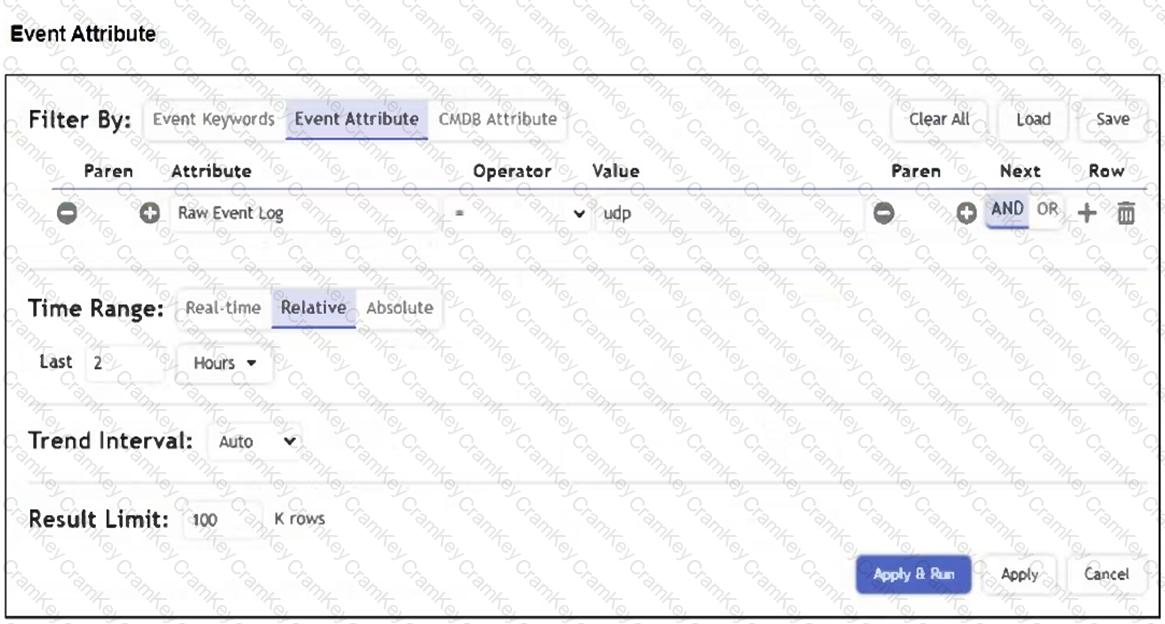
Refer to the exhibit.

Questions 5

A FortiSIEM device is receiving syslog events from a FortiGate firewall. The FortiSIEM analyst is trying to search the raw event logs for the last two hours that contain the keyword "udp". However, they are getting no results from the search, which they know should be available. Based on the filter shown in the exhibit, why are there no search results?

Options:

A.  

The analyst selected AND in the Next column. This is the wrong Boolean operator.

B.  

The Time Range value should be set to Real-Time.

C.  

The keyword is case sensitive. Instead of typing udp in the Value field, the analyst should type UDP.

D.  

The analyst selected = in the Operator column. That is the wrong operator.

Discussion 0
Hassan
Highly Recommended Dumps… today I passed my exam! Same questions appear. I bought Full Access.
Kasper Sep 6, 2026
Hey wonderful….so same questions , sounds good. Planning to write this week, I will go for full access today.
Nadia
Why these dumps are important? Can I pass my exam without these dumps?
Julian Sep 19, 2026
The questions in the Cramkey dumps are explained in detail and there are also study notes and reference materials provided. This made it easier for me to understand the concepts and retain the information better.
Stefan
Thank you so much Cramkey I passed my exam today due to your highly up to date dumps.
Ocean Sep 8, 2026
Agree….Cramkey Dumps are constantly updated based on changes in the exams. They also have a team of experts who regularly review the materials to ensure their accuracy and relevance. This way, you can be sure you're studying the most up-to-date information available.
Peyton
Hey guys. Guess what? I passed my exam. Thanks a lot Cramkey, your provided information was relevant and reliable.
Coby Sep 15, 2026
Thanks for sharing your experience. I think I'll give Cramkey a try for my next exam.
Ayra
How these dumps are necessary for passing the certification exam?
Damian Sep 15, 2026
They give you a competitive edge and help you prepare better.

FCP_FSM_AN-7.2
PDF

$36.75  $104.99

FCP_FSM_AN-7.2 Testing Engine

$43.75  $124.99

FCP_FSM_AN-7.2 PDF + Testing Engine

$57.75  $164.99