Comprehensive and Detailed Explanation
HPE Press guide context | PDF page 679 | HPE Press, Aruba Certified Associate – Campus Access Official Certification Study Guide
Technical Deep Dive — Original Chat Wording
Audit logging provides a historical record of administrative and system activities performed within a network-management platform.
In HPE Aruba Networking Central, the Audit Trail helps administrators identify configuration changes and determine when they occurred.
Audit records can include information such as timestamps, the responsible account, affected devices, operation categories, and descriptions of the changes performed.
For example, an administrator may modify an AP group configuration or update an access-control policy.
The Audit Trail can record the associated management activity, allowing authorized personnel to investigate the change later.
This is particularly useful when troubleshooting a problem that begins after a configuration update.
An engineer can compare the time of the reported problem with relevant administrative events.
Audit records also support accountability and security investigations because they establish a record of management operations.
However, audit logging should not be confused with ordinary network traffic monitoring.
Policy usage statistics describe how traffic matches security or forwarding policies.
Mouse-click activity is not comprehensively recorded as a general-purpose user interaction history.
Report imports may generate particular system events, but they are not the fundamental audit function targeted by the question.
The primary purpose of the Audit Trail is to record administrative activity, including configuration modifications.
Therefore, Option B (Configuration changes) is correct.
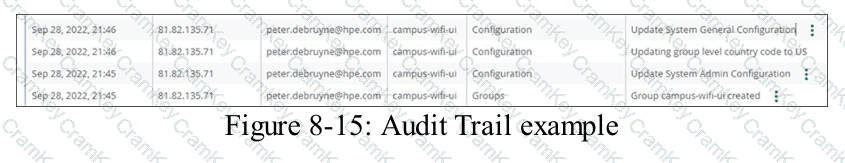
HPE Press study-guide figure / related learning illustration · Q134 Fig 8-15 Audit