Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

ECCouncil Updated ECSAv10 Exam Questions and Answers by aris

Page: 5 / 7

ECCouncil ECSAv10 Exam Overview :

Exam Name: EC-Council Certified Security Analyst (ECSA) v10 : Penetration Testing
Exam Code: ECSAv10 Dumps
Vendor: ECCouncil Certification: ECSA
Questions: 201 Q&A's Shared By: aris
Question 20

STION NO: 23

Identify the framework that comprises of five levels to guide agency assessment of their security programs and assist in prioritizing efforts for improvement:

Options:

A.

Information System Security Assessment Framework (ISSAF)

B.

Microsoft Internet Security Framework

C.

Nortells Unified Security Framework

D.

Federal Information Technology Security Assessment Framework

Discussion
Anaya
I found so many of the same questions on the real exam that I had already seen in the Cramkey Dumps. Thank you so much for making exam so easy for me. I passed it successfully!!!
Nina Oct 18, 2026
It's true! I felt so much more confident going into the exam because I had already seen and understood the questions.
Reeva
Wow what a success I achieved today. Thank you so much Cramkey for amazing Dumps. All students must try it.
Amari Oct 27, 2026
Wow, that's impressive. I'll definitely keep Cramkey in mind for my next exam.
River
Hey, I used Cramkey Dumps to prepare for my recent exam and I passed it.
Lewis Oct 26, 2026
Yeah, I used these dumps too. And I have to say, I was really impressed with the results.
Norah
Cramkey is highly recommended.
Zayan Oct 22, 2026
Definitely. If you're looking for a reliable and effective study resource, look no further than Cramkey Dumps. They're simply wonderful!
Esmae
I highly recommend Cramkey Dumps to anyone preparing for the certification exam.
Mollie Oct 6, 2026
Absolutely. They really make it easier to study and retain all the important information. I'm so glad I found Cramkey Dumps.
Question 21

Before performing the penetration testing, there will be a pre-contract discussion with different pen-testers (the team of penetration testers) to gather a quotation to perform pen testing.
Questions 21

Which of the following factors is NOT considered while preparing a price quote to perform pen testing?

Options:

A.

Total number of employees in the client organization

B.

Type of testers involved

C.

The budget required

D.

Expected time required to finish the project

Discussion
Question 22

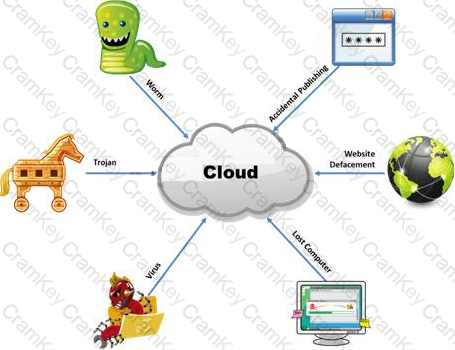
The Internet is a giant database where people store some of their most private information on the cloud, trusting that the service provider can keep it all safe. Trojans, Viruses, DoS attacks, website defacement, lost computers, accidental publishing, and more have all been sources of major leaks over the last 15 years.
Questions 22

What is the biggest source of data leaks in organizations today?

Options:

A.

Weak passwords and lack of identity management

B.

Insufficient IT security budget

C.

Rogue employees and insider attacks

D.

Vulnerabilities, risks, and threats facing Web sites

Discussion
Question 23

N NO: 134

Which of the following is the objective of Gramm-Leach-Bliley Act?

Options:

A.

To ease the transfer of financial information between institutions and banks

B.

To protect the confidentiality, integrity, and availability of data

C.

To set a new or enhanced standards for all U.S. public company boards, management and public accounting firms

D.

To certify the accuracy of the reported financial statement

Discussion
Page: 5 / 7

ECSAv10
PDF

$27.5  $109.99

ECSAv10 Testing Engine

$32.5  $129.99

ECSAv10 PDF + Testing Engine

$42.5  $169.99

