Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

ECCouncil Updated ECSAv10 Exam Questions and Answers by renzo

Page: 3 / 7

ECCouncil ECSAv10 Exam Overview :

Exam Name: EC-Council Certified Security Analyst (ECSA) v10 : Penetration Testing
Exam Code: ECSAv10 Dumps
Vendor: ECCouncil Certification: ECSA
Questions: 201 Q&A's Shared By: renzo
Question 12

Identify the attack represented in the diagram below:
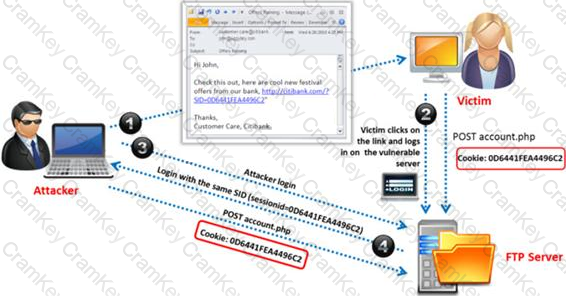
Questions 12

Options:

A.

Input Validation

B.

Session Hijacking

C.

SQL Injection

D.

Denial-of-Service

Discussion
Conor
I recently used these dumps for my exam and I must say, I was impressed with their authentic material.
Yunus Oct 16, 2026
Exactly…….The information in the dumps is so authentic and up-to-date. Plus, the questions are very similar to what you'll see on the actual exam. I felt confident going into the exam because I had studied using Cramkey Dumps.
Hendrix
Great website with Great Exam Dumps. Just passed my exam today.
Luka Oct 8, 2026
Absolutely. Cramkey Dumps only provides the latest and most updated exam questions and answers.
Victoria
Hey, guess what? I passed the certification exam! I couldn't have done it without Cramkey Dumps.
Isabel Oct 13, 2026
Same here! I was so surprised when I saw that almost all the questions on the exam were exactly what I found in their study materials.
Syeda
I passed, Thank you Cramkey for your precious Dumps.
Stella Oct 7, 2026
That's great. I think I'll give Cramkey Dumps a try.
Question 13

Many security and compliance projects begin with a simple idea: assess the organization's risk, vulnerabilities, and breaches. Implementing an IT security risk assessment is critical to the overall security posture of any organization.

An effective security risk assessment can prevent breaches and reduce the impact of realized breaches.
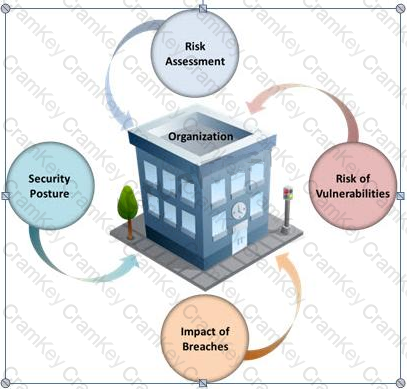
Questions 13

What is the formula to calculate risk?

Options:

A.

Risk = Budget x Time

B.

Risk = Goodwill x Reputation

C.

Risk = Loss x Exposure factor

D.

Risk = Threats x Attacks

Discussion
Question 14

John, the penetration testing manager in a pen testing firm, needs to prepare a pen testing pricing report for a client. Which of the following factors does he need to consider while preparing the pen testing pricing report?
Questions 14

Options:

A.

Number of employees in the client organization

B.

Complete structure of the organization

C.

Number of client computers to be tested and resources required to perform a pen test

D.

Number of servers available in the client organization

Discussion
Question 15

Which of the following is NOT related to the Internal Security Assessment penetration testing strategy?

Options:

A.

Testing to provide a more complete view of site security

B.

Testing focused on the servers, infrastructure, and the underlying software, including the target

C.

Testing including tiers and DMZs within the environment, the corporate network, or partner company connections

D.

Testing performed from a number of network access points representing each logical and physical segment

Discussion
Page: 3 / 7

ECSAv10
PDF

$27.5  $109.99

ECSAv10 Testing Engine

$32.5  $129.99

ECSAv10 PDF + Testing Engine

$42.5  $169.99

