Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

Fortinet Updated NSE4_FGT_AD-7.6 Exam Questions and Answers by hawa

Page: 4 / 6

Fortinet NSE4_FGT_AD-7.6 Exam Overview :

Exam Name: Fortinet NSE 4 - FortiOS 7.6 Administrator
Exam Code: NSE4_FGT_AD-7.6 Dumps
Vendor: Fortinet Certification: Fortinet Network Security Expert
Questions: 95 Q&A's Shared By: hawa
Question 16

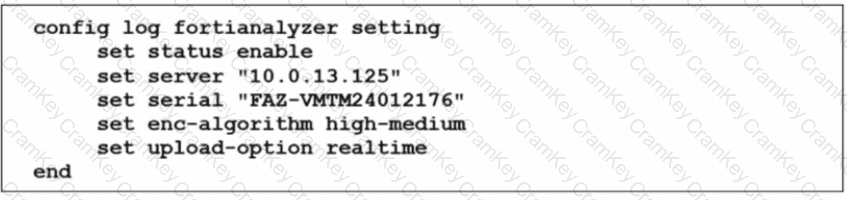
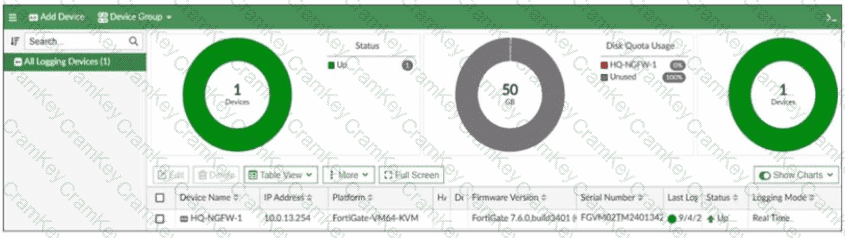
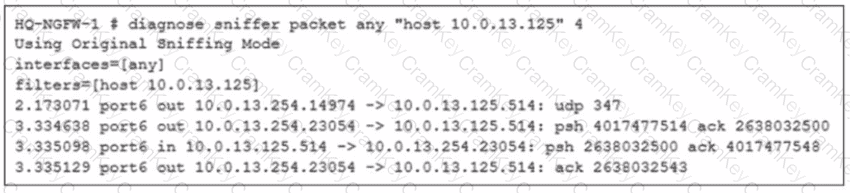
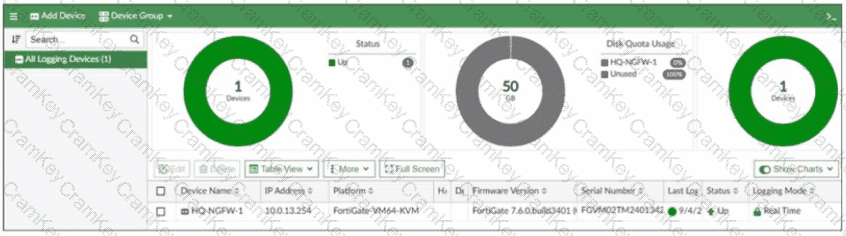
The FortiGate device HQ-NGFW-1 with the IP address 10.0.13.254 sends logs to the FortiAnalyzer device with the IP address 10.0.13.125. The administrator wants to verify that reliable logging is enabled on HQ-NGFW-1.

Which exhibit helps with the verification?

A)
Questions 16

B)

Questions 16

C)

Questions 16

D)

Questions 16

Options:

A.

Option A

B.

Option B

C.

Option C

D.

Option D

Discussion
Question 17

An administrator wanted to configure an IPS sensor to block traffic that triggers the signature set number of times during a specific time period. How can the administrator achieve the objective?

Options:

A.

Use IPS group signatures, set rate-mode 60.

B.

Use IPS packet logging option with periodical filter option.

C.

Use IPS signatures, rate-mode periodical option.

D.

Use IPS filter, rate-mode periodical option.

Discussion
Aryan
Absolutely rocked! They are an excellent investment for anyone who wants to pass the exam on the first try. They save you time and effort by providing a comprehensive overview of the exam content, and they give you a competitive edge by giving you access to the latest information. So, I definitely recommend them to new students.
Jessie Sep 9, 2026
did you use PDF or Engine? Which one is most useful?
Walter
Yayyy!!! I passed my exam with the help of Cramkey Dumps. Highly appreciated!!!!
Angus Sep 16, 2026
YES….. I saw the same questions in the exam.
Miley
Hey, I tried Cramkey Dumps for my IT certification exam. They are really awesome and helped me pass my exam with wonderful score.
Megan Sep 16, 2026
That’s great!!! I’ll definitely give it a try. Thanks!!!
Honey
I highly recommend it. They made a big difference for me and I'm sure they'll help you too. Just make sure to use them wisely and not solely rely on them. They should be used as a supplement to your regular studies.
Antoni Sep 12, 2026
Good point. Thanks for the advice. I'll definitely keep that in mind.
Question 18

Refer to the exhibit.

Questions 18

What can you conclude from the log shown in the exhibit?

Options:

A.

The IPS socket buffer is full and IPS engine needs more memory to create new sessions.

B.

The IPS socket buffer is full and IPS engine cannot decode a packet.

C.

The IPS scan is paused by the IPS diagnostic command with bypass mode option 5.

D.

The IPS session scan is paused and reevaluating the packet because of a dirty flag.

Discussion
Question 19

A network administrator enabled antivirus and selected an SSL inspection profile on a firewall policy. When downloading an EICAR test file through HTTP, FortiGate detects the virus and blocks the file. When downloading the same file through HTTPS, FortiGate does not detect the virus and does not block the file, allowing it to be downloaded. The administrator confirms that the traffic matches the configured firewall policy. What are two reasons for the failed virus detection by FortiGate? (Choose two answers)

Options:

A.

The selected SSL inspection profile has certificate inspection enabled.

B.

The website is exempted from SSL inspection.

C.

The EICAR test file exceeds the protocol options oversize limit.

D.

The browser does not trust the FortiGate self-signed CA certificate.

Discussion
Page: 4 / 6

NSE4_FGT_AD-7.6
PDF

$31.5  $104.99

NSE4_FGT_AD-7.6 Testing Engine

$37.5  $124.99

NSE4_FGT_AD-7.6 PDF + Testing Engine

$49.5  $164.99