Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

CompTIA Updated CS0-004 Exam Questions and Answers by avneet

Page: 2 / 5

CompTIA CS0-004 Exam Overview :

Exam Name: CompTIA Cybersecurity Analyst CySA+ V4 (New Version)
Exam Code: CS0-004 Dumps
Vendor: CompTIA Certification: CompTIA CySA+
Questions: 82 Q&A's Shared By: avneet
Question 8

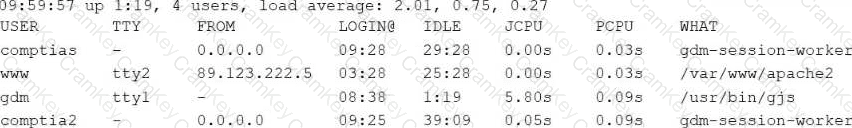
Based on recent alerts, a security analyst thinks a web application server was compromised. The analyst reviews the following server output:
Questions 8

Which of the following best describes what has occurred?

Options:

A.

An initiated unauthorized session

B.

Too many users logged in at the same time

C.

High resource consumption

D.

Abnormal idle times for each user

Discussion
Anaya
I found so many of the same questions on the real exam that I had already seen in the Cramkey Dumps. Thank you so much for making exam so easy for me. I passed it successfully!!!
Nina Oct 18, 2026
It's true! I felt so much more confident going into the exam because I had already seen and understood the questions.
Ernest
That's amazing. I think I'm going to give Cramkey Dumps a try for my next exam. Thanks for telling me about them! CramKey admin please share more questions……You guys are amazing.
Nate Oct 12, 2026
I failed last week, I never know this site , but amazed to see all these questions were in my exam week before. I feel bad now, why I didn’t bother this site. Thanks Cramkey, Excellent Job.
Walter
Yayyy!!! I passed my exam with the help of Cramkey Dumps. Highly appreciated!!!!
Angus Oct 20, 2026
YES….. I saw the same questions in the exam.
Ayra
How these dumps are necessary for passing the certification exam?
Damian Oct 20, 2026
They give you a competitive edge and help you prepare better.
Question 9

Which of the following is the most comprehensive type of report associated with a closed incident?

Options:

A.

Lessons-learned

B.

Situation

C.

Root cause analysis

D.

After action

Discussion
Question 10

An analyst needs to perform a baseline security evaluation of the company's cloud infrastructure.

Which of the following tools is most appropriate for this task?

Options:

A.

Open Vulnerability Assessment Scanner (OpenVAS)

B.

Nikto

C.

ScoutSuite

D.

Metasploit

Discussion
Question 11

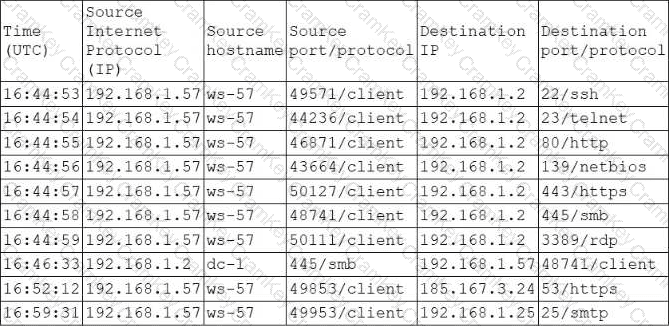
An analyst reviews the following log entries:
Questions 11

Which of the following conclusions should the analyst reach? (Choose two.)

Options:

A.

Host ws-57 is performing a network scan against dc-1.

B.

Domain Controller dc-1 is performing a network scan against ws-57.

C.

Host ws-57 delivered a phishing email via Simple Mail Transfer Protocol.

D.

Host ws-57 is communicating on a service using a non-standard port.

E.

Domain Controller dc-1 is infected with ransomware and initiating connections with ws-57.

F.

Domain Controller dc-1 is communicating using a non-standard port.

Discussion
Page: 2 / 5

CS0-004
PDF

$27.5  $109.99

CS0-004 Testing Engine

$32.5  $129.99

CS0-004 PDF + Testing Engine

$42.5  $169.99

