Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

Page: 1 / 6

CompTIA CySA+ CompTIA Cybersecurity Analyst CySA+ V4 (New Version)

CompTIA Cybersecurity Analyst CySA+ V4 (New Version)

Last Update Nov 17, 2026
Total Questions : 82

To help you prepare for the CS0-004 CompTIA exam, we are offering free CS0-004 CompTIA exam questions. All you need to do is sign up, provide your details, and prepare with the free CS0-004 practice questions. Once you have done that, you will have access to the entire pool of CompTIA Cybersecurity Analyst CySA+ V4 (New Version) CS0-004 test questions which will help you better prepare for the exam. Additionally, you can also find a range of CompTIA Cybersecurity Analyst CySA+ V4 (New Version) resources online to help you better understand the topics covered on the exam, such as CompTIA Cybersecurity Analyst CySA+ V4 (New Version) CS0-004 video tutorials, blogs, study guides, and more. Additionally, you can also practice with realistic CompTIA CS0-004 exam simulations and get feedback on your progress. Finally, you can also share your progress with friends and family and get encouragement and support from them.

Questions 2

Which of the following best describes why operational technology (OT) devices use compensating controls?

Options:

A.  

Industrial control systems use significant network bandwidth.

B.  

Outage windows are usually scheduled.

C.  

Traditional IT security solutions may not be compatible.

D.  

OT devices are typically not encrypted.

Discussion 0
Questions 3

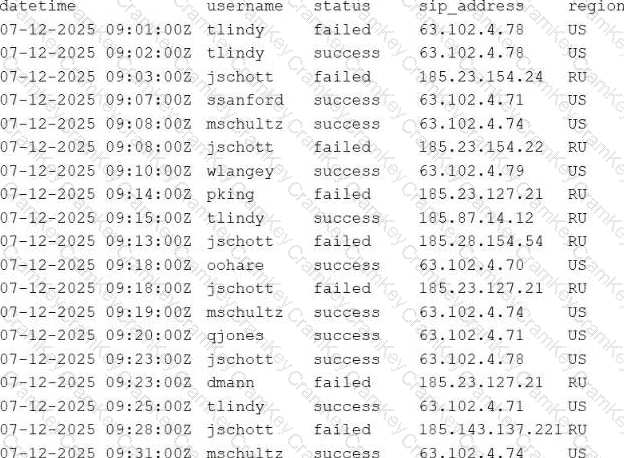
A security analyst analyzes the output of a web application access log for a company based in the United States.

Given the following output:
Questions 3

Which of the following users should be investigated first?

Options:

A.  

jschott

B.  

dmann

C.  

mschultz

D.  

tlindy

Discussion 0
Questions 4

A Chief Information Security Officer (CISO) is notified of an ongoing incident.

Which of the following explains why the CISO instructs the Chief Executive Officer not to discuss the incident over email?

Options:

A.  

The security team discovered a vulnerability in the Short Message Service email gateway.

B.  

The email system may be compromised.

C.  

Emails are not encrypted in transit.

D.  

The CISO has not notified the public relations team of the incident.

Discussion 0
Esmae
I highly recommend Cramkey Dumps to anyone preparing for the certification exam.
Mollie Oct 6, 2026
Absolutely. They really make it easier to study and retain all the important information. I'm so glad I found Cramkey Dumps.
Rae
I tried using Cramkey dumps for my recent certification exam and I found them to be more accurate and up-to-date compared to other dumps I've seen. Passed the exam with wonderful score.
Rayyan Oct 10, 2026
I see your point. Thanks for sharing your thoughts. I might give it a try for my next certification exam.
Alaya
Best Dumps among other dumps providers. I like it so much because of their authenticity.
Kaiden Oct 22, 2026
That's great. I've used other dump providers in the past and they were often outdated or had incorrect information. This time I will try it.
Ilyas
Definitely. I felt much more confident and prepared because of the Cramkey Dumps. I was able to answer most of the questions with ease and I think that helped me to score well on the exam.
Saoirse Oct 26, 2026
That's amazing. I'm glad you found something that worked for you. Maybe I should try them out for my next exam.
Cody
I used Cramkey Dumps to prepare and a lot of the questions on the exam were exactly what I found in their study materials.
Eric Oct 3, 2026
Really? That's great to hear! I used Cramkey Dumps too and I had the same experience. The questions were almost identical.
Questions 5

An analyst prepares an after action report following an incident in which multiple systems were compromised over several days.

The analyst provides raw event logs from each compromised system in the report and determines that a patient-zero system cannot be found.

Which of the following should the analyst do to determine the patient-zero system?

Options:

A.  

Establish an accurate timeline of events.

B.  

Enable monitoring on the compromised systems.

C.  

Isolate the compromised systems before remediation.

D.  

Improve the content for incident updates during shift handoff.

E.  

Perform a reverse composition analysis on malware packages.

Discussion 0

CS0-004
PDF

$27.5  $109.99

CS0-004 Testing Engine

$32.5  $129.99

CS0-004 PDF + Testing Engine

$42.5  $169.99

