Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

Page: 1 / 8

Cybersecurity Defense Analyst Splunk Certified Cybersecurity Defense Engineer

Splunk Certified Cybersecurity Defense Engineer

Last Update Sep 21, 2026
Total Questions : 105

To help you prepare for the SPLK-5002 Splunk exam, we are offering free SPLK-5002 Splunk exam questions. All you need to do is sign up, provide your details, and prepare with the free SPLK-5002 practice questions. Once you have done that, you will have access to the entire pool of Splunk Certified Cybersecurity Defense Engineer SPLK-5002 test questions which will help you better prepare for the exam. Additionally, you can also find a range of Splunk Certified Cybersecurity Defense Engineer resources online to help you better understand the topics covered on the exam, such as Splunk Certified Cybersecurity Defense Engineer SPLK-5002 video tutorials, blogs, study guides, and more. Additionally, you can also practice with realistic Splunk SPLK-5002 exam simulations and get feedback on your progress. Finally, you can also share your progress with friends and family and get encouragement and support from them.

Questions 2

Below is an example of a Sysmon process create log. Which EventCode would be associated with this log entry?
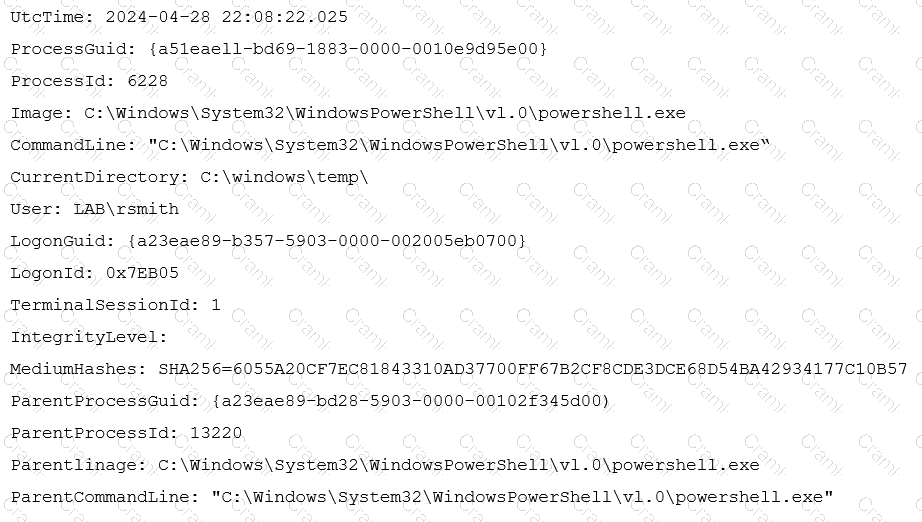
Questions 2

Options:

A.  

EventCode=1

B.  

EventCode=4

C.  

EventCode=3

D.  

EventCode=2

Discussion 0
Questions 3

In a Risk-Based Alerting implementation with Splunk Enterprise Security, which of the following best describes a risk factor?

Options:

A.  

A multiplier of risk that depends on the characteristics of the specific user or asset.

B.  

An event that modifies risk based on the characteristics of the specific user or asset.

C.  

A tool to enable risk data model acceleration.

D.  

A SOAR action that is drawn from annotations.

Discussion 0
Questions 4

What framework in Enterprise Security allows engineers to build detections using known malicious IOCs, comparing them to event logs to find suspicious behavior?

Options:

A.  

Asset & Intelligence Framework

B.  

Incident Management Framework

C.  

Threat Intelligence Framework

D.  

OSINT Framework

Discussion 0
Miriam
Highly recommended Dumps. 100% authentic and reliable. Passed my exam with wonderful score.
Milan Aug 14, 2026
I see. Thanks for the information. I'll definitely keep Cramkey in mind for my next exam.
Rae
I tried using Cramkey dumps for my recent certification exam and I found them to be more accurate and up-to-date compared to other dumps I've seen. Passed the exam with wonderful score.
Rayyan Aug 8, 2026
I see your point. Thanks for sharing your thoughts. I might give it a try for my next certification exam.
Neve
Will I be able to achieve success after using these dumps?
Rohan Aug 8, 2026
Absolutely. It's a great way to increase your chances of success.
Norah
Cramkey is highly recommended.
Zayan Aug 17, 2026
Definitely. If you're looking for a reliable and effective study resource, look no further than Cramkey Dumps. They're simply wonderful!
Questions 5

How can you incorporate additional context into notable events generated by correlation searches?

Options:

A.  

By adding enriched fields during search execution

B.  

By using the dedup command in SPL

C.  

By configuring additional indexers

D.  

By optimizing the search head memory

Discussion 0

SPLK-5002
PDF

$36.75  $104.99

SPLK-5002 Testing Engine

$43.75  $124.99

SPLK-5002 PDF + Testing Engine

$57.75  $164.99

